 abc13.com
Vandalism of Flock Cameras Linked to Epstein Files Demand
Article Content

- •Two Flock cameras were cut down in Cypress, Texas, with a message about Epstein.
- •The vandalism is part of a broader backlash against surveillance technology.
- •Local authorities are investigating the incident amid rising concerns about privacy.
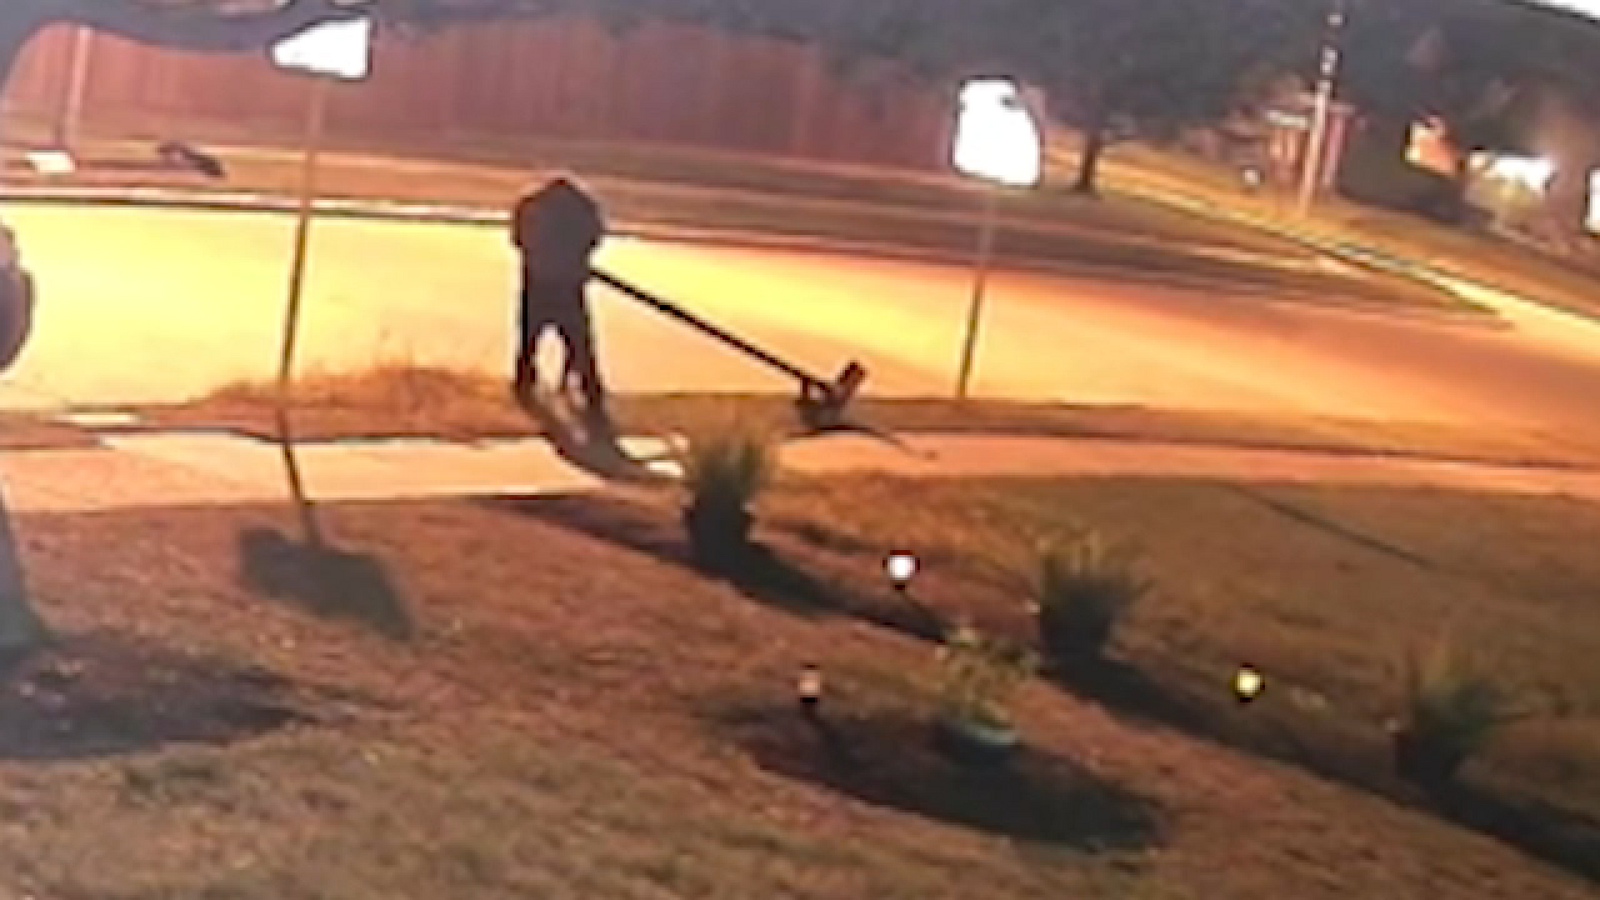
On November 3, 2026, two Flock surveillance cameras were vandalized in Cypress, Texas, with a message demanding the release of the Epstein files. The vandal, captured on surveillance footage, used a power tool to cut down the cameras, which are known for reading license plates. The incident has raised concerns among local residents about safety and the role of surveillance technology in crime prevention. Critics have previously highlighted issues with Flock cameras, including misuse by law enforcement. The Harris County Precinct 5 Constable’s Office is investigating the vandalism. Local resident Jeff Sciba expressed mixed feelings about the cameras, noting their importance in crime deterrence. The vandalism reflects ongoing debates about privacy and surveillance in American communities.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Following this threat?
Track Flock Safety in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What happened to the Flock cameras?
Who is investigating the vandalism?
What are the community's views on Flock cameras?
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 Critical RCE Vulnerability in Prefab UI Disclosed A critical remote code execution vulnerability, CVE-2026-120338, was disclosed on November 1, 2026, affecting Prefab UI's Generative UI sandbox. The flaw allows attackers to execute arbitrary Python code by exploiting Deno's permissions, enabling file read/write access on the host server. This vulnerability affects…