 Cryptonews
Website Challenges Hackers to Steal Bitcoin with PHP Vulnerabilities
Article Content

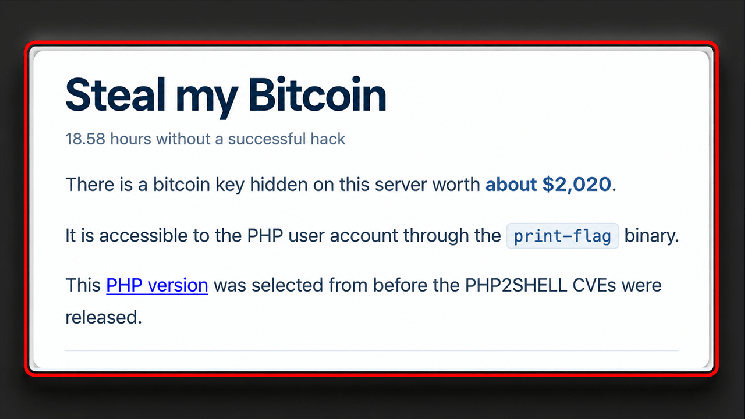
- •Steal My Bitcoin offers a $2,000 bounty for exploiting PHP vulnerabilities.
- •CVE-2026-109618 and CVE-2026-109619 are critical vulnerabilities with a CVSS score of 9.2.
- •No successful exploitation has occurred after 17 hours, raising questions about the challenge's legitimacy.
A website named Steal My Bitcoin is offering a $2,000 bounty for successfully exploiting a deliberately vulnerable PHP installation. Despite the challenge being live for over 17 hours, no one has claimed the prize. The vulnerabilities, CVE-2026-109618 and CVE-2026-109619, were published on October 21, 2026, and are rated as critical with a CVSS score of 9.2. However, an analysis suggests that the server's configuration may prevent exploitation of these vulnerabilities. Participants are restricted to attacking only the web application and PHP container, while other methods are forbidden. The challenge has raised questions about whether it is genuinely exploitable or if it is rigged. As of now, the Bitcoin wallet remains untouched.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Following this threat?
Track CVE-2026-109618 in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What vulnerabilities are involved?
Why hasn't anyone claimed the bounty?
What are the rules for participation?
Continue Reading
 Lazarus Group Linked to PHP Vulnerability Exploitation Plans A cybersecurity report from Cyfirma indicates that a group suspected to be linked to North Korea's Lazarus Group is preparing to exploit critical vulnerabilities in PHP, specifically CVE-2026-109618 and CVE-2026-109619, which allow unauthenticated remote code execution. The attackers, communicating in Korean, are…
 Japan Issues Warning Over Critical PHP Vulnerabilities Affecting Government Sites Japanese Prime Minister Sanae Takaichi announced critical vulnerabilities in the PHP programming language, widely used on government and commercial websites. The vulnerabilities, CVE-2026-109619 and CVE-2026-109618, both rated CVSS 9.2, were disclosed on October 21, 2026, with proof-of-concept code for CVE-2026-109618…