 Interestingengineering
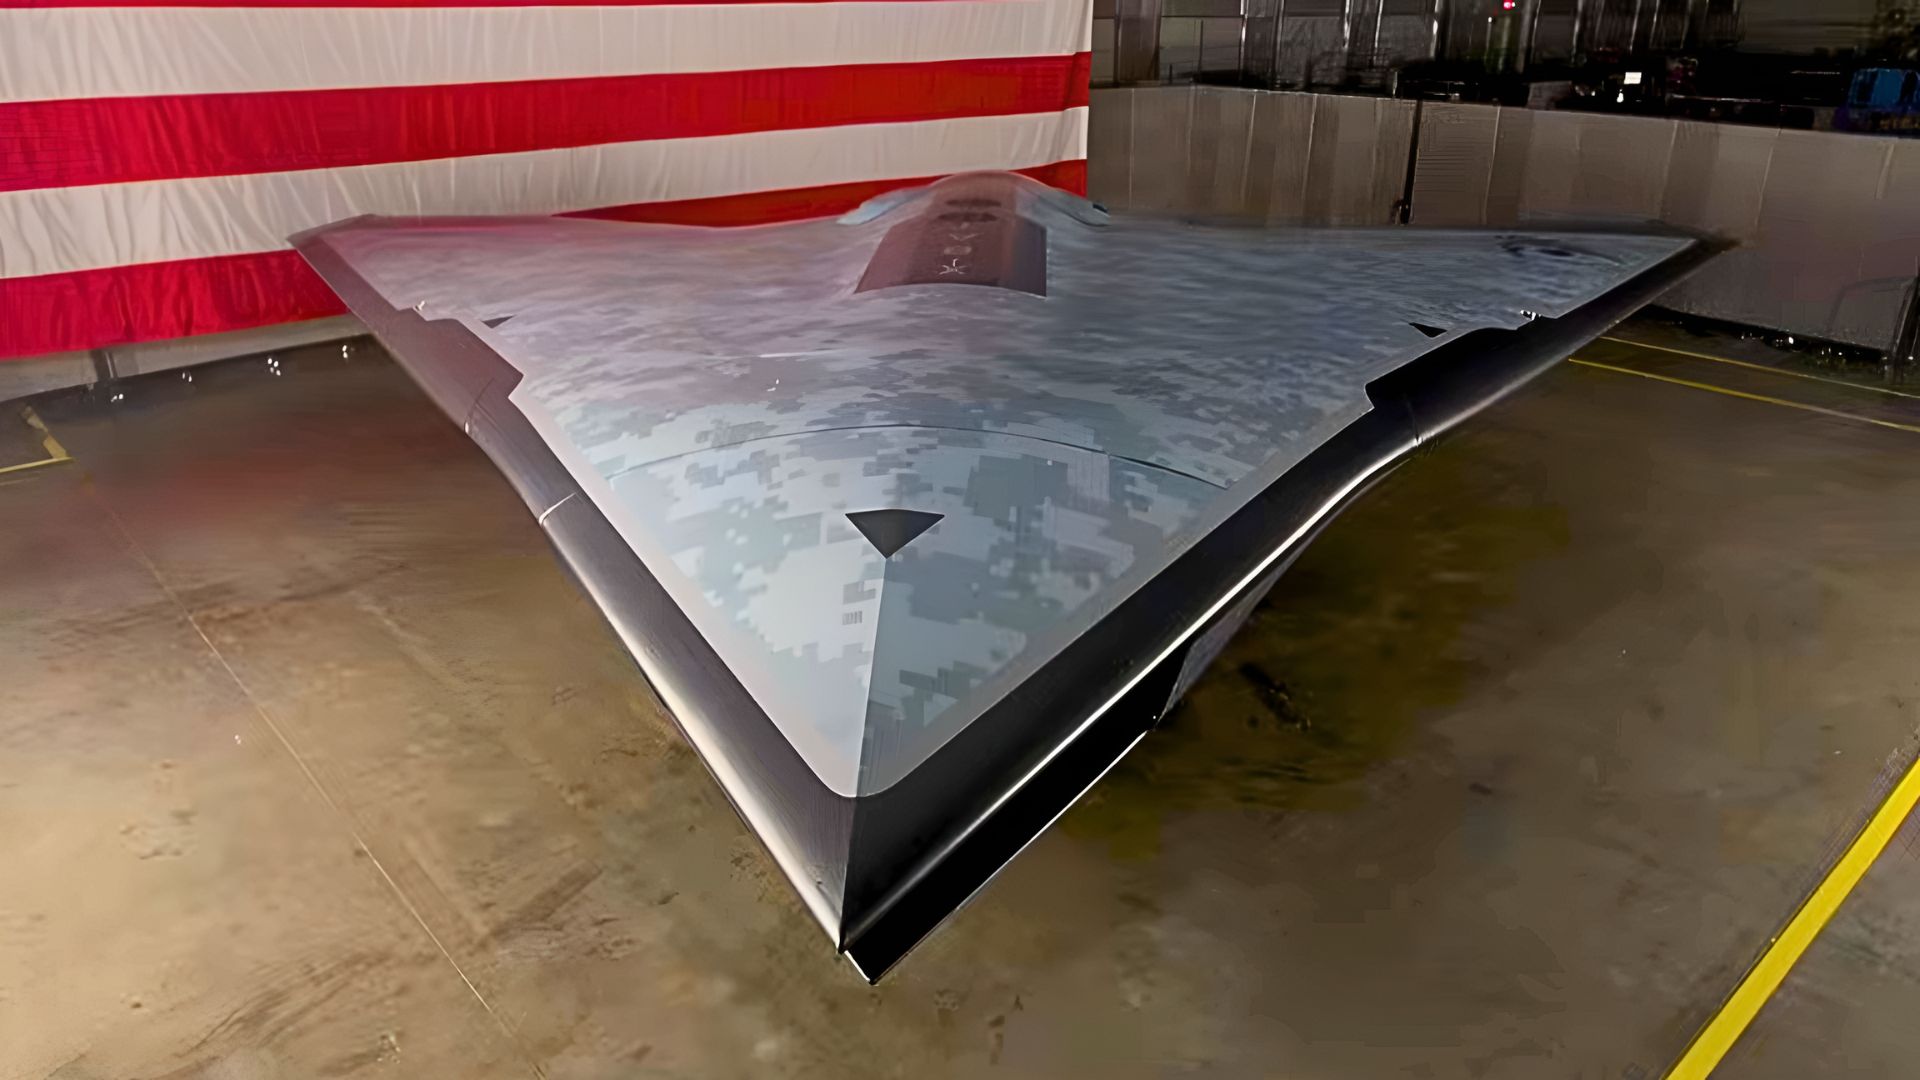
X-BAT Drone Prototype Unveiled with Advanced VTOL Capabilities
Article Content

- •X-BAT 001 is a full-scale prototype designed for vertical takeoff and landing.
- •The drone can carry munitions weighing up to 2,000 pounds in its internal bays.
- •Testing of the prototype will begin shortly at the X-Forge 2 facility in Kansas.
Shield AI has unveiled the X-BAT 001, a full-scale prototype of its jet-powered stealth drone, designed for vertical takeoff and landing (VTOL). The drone, powered by a GE Aerospace F110 turbofan, is intended for operations from naval vessels and remote locations without conventional runways. It features internal weapon bays capable of carrying munitions up to 2,000 pounds. The prototype is currently being transported to Newton, Kansas, for testing, where engineers will evaluate its propulsion and vertical flight capabilities. The testing program will include initial engine runs and crane-assisted trials before attempting untethered flights. The U.S. Navy has expressed interest in the X-BAT as part of its future operational capabilities. Shield AI plans to build a total of two prototypes for further development.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Common questions
What is the purpose of the X-BAT drone?
What are the testing plans for the X-BAT prototype?
How much munitions can the X-BAT carry?
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 Critical RCE Vulnerability in Prefab UI Disclosed A critical remote code execution vulnerability, CVE-2026-120338, was disclosed on November 1, 2026, affecting Prefab UI's Generative UI sandbox. The flaw allows attackers to execute arbitrary Python code by exploiting Deno's permissions, enabling file read/write access on the host server. This vulnerability affects…