Summary
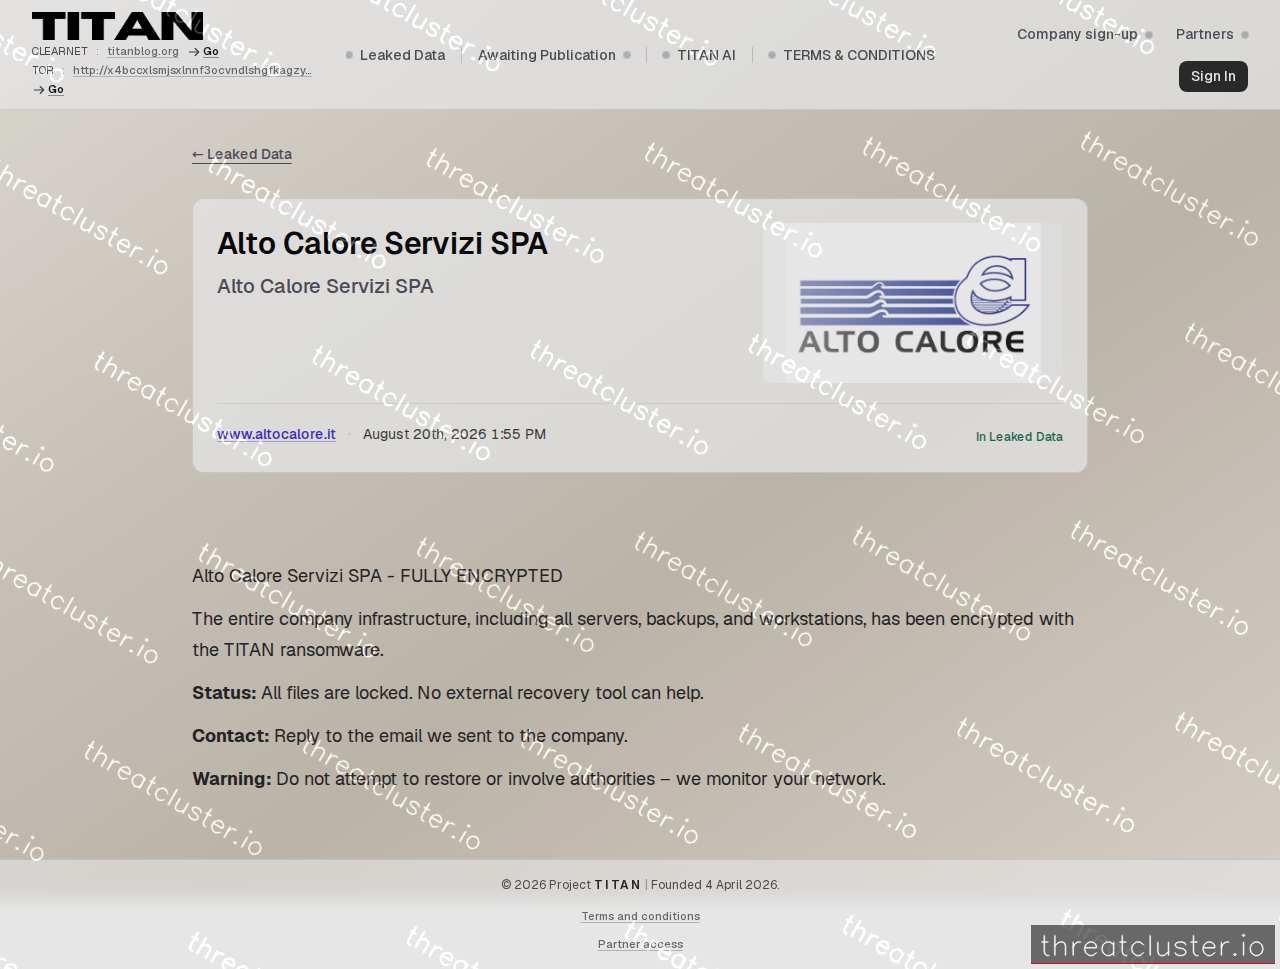
Written by ThreatClusterfrom site fields, victim profile, leak post, screenshotThe leak states that Alto Calore Servizi SPA's entire infrastructure—including all servers, backups, and workstations—has been fully encrypted with the TITAN ransomware, with all files locked and no external recovery tool able to help. The victim is identified as Alto Calore Servizi SPA (domain altocalore.it) and the leak is published. The page repeats a warning not to restore or involve authorities, stating that the group monitors the victim's network.
Describes what the group claims on its leak site. A listing is not confirmation that a breach occurred.
Victim profile
- Domains
- www.altocalore.it
What was taken
Alto Calore Servizi SPA - FULLY ENCRYPTED. The entire company infrastructure, including all servers, backups, and workstations, has been encrypted with the TITAN ransomware. Status: All files are locked. No external recovery tool can help. Contact: Reply to the email we sent to the company. Warning: Do not attempt to restore or involve authorities – we monitor your network.
Also stated on the leak page
Fields this group publishes that do not map to a standard column. Labels are the site's own.
- Warning
- Do not attempt to restore or involve authorities – we monitor your network.
Leak-site images (1)
Images from the victim's leak listing. Thumbnails scraped from the onion page are blurred by default — click a thumbnail to view.