Summary
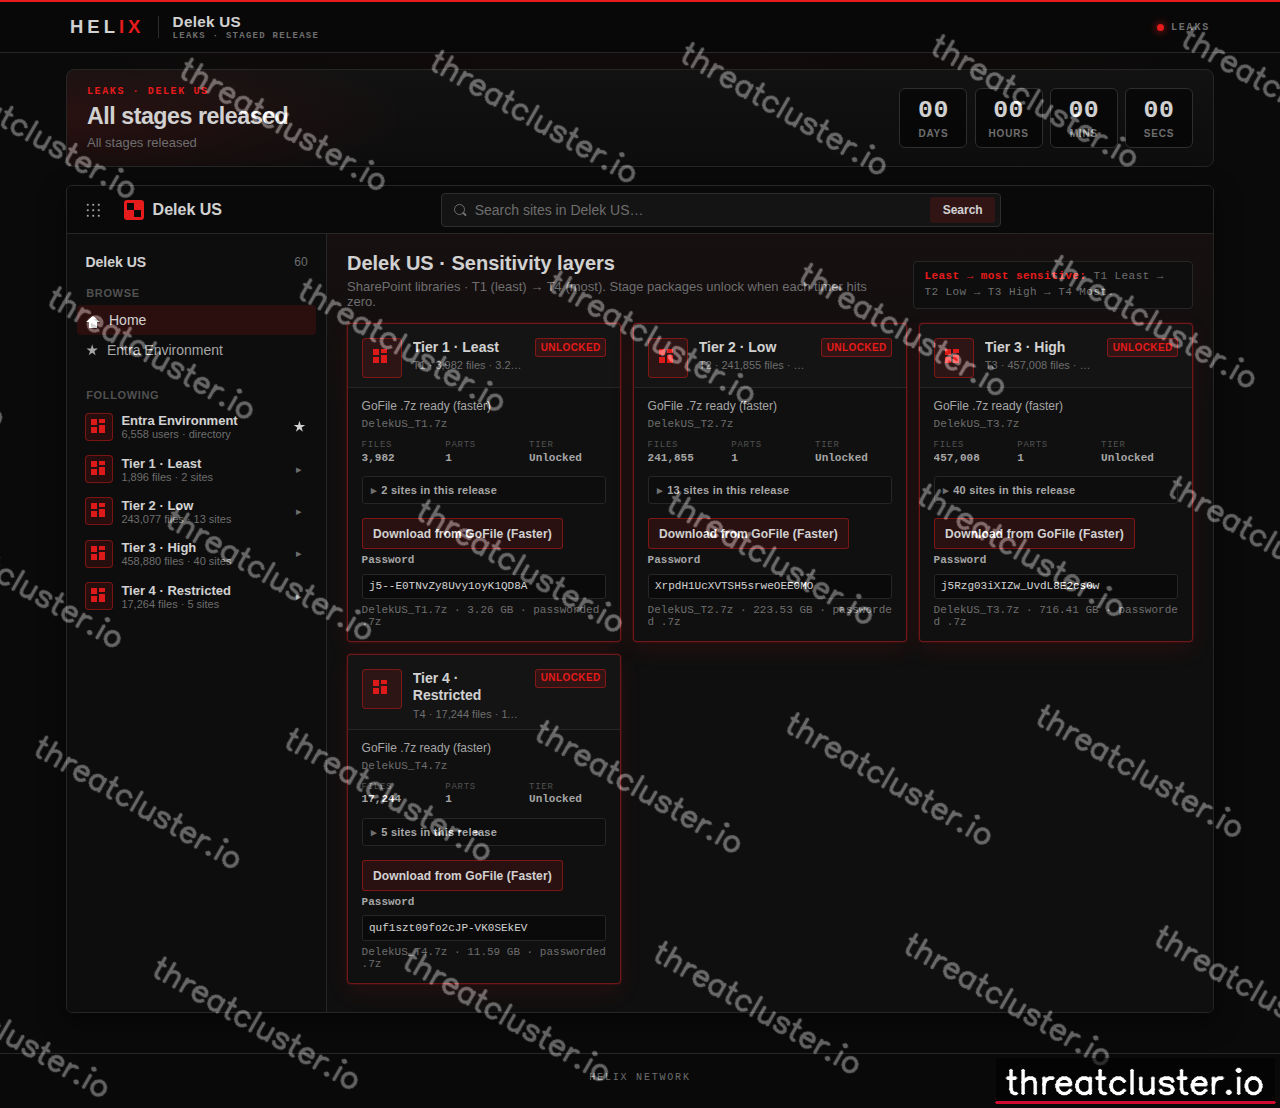
Written by ThreatClusterfrom site fields, file listing, victim profile, leak post, screenshotThe leak claims 720,089 files were taken from Delek US, published on the group's leak site with a countdown showing zero time remaining and all stages released. Data categories claimed include documents, emails, and training records; sample archives published are DelekUS_T1.7z, DelekUS_T2.7z, DelekUS_T3.7z, and DelekUS_T4.7z (four 7z archives). The leak page lists SharePoint, GoFile, and gofile.io as the platforms involved, and notes the archives are passworded with the password "passworded."
Describes what the group claims on its leak site. A listing is not confirmation that a breach occurred.
Victim profile
- Platforms
- SharePoint GoFile
What was taken
Delek US is live. T1 unlocks in 12 hours, then 24 hours per remaining tier.
Also stated on the leak page
Fields this group publishes that do not map to a standard column. Labels are the site's own.
- Password
- passworded .7z
- Tier 1 download
- DelekUS_T1.7z · 3.26 GB · passworded .7z
- Tier 2 download
- DelekUS_T2.7z · 223.53 GB · passworded .7z
- Tier 3 download
- DelekUS_T3.7z · 716.41 GB · passworded .7z
- Tier 4 download
- DelekUS_T4.7z · 11.59 GB · passworded .7z
- Tier 1 GoFile link
- https://gofile.io/d/179e4110-1b88-4170-b3b0-d3f636bc4d96
- Tier 2 GoFile link
- https://gofile.io/d/6f990daf-8e0c-4a27-a844-7062d83e50cd
- Tier 3 GoFile link
- https://gofile.io/d/0ecad5a3-1aa3-4e7c-9cae-eccf5897a2d1
- Tier 4 GoFile link
- https://gofile.io/d/3e428d57-c48c-4670-b131-5441b3dc7c1b
- All stages released
- Yes
Leak-site images (1)
Images from the victim's leak listing. Thumbnails scraped from the onion page are blurred by default — click a thumbnail to view.