Summary
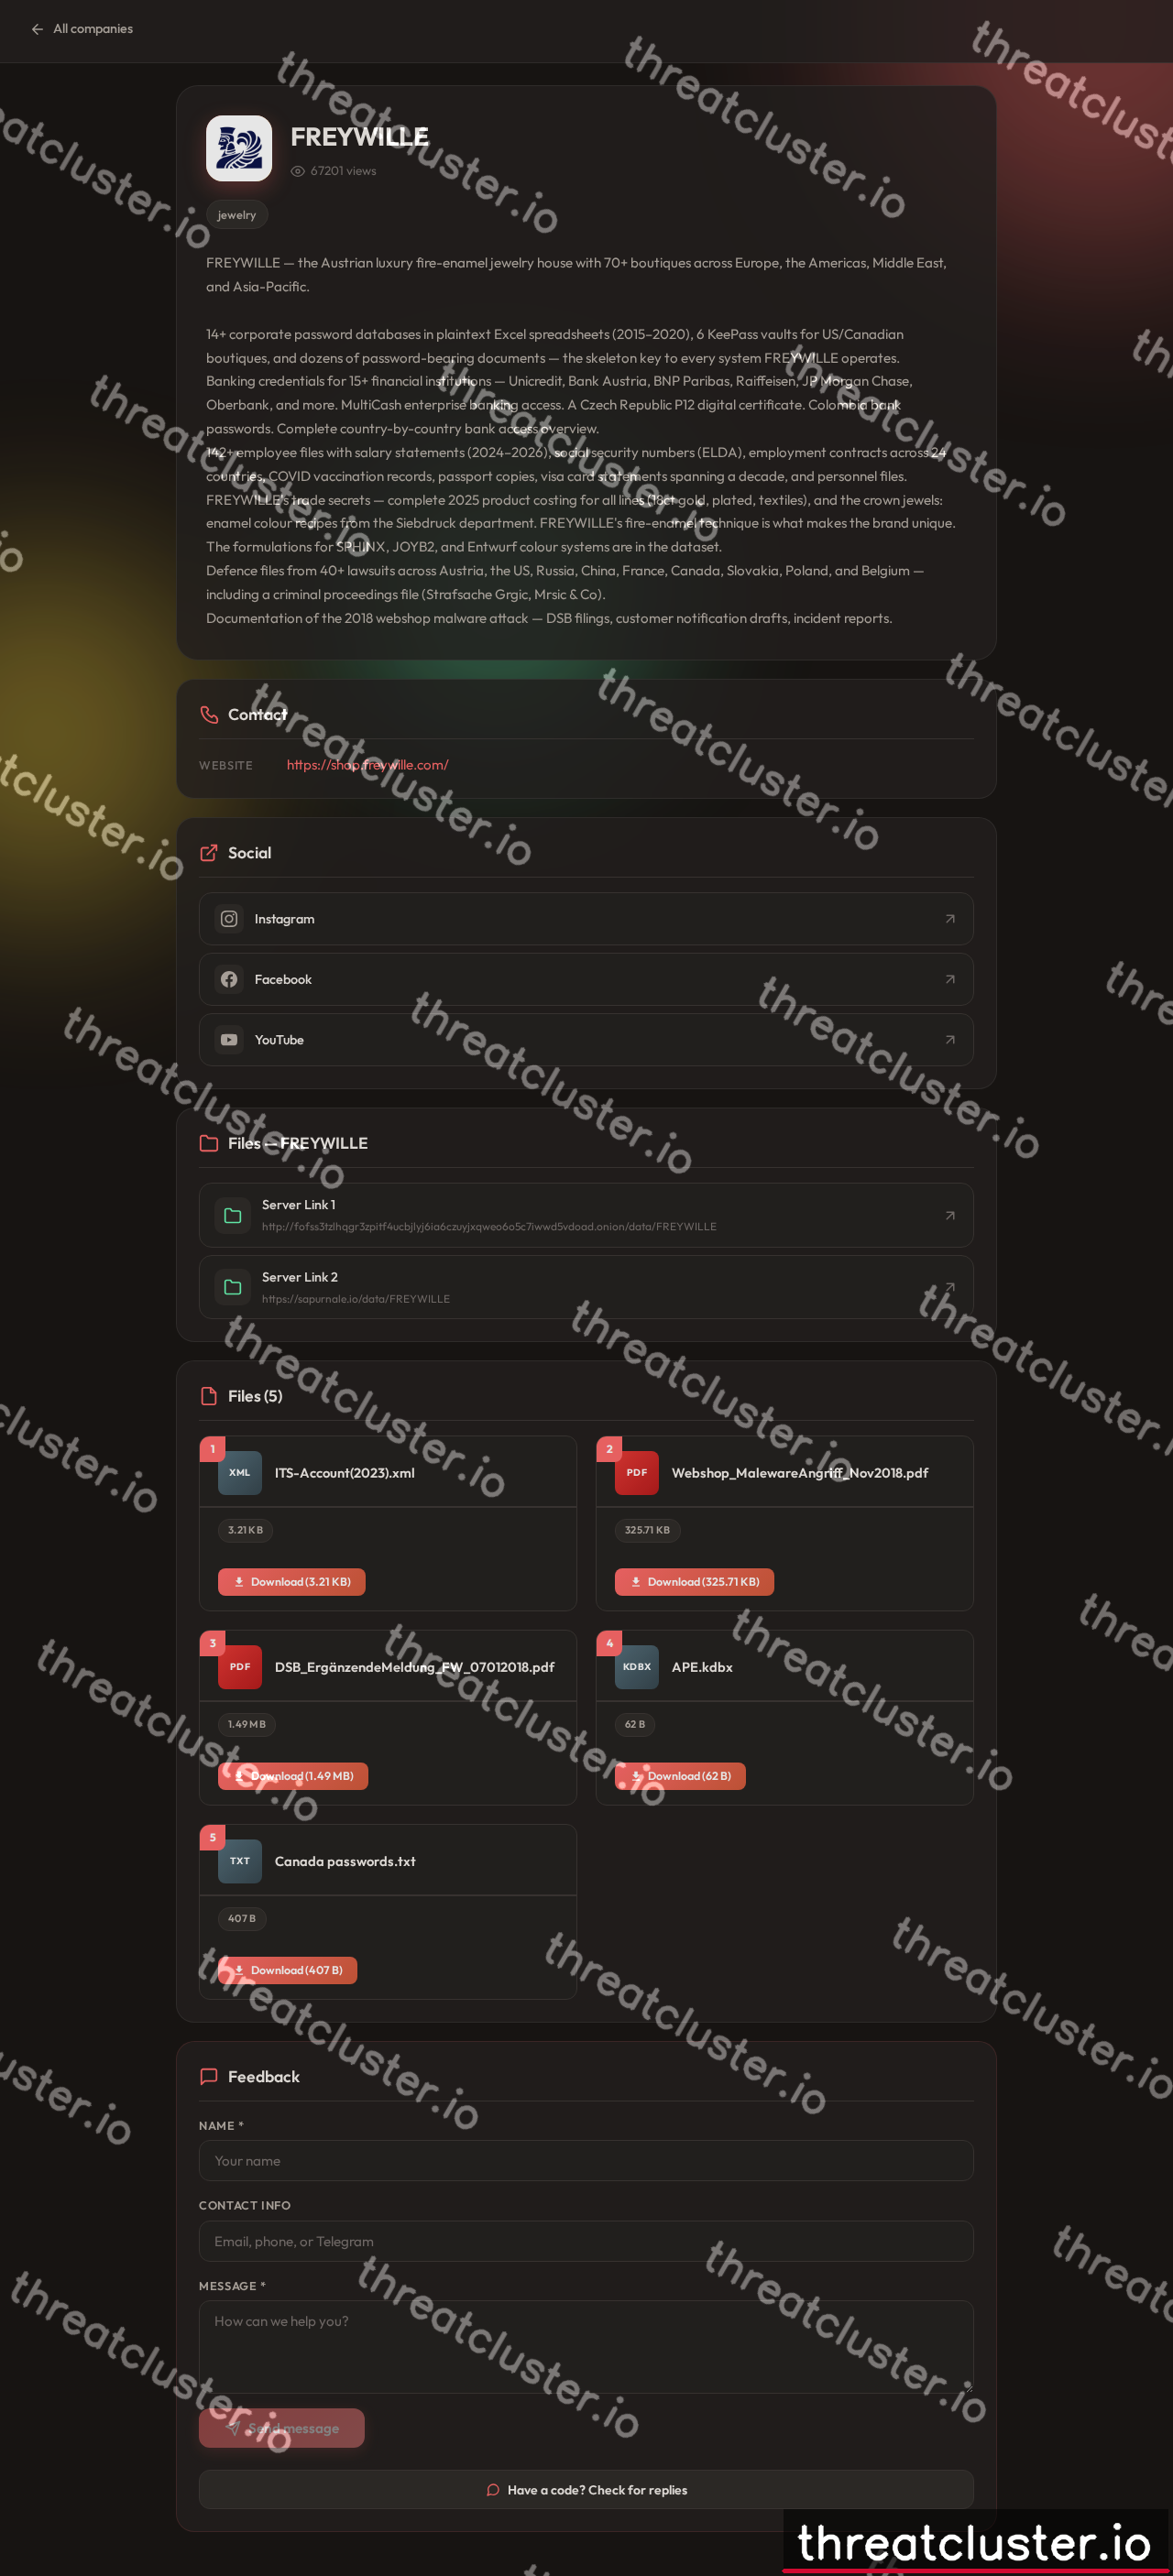
Written by ThreatClusterfrom site fields, file listing, victim profile, leak post, screenshotAurora claims FREYWILLE, the Austrian luxury jewelry house, had about 1.81 MB of data exfiltrated, with five files published. The leak page states the stolen data categories include corporate credentials, banking/financial data, HR records, trade secrets, legal/litigation documents, and webshop malware attack documentation. Sample filenames published include ITS-Account(2023).xml, Webshop_MalewareAngriff_Nov2018.pdf, DSB_ErgänzendeMeldung_FW_07012018.pdf, APE.kdbx, and Canada passwords.txt. The leak post is listed (published) and provides two data links.
Describes what the group claims on its leak site. A listing is not confirmation that a breach occurred.
Victim profile
- Platforms
- KeePass
- People named
- Grgic Mrsic
What was taken
FREYWILLE — the Austrian luxury fire-enamel jewelry house with 70+ boutiques across Europe, the Americas, Middle East, and Asia-Pacific.
Also stated on the leak page
Fields this group publishes that do not map to a standard column. Labels are the site's own.
- YouTube
- https://www.youtube.com/freywilleofficial
- https://www.facebook.com/FREYWILLE/
- https://www.instagram.com/freywille/
- Server Link 1
- http://fofss3tzlhqgr3zpitf4ucbjlyj6ia6czuyjxqweo6o5c7iwwd5vdoad.onion/data/FREYWILLE
- Server Link 2
- https://sapurnale.io/data/FREYWILLE
Leak-site images (2)
Images from the victim's leak listing. Thumbnails scraped from the onion page are blurred by default — click a thumbnail to view.