Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
Ransomware groups, including Qilin and INC, are exploiting a critical authentication bypass vulnerability (CVE-2026-0257) in Palo Alto Networks' PAN-OS GlobalProtect and Prisma Access. This flaw allows attackers to establish unauthorized VPN sessions, bypassing multifactor authentication controls. S...
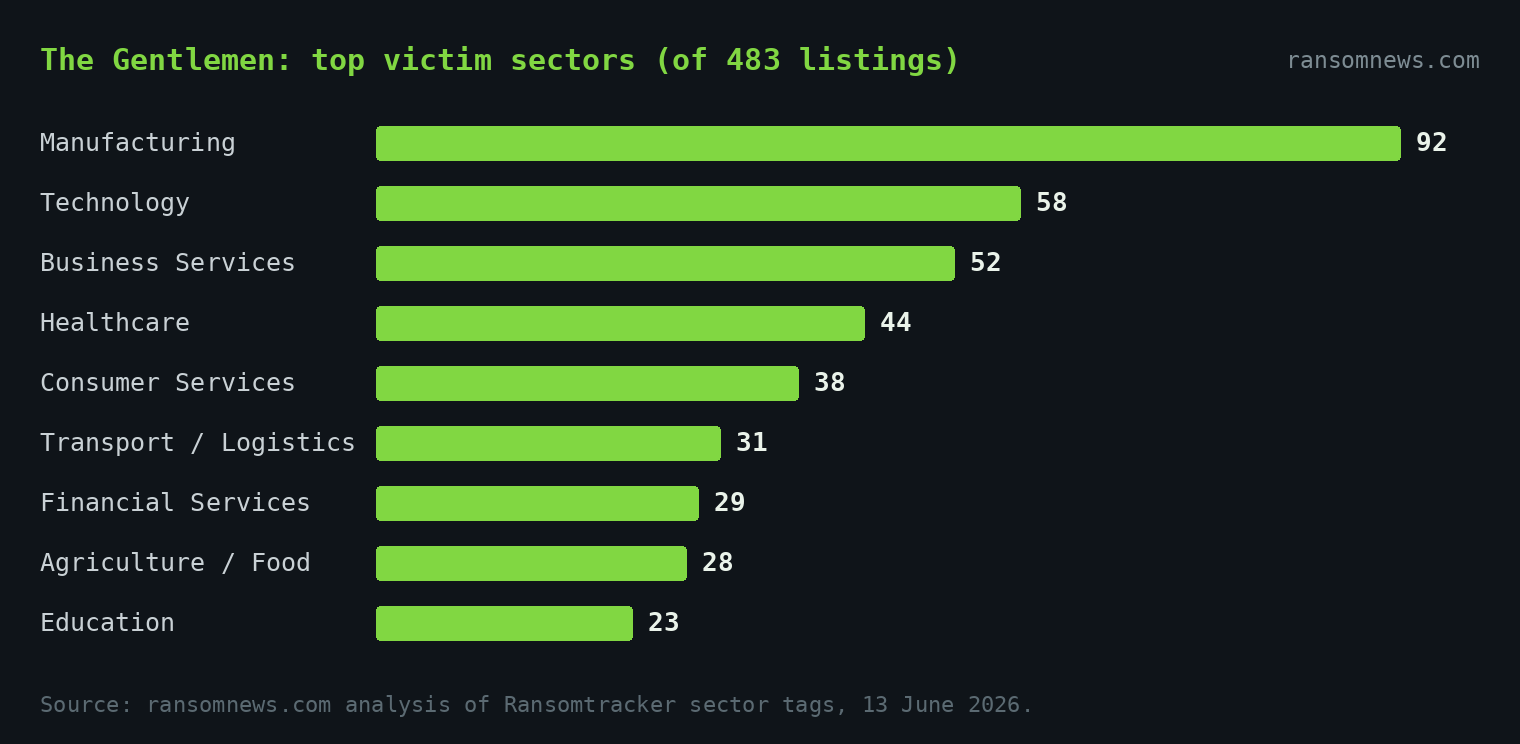
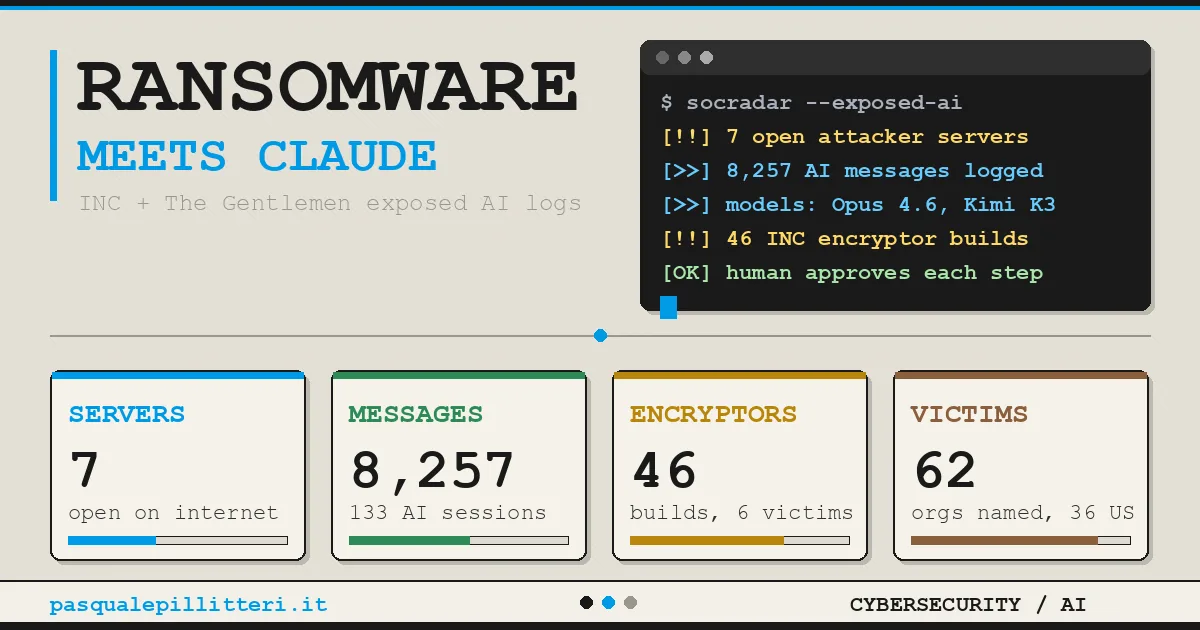
Researchers from SOCRadar uncovered an AI-driven intrusion ecosystem linked to the INC and The Gentlemen ransomware groups, utilizing a framework called Phantom. The operation exploited vulnerabilities in public-facing edge devices, including FortiClient EMS, SimpleHelp, and cPanel, affecting at lea...
As of February 12, 2026, organizations worldwide are experiencing an average of 2,090 cyber-attacks per week, largely driven by ransomware incidents. This increase highlights the ongoing challenges faced by businesses in securing their networks against evolving cyber threats.
In 2025, ransomware groups Medusa and DragonForce targeted UK organizations by exploiting three critical vulnerabilities in the SimpleHelp Remote Monitoring and Management platform. These vulnerabilities (CVE-2024-57726, CVE-2024-57727, CVE-2024-57728) allowed unauthorized access through trusted thi...