Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
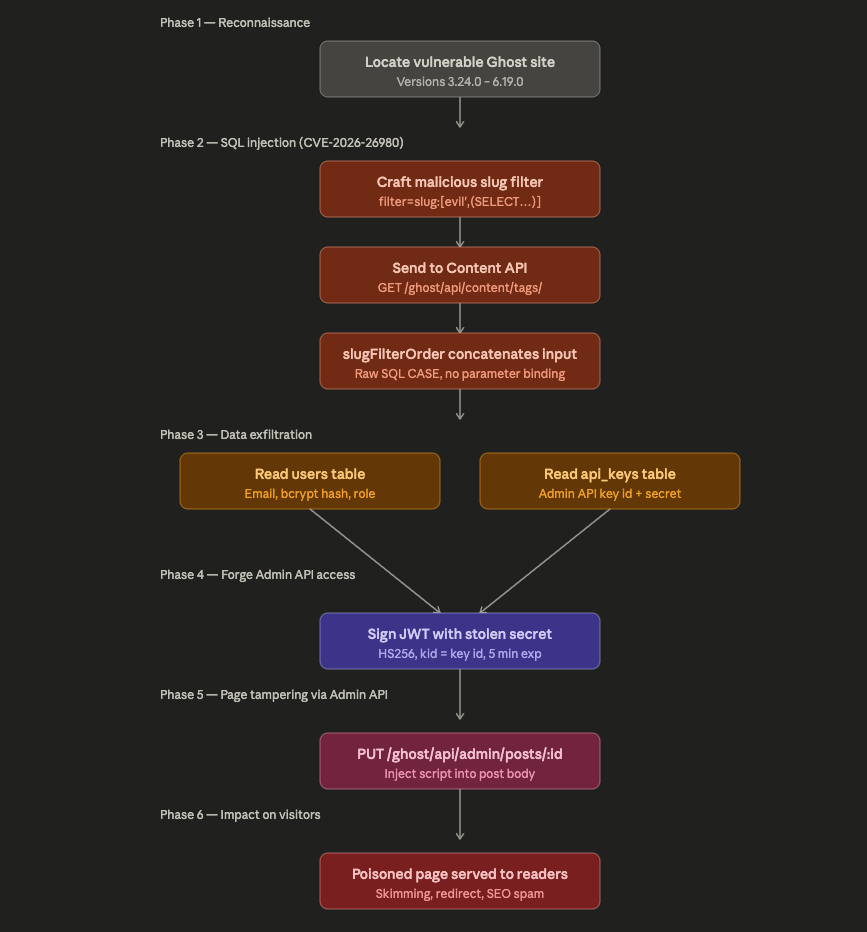
A critical SQL injection vulnerability (CVE-2026-26980) in Ghost CMS is being actively exploited in a large-scale cyberattack affecting over 700 websites, including those of Harvard University, Oxford University, Auburn University, and DuckDuckGo. The vulnerability allows unauthenticated attackers t...
CVE-2026-26980 is a SQL Injection vulnerability affecting Ghost, a Node.js content management system, allowing unauthenticated attackers to perform arbitrary database reads. The flaw exists in the Content API's slug filter ordering functionality, impacting versions 3.24.0 through 6.19.0. Attackers c...
NightSpire ransomware, identified in early 2025, has rapidly become a significant threat, employing double-extortion tactics. It targets various sectors, including hospitals and government offices, by exploiting Remote Desktop Protocol (RDP) vulnerabilities and remote admin tools. Victims face data...
On October 8, 2026, Anthropic announced the launch of its Cyber Mission, aimed at enhancing the security of critical infrastructure and open-source software. The initiative includes the Critical Infrastructure Defense Program (CIDP) and OSS Scanner, a free service for periodic vulnerability scans of...