Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
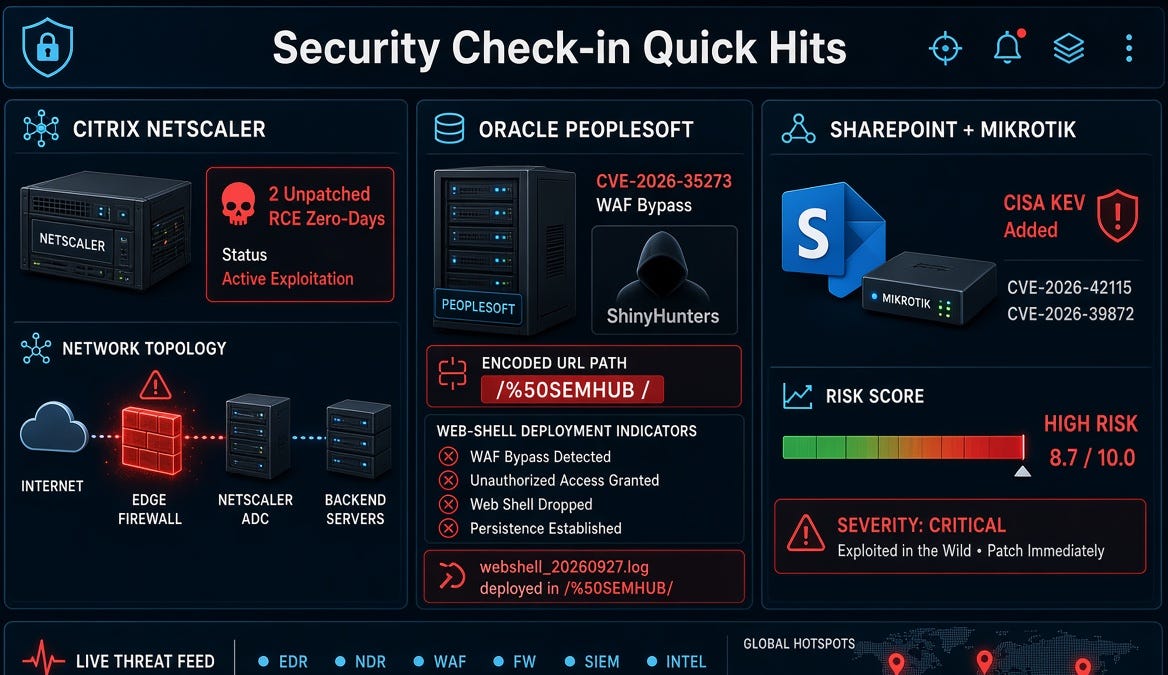
Citrix disclosed two critical zero-day vulnerabilities, CVE-2026-88771 and CVE-2026-88772, affecting NetScaler ADC and Gateway systems, which are being actively exploited. Both vulnerabilities have a CVSS score of 9.5 and allow unauthenticated attackers to execute arbitrary commands remotely. CVE-20...
On September 26, 2026, security firm watchTowr reported two unpatched zero-day vulnerabilities in Citrix NetScaler ADC and Gateway appliances, allowing remote code execution (RCE) and actively exploited in the wild. Citrix has confirmed the existence of these vulnerabilities, tracked as CVE-2026-887...
Chinese hackers infiltrated Microsoft 365 environments, maintaining access for 18 months before detection. The attack exploited vulnerabilities to harvest sensitive data from various organizations. Simultaneously, a new vulnerability in Oracle PeopleSoft (CVE-2026-35273) was disclosed, with active e...
A pre-authentication remote code execution (RCE) vulnerability, CVE-2026-35273, was discovered in Oracle PeopleSoft PeopleTools, affecting versions 8.61 and 8.62. The vulnerability allows unauthenticated attackers to execute code within the application server's Java virtual machine (JVM) by exploiti...