Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
A critical zero-day privilege escalation vulnerability in the LiteSpeed User-End cPanel plugin is being exploited in the wild, allowing authenticated cPanel users to execute arbitrary scripts as root. This flaw, tracked as CVE-2026-48172, has a maximum CVSS score of 10.0 and affects versions from v2...
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has issued a warning regarding a critical vulnerability (CVE-2026-54420) in the LiteSpeed cPanel user-end plugin, which allows attackers with FTP or web shell access to escalate privileges to root on shared hosting servers using CloudL...
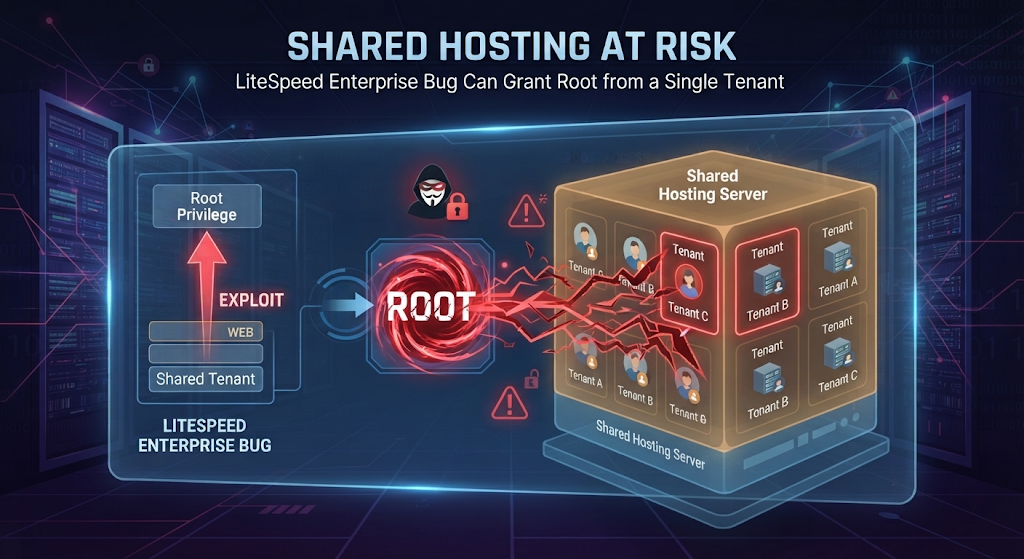
A critical vulnerability in LiteSpeed Web Server Enterprise allows low-privilege users on shared hosting servers to gain root access, potentially compromising other accounts and the server itself. The flaw affects versions prior to 6.3.7, and cPanel issued an advisory on September 14, 2026, urging i...