Frequency
7
occurrences
First Seen
June 16, 2026
Last Seen
September 15, 2026
Exploited in Wild
—
Ransomware Use
—
Public Exploits
—
Attack Vector
—
Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has issued a warning regarding a critical vulnerability (CVE-2026-54420) in the LiteSpeed cPanel user-end plugin, which allows attackers with FTP or web shell access to escalate privileges to root on shared hosting servers using CloudL...
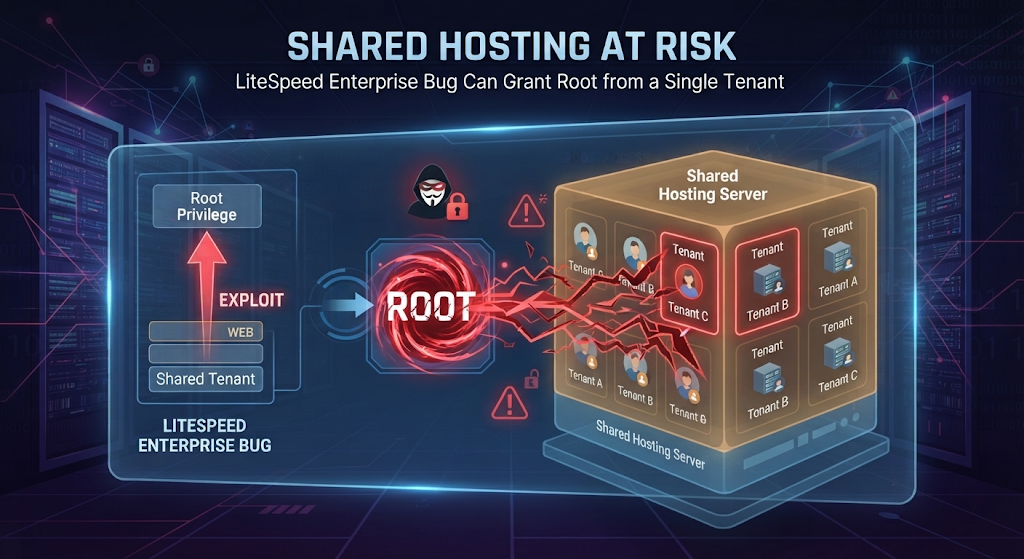
A critical vulnerability in LiteSpeed Web Server Enterprise allows low-privilege users on shared hosting servers to gain root access, potentially compromising other accounts and the server itself. The flaw affects versions prior to 6.3.7, and cPanel issued an advisory on September 14, 2026, urging i...
Public Exploits
Checking GitHub for proof-of-concept code…
Related Clusters (2)

Related Articles (7)


1 / 2