 Ukrinform
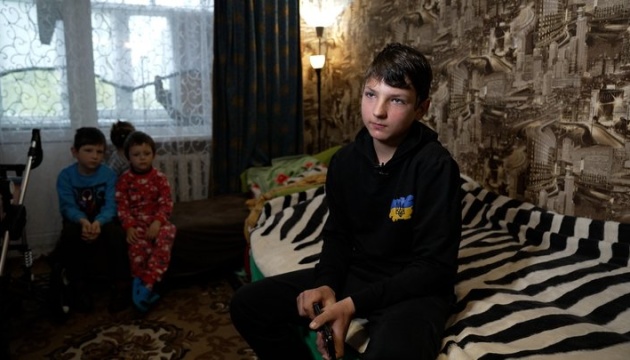
12-Year-Old Ukrainian Boy Disables Russian Drone to Protect Siblings
Article Content

- •A 12-year-old boy disabled a Russian drone, protecting his siblings from potential harm.
- •The incident occurred in Semenivka, Ukraine, highlighting ongoing aerial threats to civilians.
- •Experts caution that such actions could make individuals targets for additional drone strikes.
On April 18, 2026, in Semenivka, Ukraine, 12-year-old Anatoliy Prokhorenko cut the fiber-optic cable of a Russian FPV drone, preventing it from striking his younger siblings who were playing nearby. The drone lost control and crashed into bushes 100 to 150 meters away. Anatoliy learned this technique from military acquaintances while assisting them in the forest. His quick thinking and instinct to protect his family outweighed his fear during the incident. Following the event, the family moved to Chernihiv and plans to register as internally displaced persons due to ongoing security risks. Experts warned that the boy was fortunate there were no additional drones in the vicinity, as FPV drones are typically guided by higher-altitude surveillance drones. The incident highlights the ongoing threat of aerial strikes in the region, which has seen multiple attacks on civilian targets. Anatoliy expressed a desire to join the military and work with drone technology in the future.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…