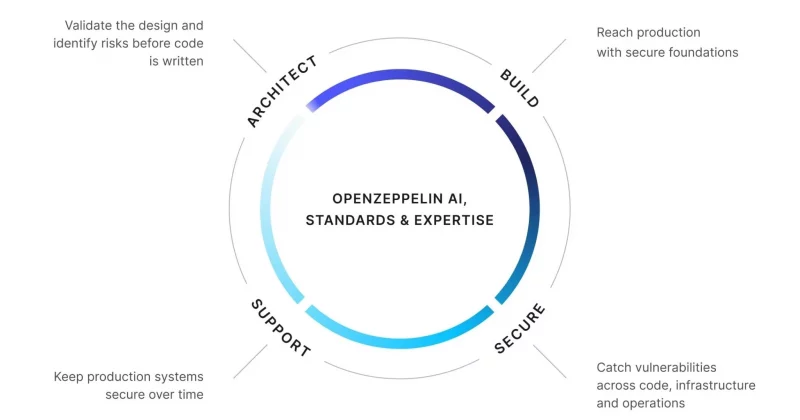
 Cryptobriefing
AI Agents Render All DeFi Protocols Unsafe, Warns Security Expert
Article Content

- •All DeFi protocols are deemed unsafe due to AI's enhanced vulnerability discovery.
- •Over $600 million was lost to DeFi exploits in April 2026, with significant incidents reported.
- •The total value locked in DeFi has fallen by over $20 billion since January 2026.
Manuel Aráoz, CEO of OpenZeppelin, has declared that all decentralized finance (DeFi) protocols are currently unsafe due to the enhanced capabilities of AI agents in identifying vulnerabilities. His warning follows a significant uptick in DeFi exploits, with over $600 million lost in April 2026 alone. The asymmetry in security—where defenders must address every vulnerability while attackers need to find just one—has been exacerbated by AI's ability to analyze code rapidly. Notable incidents include the $292 million KelpDAO exploit and the $285 million loss from Drift. The total value locked (TVL) in DeFi has decreased by over $20 billion since the start of the year, reflecting a loss of confidence in the sector. Experts suggest that traditional security measures are insufficient against AI-driven threats, prompting calls for enhanced security protocols and continuous monitoring. The current state of DeFi is precarious, with ongoing discussions about the need for new security frameworks.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (9)
Following this threat?
Track KelpDAO in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Crypto Hacks in 2026: $2.2B Lost Amid Rising Threats In 2026, cryptocurrency security losses have reached approximately $2.21 billion across 288 reported incidents. The first half of the year saw 207 hacks, a significant increase from 83 in the same period of 2025. Major losses were driven by infrastructure and operational failures, with 4% of attacks accounting for 75%…
 NEAR Intents Loses $3.8 Million in Exploit Linked to Omni Bridge Bug On October 1, 2026, NEAR Intents, a cross-chain swap service, suffered a security breach resulting in the theft of approximately $3.8 million. The exploit was due to a bug in the interaction between its Omni deposit and withdrawal infrastructure and the NEAR Intents smart contract. Following the incident, NEAR Intents…