 www.gadgetreview.com
AI Tools Can Extract Fingerprints from Selfies, Experts Warn
Article Content

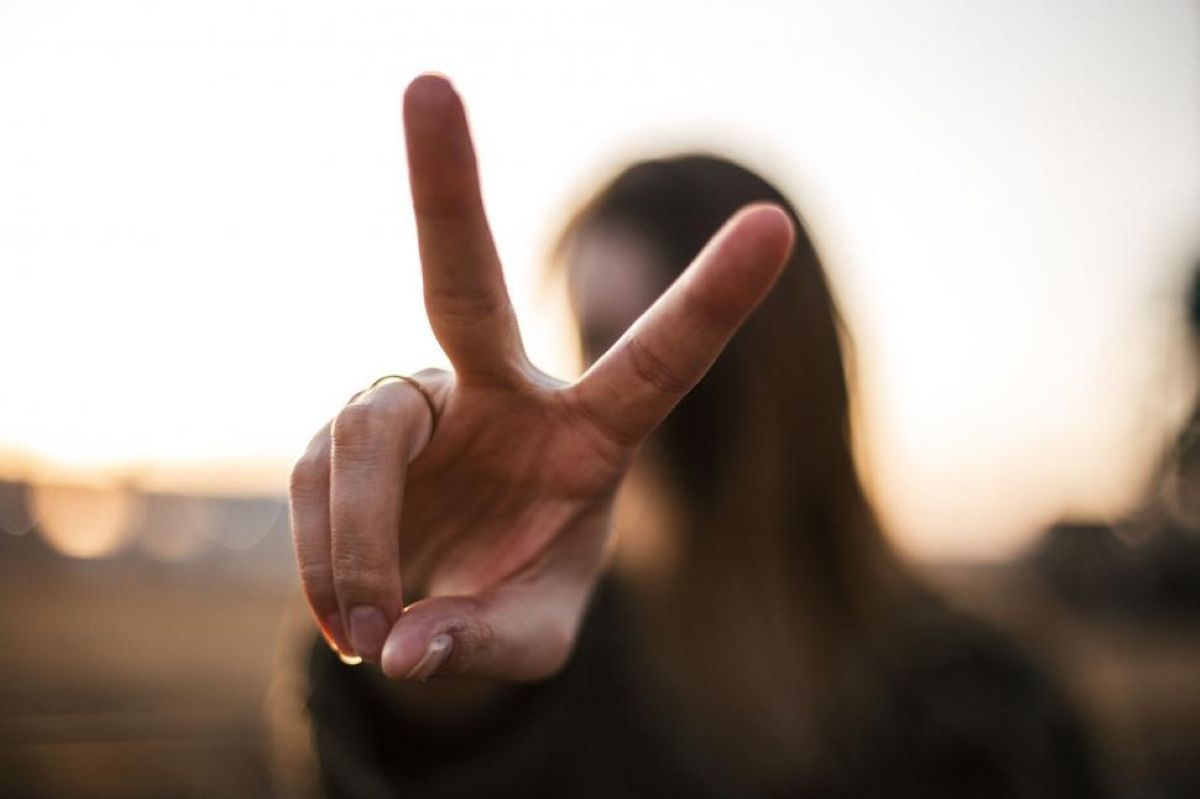
- •AI can reconstruct fingerprints from selfies, especially with the peace sign pose.
- •Modern smartphones and AI tools make fingerprint extraction easier for attackers.
- •Compromised fingerprints cannot be changed, posing a long-term security risk.
Cybersecurity experts have raised alarms about the potential for AI tools to extract fingerprints from high-resolution selfies, particularly those featuring the peace sign pose. Photos taken within five feet can provide enough detail for attackers to reconstruct usable biometric templates. This vulnerability is exacerbated by advancements in AI image enhancement and the high-quality cameras in modern smartphones. While the concept of extracting fingerprints from photos is not new, the accessibility of AI tools has lowered the technical barriers for criminals. Experts emphasize that compromised fingerprints cannot be changed like passwords, making this a significant security concern. Although successful extraction requires ideal conditions, the risk remains as AI capabilities improve. Recommendations for users include avoiding close-up photos of fingertips and using additional authentication methods.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (6)
Following this threat?
Track Office Of Personnel Management in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Critical Zero-Day Vulnerability in Cisco Secure Email Gateway Exploited On September 14, 2026, Cisco disclosed a critical SQL injection vulnerability (CVE-2026-76461) in its Secure Email Gateway, allowing unauthenticated remote attackers to execute arbitrary commands with root privileges. This vulnerability arises from insufficient validation in the email parsing logic. Cisco confirmed…
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…