 Thecyberexpress
Amazon WorkSpaces Linux Flaw Allows Credential Theft
Article Content
Browse articles 
A security flaw in the Amazon WorkSpaces client for Linux, identified as CVE-2025-12779, enables local attackers to extract valid authentication tokens, granting unauthorized access to other users' WorkSpace sessions. Organizations utilizing AWS's virtual desktop infrastructure are affected by this vulnerability. AWS issued a security bulletin on November 5, 2025, detailing the issue and recommending immediate remediation.
Ask AI about this cluster
Answers cite the sources they use
Updated 212d ago How this analysis works
More articles in this cluster (2)
Following this threat?
Track ClickFix, Amazon and CVE-2025-12779 in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
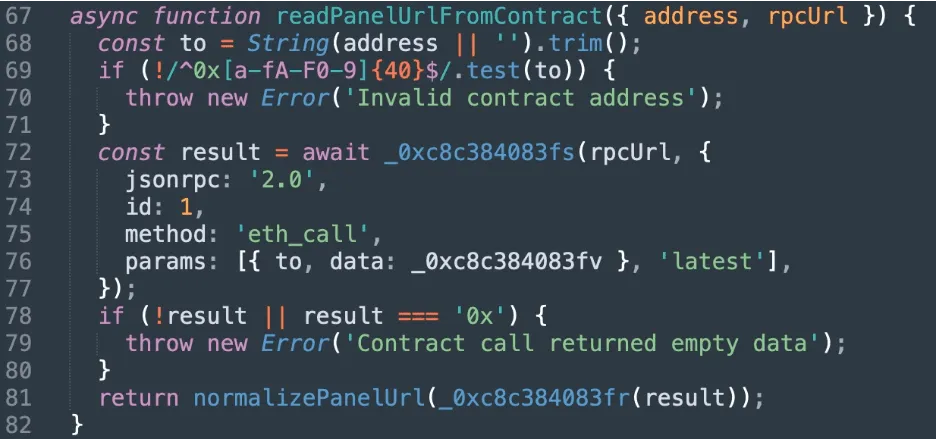 New ChainScript RAT Exploits ClickFix Lures with Blockchain C2 A newly discovered Node.js remote access trojan (RAT) named ChainScript is being deployed through ClickFix social engineering tactics, targeting Windows systems. The malware utilizes a unique command-and-control (C2) discovery method by querying a Polygon blockchain smart contract to dynamically rotate its server…
 Cybercriminals Exploit ChatGPT Custom GPTs for ClickFix RAT Attacks A new ClickFix campaign has been discovered that exploits ChatGPT Custom GPTs to impersonate legitimate products, luring users into executing malicious code. Cybersecurity firm Huntress reported that at least 40 users have been infected, with two confirmed incidents linked to Custom GPT instances. The attackers…