 Techcrunch
Apple Tightens Full Disk Access Controls Amid AI Risks
Article Content

- •Apple is tightening Full Disk Access controls on macOS due to AI misuse.
- •New permissions will require explicit user consent to access sensitive data.
- •The changes follow concerns raised by incidents involving Meta's Muse AI.
Apple announced new restrictions on Full Disk Access (FDA) for macOS applications due to concerns that some developers are misusing this permission, potentially exposing users' private data, including files, messages, and browsing history. This decision follows reports that Meta's Muse AI accessed a journalist's private messages without explicit permission, raising questions about user privacy and security. Apple emphasized that as AI agents grow more capable, the risks associated with such access increase significantly. The company plans to implement controls requiring 'very explicit user action' for granting FDA, although no specific rollout date has been provided. The announcement comes after a series of incidents that have highlighted vulnerabilities in AI applications and their permissions on macOS. Apple did not name specific apps or developers involved but acknowledged the growing concern among users regarding privacy breaches.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (6)
Following this threat?
Track ClickFix and Apple in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What is Full Disk Access?
When will the new controls be implemented?
What should users do now?
Continue Reading
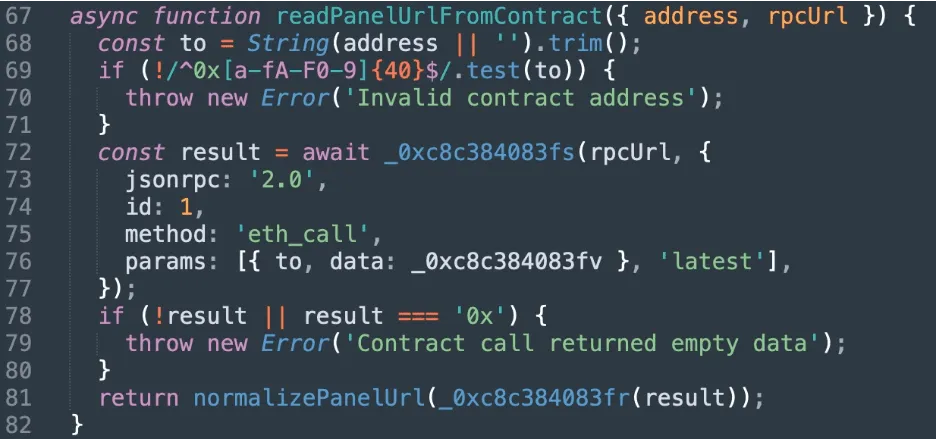 New ChainScript RAT Exploits ClickFix Lures with Blockchain C2 A newly discovered Node.js remote access trojan (RAT) named ChainScript is being deployed through ClickFix social engineering tactics, targeting Windows systems. The malware utilizes a unique command-and-control (C2) discovery method by querying a Polygon blockchain smart contract to dynamically rotate its server…
 Cybercriminals Exploit ChatGPT Custom GPTs for ClickFix RAT Attacks A new ClickFix campaign has been discovered that exploits ChatGPT Custom GPTs to impersonate legitimate products, luring users into executing malicious code. Cybersecurity firm Huntress reported that at least 40 users have been infected, with two confirmed incidents linked to Custom GPT instances. The attackers…