 Smh.Au
Australia Faces Dilemma Over Russian Athletes Linked to Sanctioned Oligarchs
Article Content

- •Russian athletes linked to sanctioned oligarchs are set to compete in Australia.
- •The Australian Federation of Ukrainian Organisations demands scrutiny of all Russian participants.
- •Australia has sanctioned over 1,300 individuals and entities connected to Russia.
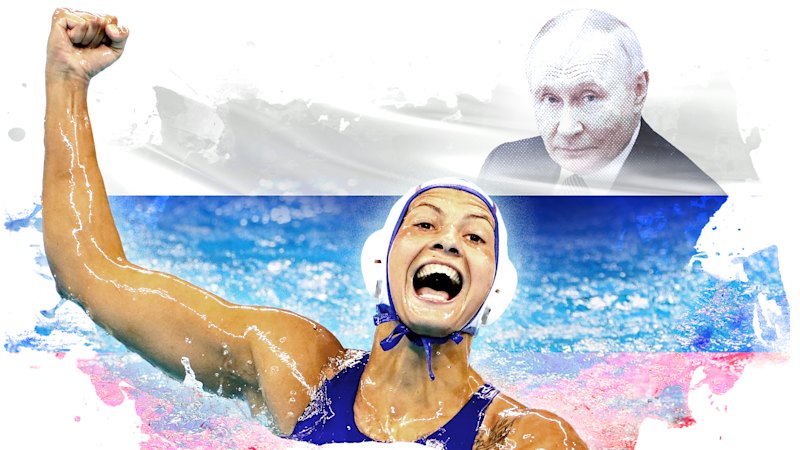
The Australian government is under pressure as Russian athletes, linked to sanctioned oligarchs, prepare to compete in the World Cup in Sydney. The Russian women's national water polo team is set to participate under its national flag after a ban was lifted in April 2026. This decision has raised concerns about legal and diplomatic implications due to Australia's sanctions laws, particularly regarding athletes associated with entities like Surgutneftegas, a sanctioned oil producer. The Australian Federation of Ukrainian Organisations is demanding thorough scrutiny of all Russian participants. The situation reflects ongoing geopolitical tensions stemming from Russia's invasion of Ukraine, which has lasted over four years. Calls for stricter sanctions and investigations into the athletes' connections are intensifying as Australia balances its international commitments and domestic sentiments. The federal government has sanctioned over 1,300 individuals and entities related to Russia, emphasizing its support for Ukraine.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Continue Reading
 Critical Zero-Day Vulnerability in Cisco Secure Email Gateway Exploited On September 14, 2026, Cisco disclosed a critical SQL injection vulnerability (CVE-2026-76461) in its Secure Email Gateway, allowing unauthenticated remote attackers to execute arbitrary commands with root privileges. This vulnerability arises from insufficient validation in the email parsing logic. Cisco confirmed…
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…