 Dvidshub
Balikatan 2026: U.S. and Philippine Forces Prepare for Potential Taiwan Conflict
Article Content

- •Balikatan 2026 involves 17,000 troops from the U.S., Philippines, and five allied nations.
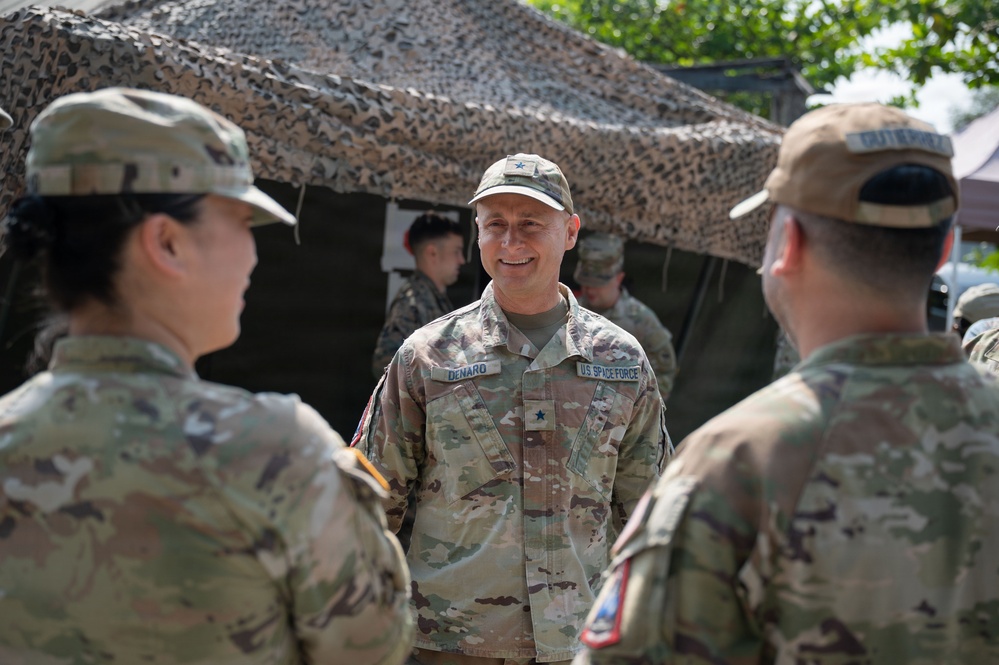
- •The U.S. Space Force's participation marks a significant integration of space capabilities into military operations.
- •The exercise prepares forces for potential Chinese aggression in the Taiwan Strait by 2027.
Balikatan 2026, a large-scale military exercise involving 17,000 troops from the U.S., Philippines, and five allied nations, commenced on April 20, 2026. This year's exercise emphasizes the integration of space capabilities, with participation from the U.S. Space Force, marking a significant development in joint military operations. The exercise aims to enhance bilateral interoperability and readiness against potential Chinese aggression in the Taiwan Strait and South China Sea. U.S. military officials have stated that the exercise is a crucial step in preparing for a possible Chinese invasion of Taiwan by 2027. The inclusion of various allied nations reflects the Philippines' strategy to bolster its defense partnerships amid rising regional tensions. The exercise runs until May 8, 2026, and includes operations across multiple domains: air, land, sea, cyber, and space. This multilateral approach is a response to increasing concerns over China's military actions in the region.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…