 Bleepingcomputer
Chinese Hackers Exploit Dell Zero-Day Flaw CVE-2026-22769 Since Mid-2024
Article Content
Browse articles 
A Chinese state-backed hacking group, UNC6201, has been exploiting a critical zero-day vulnerability in Dell RecoverPoint for Virtual Machines since at least mid-2024. The flaw, tracked as CVE-2026-22769, features a maximum severity rating due to hardcoded credentials, allowing unauthorized access to VMware virtual machine backups. This exploitation was revealed by Mandiant and the Google Threat Intelligence Group on February 17, 2026.
Ask AI about this cluster
Answers cite the sources they use
Updated 213d ago How this analysis works
Timeline
2024-06-01
UNC6201 begins exploiting Dell RecoverPoint vulnerability
2026-02-17
CVE-2026-22769 published
2026-02-17
Mandiant and GTIG report on UNC6201's activities
More articles in this cluster (40)
Following this threat?
Track Silk Typhoon, Brickstorm and Dell in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
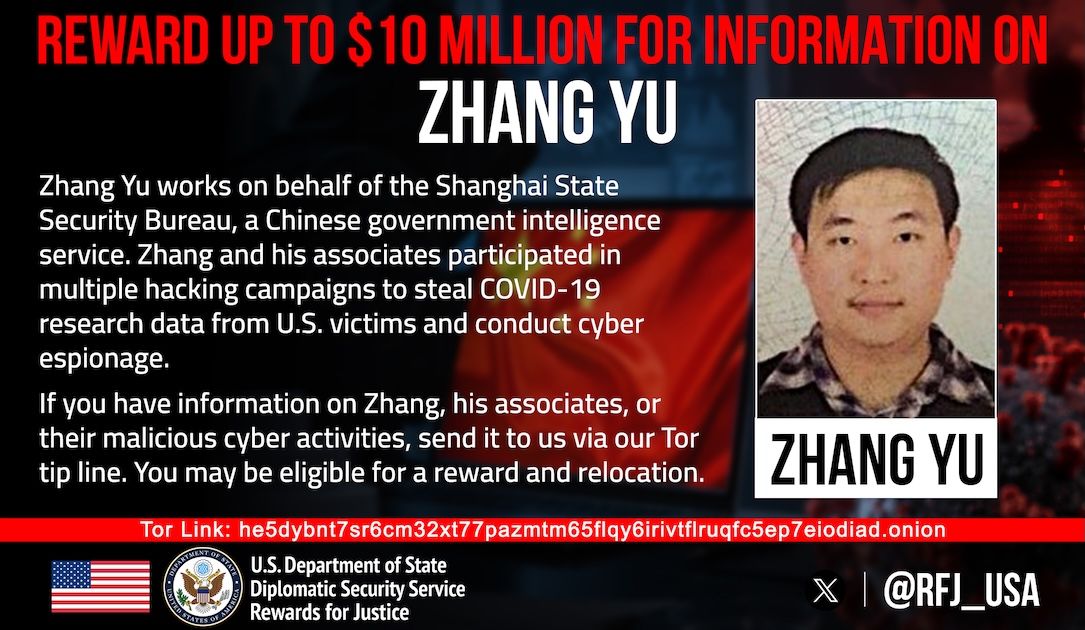 U.S. Offers $10 Million Reward for Zhang Yu, Accused Chinese Hacker The U.S. State Department has announced a reward of up to $10 million for information leading to the identification or location of Zhang Yu, a Chinese national charged with cyberattacks against U.S. COVID-19 research institutions. Zhang is accused of working under the direction of China's Ministry of State Security…
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…