 www.tahawultech.com
Cisco Talos Reports ClickFix Attacks Targeting Cryptocurrency Traders
Article Content

- •Two ClickFix attack campaigns identified targeting cryptocurrency traders.
- •Victims are tricked into executing malicious JavaScript via trusted services.
- •Cisco recommends strengthening browser controls and user education.
Cisco Talos has identified two ClickFix attack campaigns that exploit trusted services to deceive victims into executing malicious code. The first campaign, active since October 2025, targets cryptocurrency traders with fake security reports, leading them to paste JavaScript into their browsers, which then retrieves attack code from a Google spreadsheet. This malware can alter cryptocurrency deposit addresses and has been linked to over $10,000 in Bitcoin theft across 49 addresses. The second campaign, observed in April 2026, uses fraudulent Google verification prompts from a compromised site, resulting in the installation of the Amatera information stealer, which can harvest credentials and cryptocurrency. Cisco advises organizations to enhance browser controls and educate users about legitimate verification processes. The attacks leverage familiar online experiences, making detection challenging.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track ClickFix in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
How do ClickFix attacks work?
What should organizations do to protect themselves?
Who is primarily targeted by these attacks?
Continue Reading
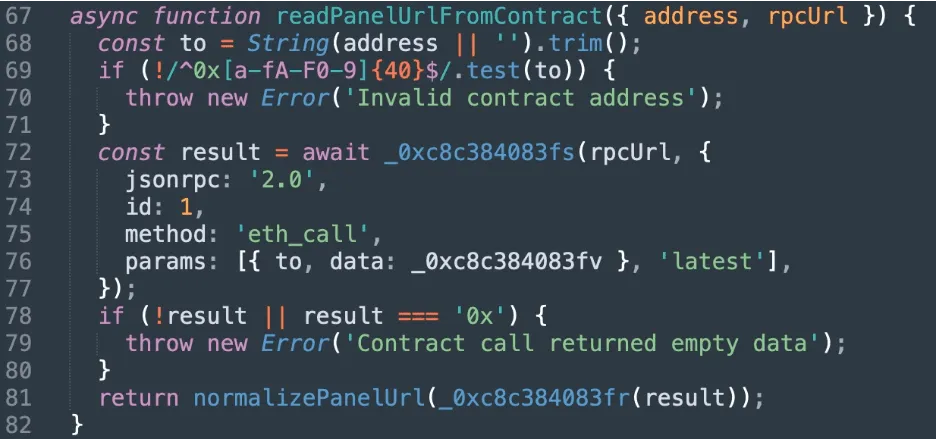 New ChainScript RAT Exploits ClickFix Lures with Blockchain C2 A newly discovered Node.js remote access trojan (RAT) named ChainScript is being deployed through ClickFix social engineering tactics, targeting Windows systems. The malware utilizes a unique command-and-control (C2) discovery method by querying a Polygon blockchain smart contract to dynamically rotate its server…
 Cybercriminals Exploit ChatGPT Custom GPTs for ClickFix RAT Attacks A new ClickFix campaign has been discovered that exploits ChatGPT Custom GPTs to impersonate legitimate products, luring users into executing malicious code. Cybersecurity firm Huntress reported that at least 40 users have been infected, with two confirmed incidents linked to Custom GPT instances. The attackers…