 Gbhackers
ClickFix Campaign Hijacks Facebook Sessions via Fake Verification Pages
Article Content
Browse articles 
The ClickFix campaign exploits social engineering techniques to steal Facebook session tokens from users. By guiding victims through a fake verification process, attackers have successfully extracted live session credentials directly from browsers. This campaign has expanded significantly since early 2025, with researchers identifying numerous malicious webpages involved in the attack.
Ask AI about this cluster
Answers cite the sources they use
Updated 201d ago How this analysis works
Timeline
2025-01-01
Campaign growth noted since early 2025
Recent
Attackers launched ClickFix campaign
Date unknown
115 malicious webpages identified
More articles in this cluster (2)
Continue Reading
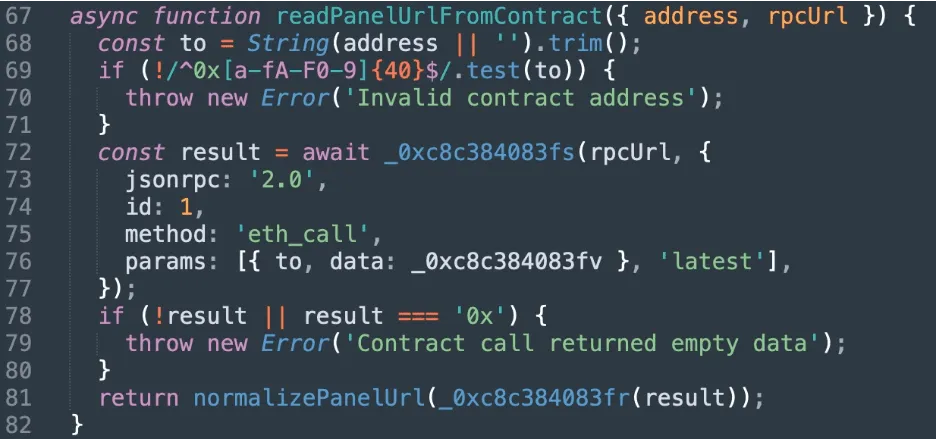 New ChainScript RAT Exploits ClickFix Lures with Blockchain C2 A newly discovered Node.js remote access trojan (RAT) named ChainScript is being deployed through ClickFix social engineering tactics, targeting Windows systems. The malware utilizes a unique command-and-control (C2) discovery method by querying a Polygon blockchain smart contract to dynamically rotate its server…
 Cybercriminals Exploit ChatGPT Custom GPTs for ClickFix RAT Attacks A new ClickFix campaign has been discovered that exploits ChatGPT Custom GPTs to impersonate legitimate products, luring users into executing malicious code. Cybersecurity firm Huntress reported that at least 40 users have been infected, with two confirmed incidents linked to Custom GPT instances. The attackers…