 Securityaffairs.Co
Cookeville Medical Center Data Breach Affects Over 337,000 Patients
Article Content

- •Over 337,000 patients affected by the CRMC ransomware attack.
- •Rhysida group claimed responsibility, demanding 10 Bitcoin as ransom.
- •CRMC is offering 12 months of identity theft protection to affected individuals.
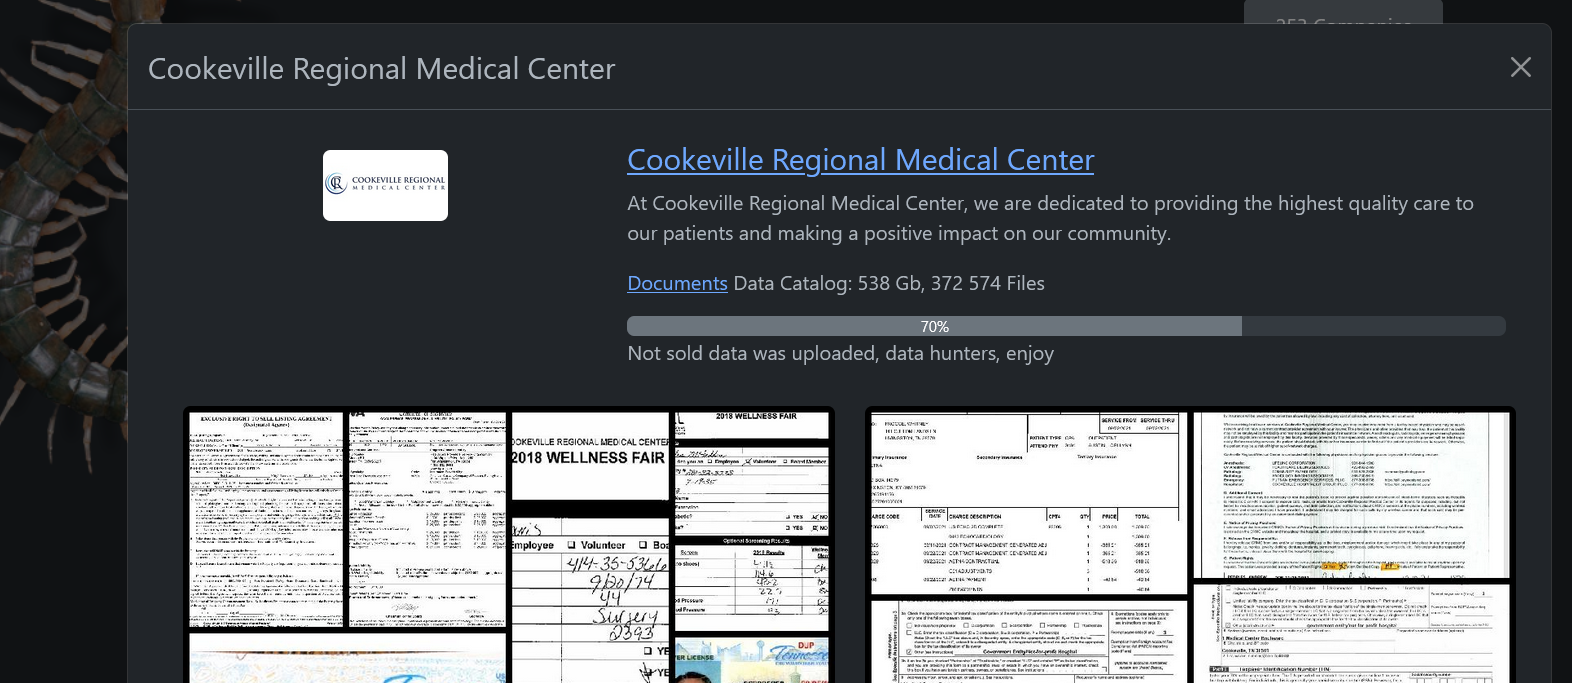
Cookeville Regional Medical Center (CRMC) in Tennessee reported a ransomware attack that compromised the personal and medical data of 337,917 patients. The attack occurred between July 11 and July 14, 2025, and was attributed to the Rhysida ransomware group, which demanded a ransom of 10 Bitcoin, valued at approximately $1.15 million at the time. The hospital began notifying affected individuals on April 14, 2026, nearly nine months after the breach was detected. Data accessed may include sensitive information such as Social Security numbers, medical records, and financial details. CRMC is offering 12 months of free identity theft protection to affected patients. This incident is noted as the eighth-largest healthcare ransomware breach in the U.S. for 2025. The hospital has implemented additional security measures since the attack. The lengthy notification period reflects the extensive forensic investigation required to assess the breach's impact.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (5)
Following this threat?
Track Rhysida and Cookeville Regional Medical Center in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Anne Arundel County Faces Second Cyberattack in 18 Months Anne Arundel County, Maryland, confirmed a data breach on August 28, 2026, where hackers accessed and copied files from a limited number of government systems. The Rhysida ransomware gang claimed responsibility, threatening to leak 2.6 terabytes of documents unless a $2 million ransom is paid. County officials stated…
 Critical BeyondTrust 9.3 Vulnerability Actively Exploited by Threat Actor A critical vulnerability (CVE-2026-102764) in BeyondTrust Remote Support has been discovered and is actively being exploited by the threat group ARMORY CASTLE, reportedly linked to China. The vulnerability, which has a CVSS score of 9.3, allows unauthenticated attackers to upload files and potentially compromise host…