 Malwarebytes
Critical Chrome Zero-Day CVE-2026-85046 Exploited in the Wild
Article Content

- •CVE-2026-85046 is a high-severity zero-day vulnerability in Chrome's V8 engine.
- •Exploitation allows remote code execution via malicious HTML pages.
- •Google has confirmed active exploitation in the wild and recommends immediate updates.
Google has released an emergency update for Chrome to address CVE-2026-85046, a high-severity zero-day vulnerability in the V8 JavaScript and WebAssembly engine, rated 8.8 on the CVSS scale. The flaw, identified as a type confusion issue, allows remote attackers to execute arbitrary code within Chrome's sandbox by tricking users into visiting specially crafted HTML pages. This vulnerability is the sixth zero-day patched by Google in 2026, following previous exploits including CVE-2026-2441 and CVE-2026-5281. The update is being rolled out for Chrome versions 152.0.7977.82/.83 for Windows and macOS, and 152.0.7977.82 for Linux. Security researcher Salvatore Gulizia reported the flaw on August 4, 2026, and received a $1,000 bug bounty. Google has confirmed that the exploit is actively being used in the wild, prompting immediate action from users to update their browsers. Organizations are advised to apply the updates as soon as they are available to mitigate risks.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (103)
Following this threat?
Track Google and CVE-2026-0768 in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
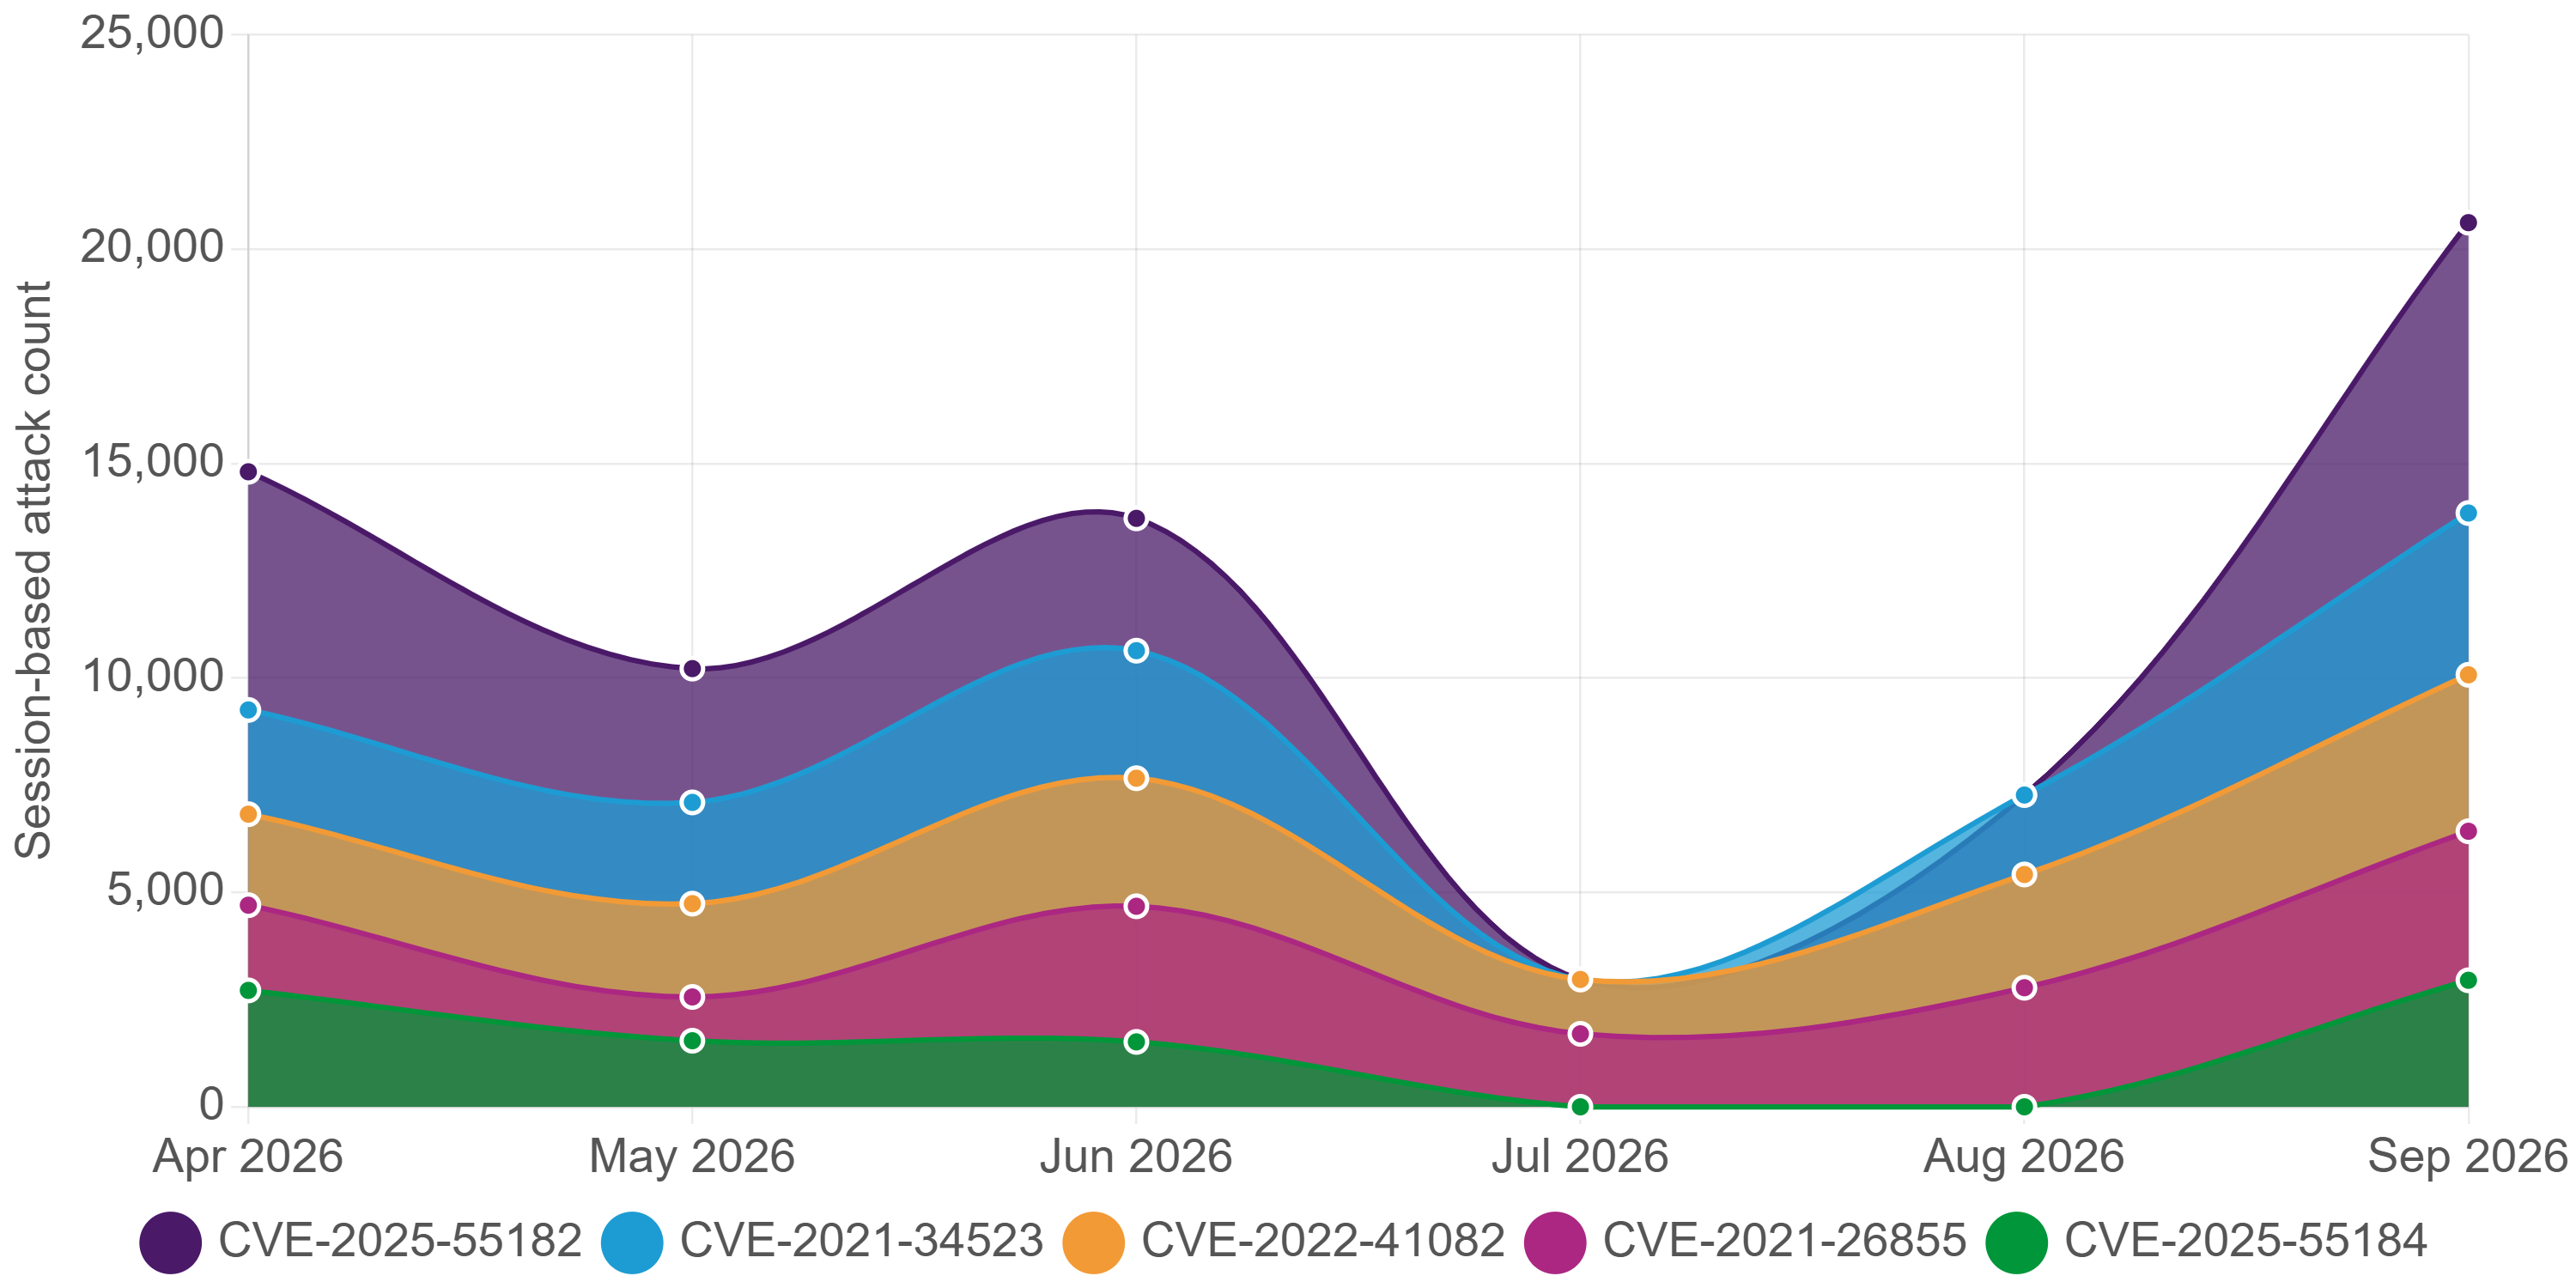 Langflow AI Platform Targeted by RCE Exploitation In September 2026, the Langflow AI application-building platform faced significant exploitation attempts targeting CVE-2026-0768, an unauthenticated remote code execution vulnerability. F5 Labs reported 405 requests from 55 distinct source IPs, indicating a coordinated effort to exploit this flaw. The vulnerability…
 Langflow CVE-2026-0768 Exploited in Credential Theft Campaign CVE-2026-0768, an unauthenticated remote code execution vulnerability in Langflow, is being, allowing attackers to execute arbitrary code with root privileges. As of October 6, 2026, VulnCheck reported over 360 exploitation attempts, primarily targeting environment variables such as AWS secrets and OpenAI API keys.…