 Scworld
Critical Vulnerabilities and Exploits Targeting Cisco, Canvas, and Microsoft Systems
Article Content

- •CVE-2026-20182 allows unauthenticated admin access on Cisco devices, with active exploitation reported.
- •Canvas LMS was defaced by ShinyHunters, claiming to possess 275 million records from educational institutions.
- •Critical XSS vulnerabilities in Microsoft Exchange are being actively exploited through crafted emails.
A series of critical vulnerabilities have emerged, including CVE-2026-20182, which allows unauthenticated attackers to gain admin access to Cisco Catalyst SD-WAN Controllers. ShinyHunters defaced the Canvas LMS login page, claiming to have 275 million records from around 9,000 educational institutions. An XSS flaw in on-prem Exchange is being exploited via crafted emails, affecting Outlook Web Access users. Two unpatched Windows zero-days have been disclosed, including YellowKey, which bypasses BitLocker encryption, and GreenPlasma, which escalates privileges. Additionally, malicious npm package updates have compromised OpenAI employee laptops, exposing limited internal credentials. Microsoft has addressed 118 vulnerabilities, but no emergency patches were issued this month. The time-to-exploit for vulnerabilities in AI infrastructure is now effectively zero, highlighting the urgency for immediate action.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track shinyhunters, Shai-hulud and Instructure in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
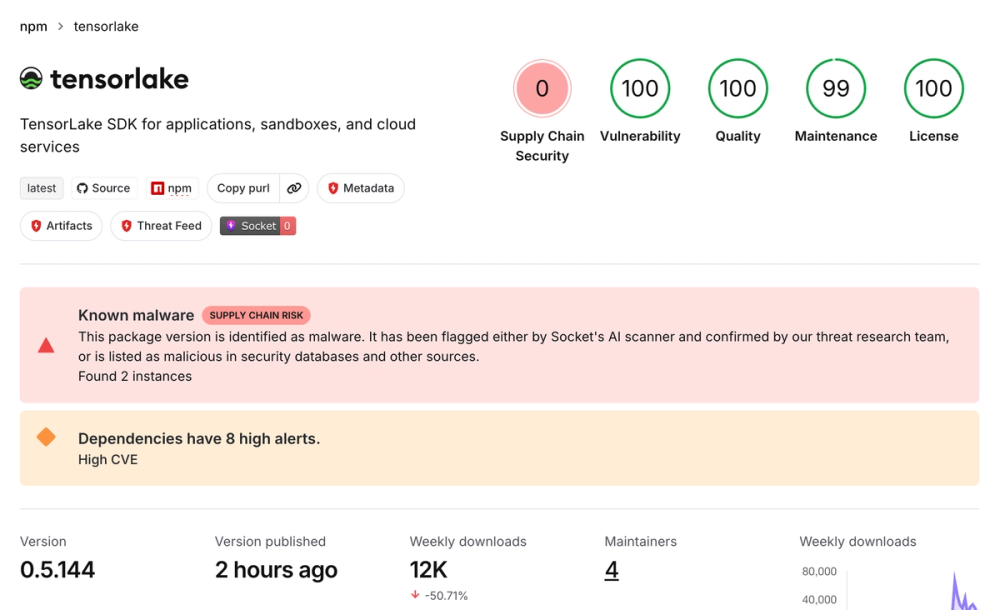 Tensorlake npm Package Compromised by Shai-Hulud Worm On October 8, 2026, the Tensorlake npm package version 0.5.144 was compromised, delivering a credential-stealing worm known as Shai-Hulud. The malware, which was published through a compromised maintainer account, executes a preinstall hook that runs an obfuscated loader to harvest credentials from local files and CI…
 Cisco Email Bug Exploited as Zero-Day by Unknown Actors A zero-day vulnerability in Cisco's email system has been by unknown criminals. The flaw, described as a 'make-me-root' bug, allows attackers to gain root access via email. Cisco has not disclosed specific details about the vulnerability or the affected systems. The exploit is reportedly being used in the wild…