 www.claroty.com
Critical Vulnerabilities Found in Vertiv UPS Network Cards
Article Content

- •Two critical vulnerabilities (CVE-2025-46412, CVE-2025-41426) found in Vertiv UPS network cards.
- •Exploits could allow attackers to disrupt power operations and execute arbitrary code.
- •Vertiv recommends immediate firmware updates to mitigate these vulnerabilities.
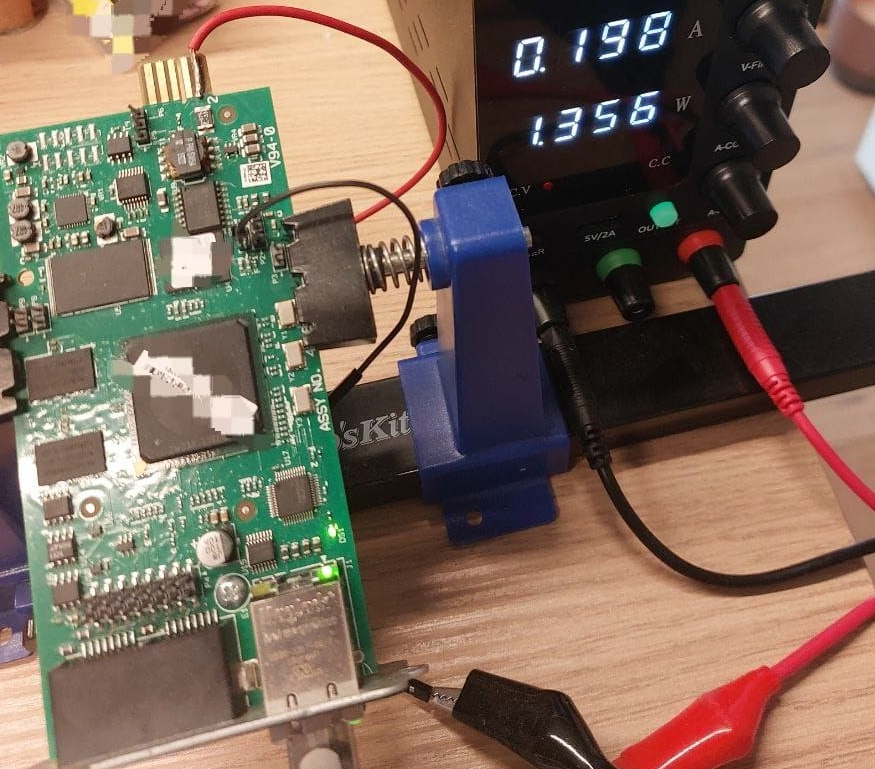
Team82 identified two critical vulnerabilities in Vertiv's Liebert IS-UNITY-DP network cards, both rated 9.8 on the CVSSv3 scale. The vulnerabilities, CVE-2025-46412 and CVE-2025-41426, allow for authentication bypass and remote code execution, posing significant risks to data centers reliant on these uninterruptible power supply (UPS) devices. Successful exploitation could enable attackers to disrupt power operations and execute arbitrary code, potentially affecting entire facilities. Vertiv has released firmware updates to mitigate these vulnerabilities, urging users to upgrade to specific versions. The vulnerabilities were disclosed on June 9, 2026, and are critical for organizations using Vertiv UPS systems.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (5)
Following this threat?
Track Trane and CVE-2025-41426 in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Critical BeyondTrust 9.3 Vulnerability Actively Exploited by Threat Actor A critical vulnerability (CVE-2026-102764) in BeyondTrust Remote Support has been discovered and is actively being exploited by the threat group ARMORY CASTLE, reportedly linked to China. The vulnerability, which has a CVSS score of 9.3, allows unauthenticated attackers to upload files and potentially compromise host…