 Ground.News
Cybercriminals Shift Domains, Maintain Malware Hosting Networks
Article Content

- •Cybercriminals are using a stable hosting network while frequently changing lure domains.
- •The ClickFix technique employs social engineering to execute commands on victims' machines.
- •Static IP blocklists are becoming ineffective against these evolving malware campaigns.
Cybercriminals are rapidly rotating lure domains and command-and-control channels while maintaining a stable bulletproof hosting network, AS202412, operated by OMEGATECH LTD. Over five months, researchers identified four distinct malware delivery chains linked to this network, highlighting the difficulty of blocking individual domains. The initial access method, ClickFix, uses social engineering to trick victims into executing malicious commands via the Windows Run dialog. This technique circumvents traditional defenses focused on file downloads and suspicious links. The observed lure domains often feature predictable naming patterns, allowing attackers to quickly switch to new domains without significant cost. The infrastructure's resilience poses a growing challenge for cybersecurity defenses, as static IP blocklists become less effective due to frequent changes in address space.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Following this threat?
Track ClickFix and Omegatech LTD in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Russia's AI-Driven Cyber Espionage Targets Ukraine and Europe A Russian-linked hacking group, identified as GTG-20006, has utilized Anthropic's Claude AI to automate cyber espionage against over 20 organizations, primarily in Ukraine and Europe. The group targeted Ukrainian government officials, military personnel, and drone manufacturers through sophisticated phishing and…
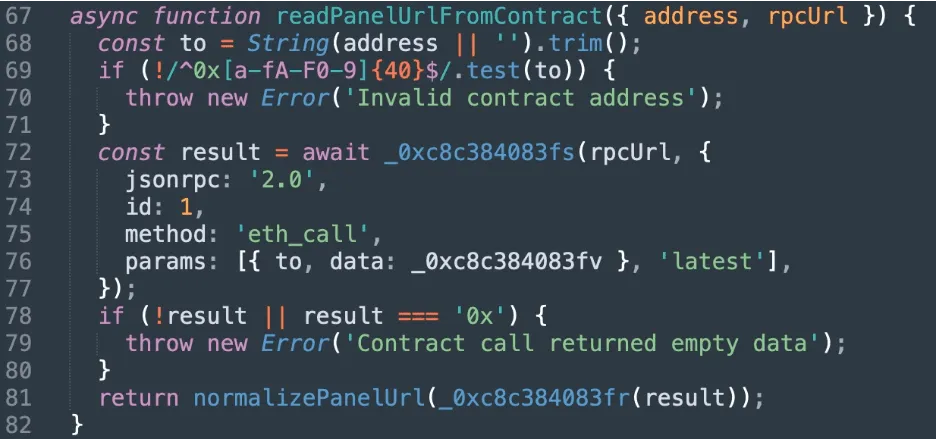 New ChainScript RAT Exploits ClickFix Lures with Blockchain C2 A newly discovered Node.js remote access trojan (RAT) named ChainScript is being deployed through ClickFix social engineering tactics, targeting Windows systems. The malware utilizes a unique command-and-control (C2) discovery method by querying a Polygon blockchain smart contract to dynamically rotate its server…