 www.prophetsecurity.ai
Cybersecurity Alert Fatigue: A Growing Challenge for SOCs
Article Content

- •SOCs receive an average of 2,992 alerts daily, with 63% going unaddressed.
- •Alert fatigue leads to degraded investigation quality and increased risk of missed threats.
- •Structural solutions are needed to address the root causes of alert fatigue.
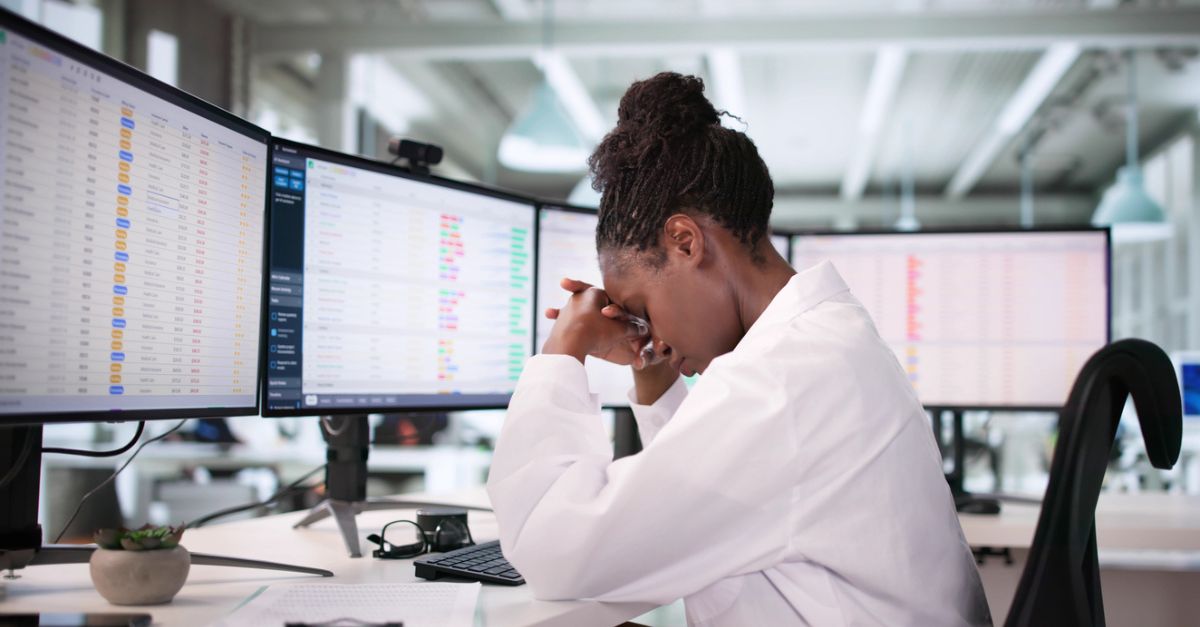
Security Operations Centers (SOCs) are facing significant alert fatigue, with an average of 2,992 security alerts generated daily, leading to 63% going unaddressed. This phenomenon, akin to alarm fatigue in healthcare, results in analysts missing critical threats due to overwhelming volumes of alerts. The issue is compounded by false positives, tool sprawl, and staffing shortages, which degrade the quality of threat detection. While the volume of alerts has decreased from previous years, the problem persists, with 76% of organizations citing alert fatigue as a primary concern. Analysts are struggling to keep up, often making hasty decisions that can overlook genuine threats. Addressing alert fatigue requires structural solutions rather than just increasing analyst headcount or tuning alerts. The current state of alert management is critical for maintaining cybersecurity effectiveness.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Following this threat?
Track Equifax and CVE-2017-5638 in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Surge in Cyber Incidents Targeting Japanese Web Systems As of October 6, 2026, Japan has reported 119 incidents of information leakage from corporate web systems, a significant increase since July 2026. This surge, accounting for 68% of the year's reported incidents, raises concerns among security experts due to its unusual nature compared to past cyberattacks. The…
 Brotli Decoder Vulnerability Patched Across Multiple Linux Distributions A vulnerability, CVE-2026-111497, affecting the Brotli decoder has been patched in various Linux distributions, including Fedora 44 and Oracle Linux 10. The flaw allows for an out-of-bounds write, which could potentially enable attackers to execute arbitrary code. The vulnerability was published on October 22, 2026…