 Clickorlando
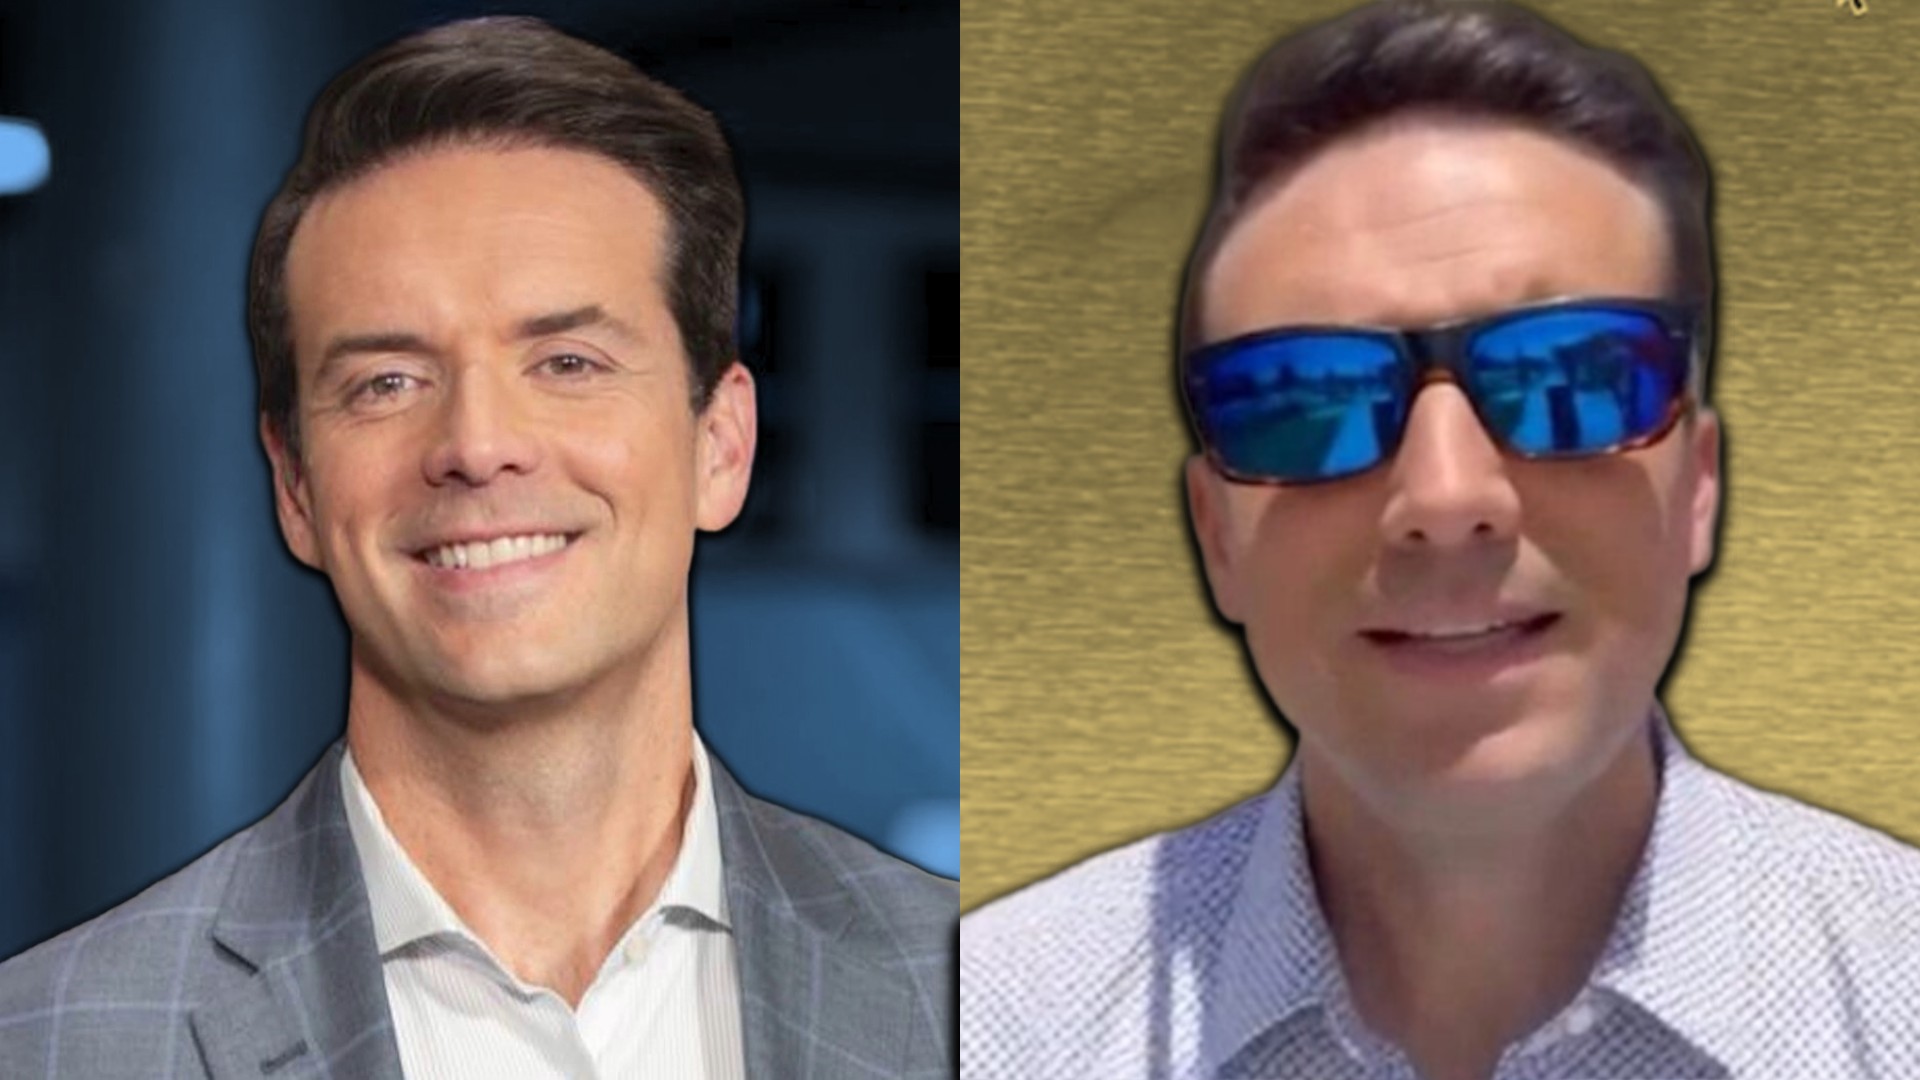
Deepfake Technology Used to Impersonate News Anchor Matt Austin
Article Content

- •Deepfake technology can convincingly impersonate public figures using their online content.
- •The demonstration took only 45 minutes to create a fake video of anchor Matt Austin.
- •Public figures are particularly vulnerable to deepfake scams and misinformation.
At the KB4-CON cybersecurity conference, a demonstration revealed how a man could create a convincing deepfake of News 6 anchor Matt Austin using publicly available videos. Perry Carpenter, a Chief Deception Strategist, showcased the ability to manipulate Austin's likeness and voice to make him appear to endorse a meme coin. This process took only 45 minutes and highlighted the risks of deepfake technology, particularly for public figures. Carpenter warned that such deepfakes could be used for scams, blackmail, or misinformation, potentially damaging reputations and financial security. The incident underscores the vulnerability of individuals who share content online, as their digital presence can be exploited for malicious purposes. The demonstration also included real-time impersonation, further illustrating the technology's capabilities. The event serves as a cautionary tale about the blurred lines between reality and deception in the digital age.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Continue Reading
 Critical Zero-Day Vulnerability in Cisco Secure Email Gateway Exploited On September 14, 2026, Cisco disclosed a critical SQL injection vulnerability (CVE-2026-76461) in its Secure Email Gateway, allowing unauthenticated remote attackers to execute arbitrary commands with root privileges. This vulnerability arises from insufficient validation in the email parsing logic. Cisco confirmed…
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…