 Ans
DOE Approves Xcimer's Laser Fusion Power Plant Design
Article Content

- •The DOE approved Xcimer Energy's Athena fusion power plant design.
- •Xcimer aims for laser costs under $100 per joule with simplified technology.
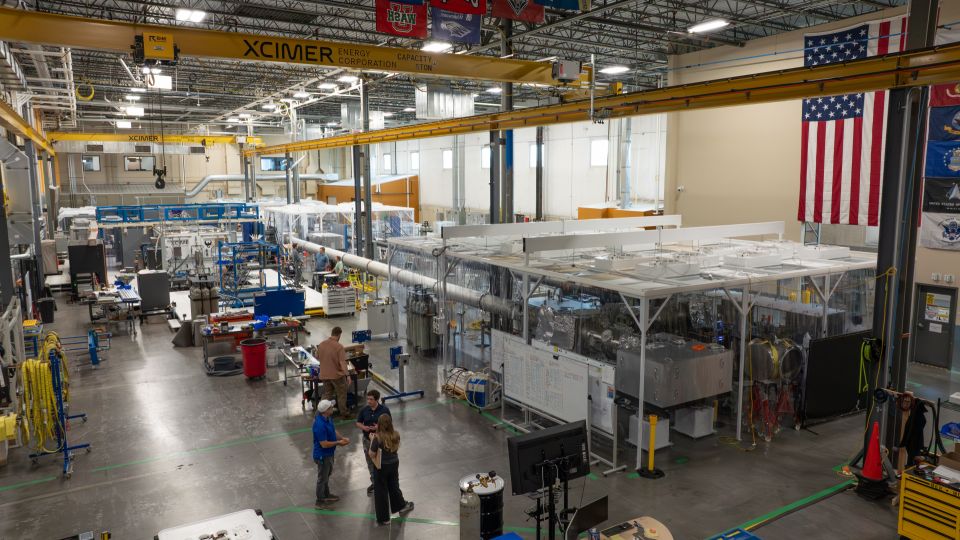
- •Phoenix, Xcimer's prototype, is the largest privately owned laser system worldwide.
The Department of Energy has approved the preconceptual technical design for Xcimer Energy's Athena fusion power plant. This marks a significant step for the Denver-based company in developing economical laser inertial confinement fusion technology. Xcimer aims to simplify and reduce costs associated with laser systems, targeting costs under $100 per joule. The company has completed earlier program milestones under the DOE's Milestone-Based Fusion Development Program. Xcimer's prototype, Phoenix, is the largest privately owned laser system globally and serves as a proof of concept for their fusion architecture. The project is backed by venture capital and technical expertise from the U.S. Naval Research Laboratory. The Athena design includes a molten salt fusion chamber and two beamlines, enhancing scalability and efficiency. The approval allows Xcimer to proceed with subsystem testing and engineering validation for an integrated plant demonstration.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…