 www.greynoise.io
Exploitation of Langflow Flaws via Commodity Crawlers
Article Content

- •Two CVEs (CVE-2025-3248, CVE-2026-0770) exploited in Langflow with thousands of attempts.
- •95% of attacks traced to two hosting providers, indicating concentrated malicious activity.
- •Significant SSH and Remote Desktop crawling observed, emphasizing the need for immediate patching.
Adversaries have exploited two known remote code execution vulnerabilities in the AI application platform Langflow, specifically CVE-2025-3248 and CVE-2026-0770. These exploits were detected during a period of active commodity crawling, with 3,968 and 4,770 connection attempts recorded respectively. Approximately 95% of the malicious activity originated from two hosting providers, indicating a concentrated source of attacks. The attackers also engaged in SSH enumeration and credential attacks, with four hosts accounting for 36% of alternative-port SSH crawling. Additionally, one address was responsible for over half of the Remote Desktop crawling observed. GreyNoise has advised users to patch Langflow and monitor the identified sources for malicious activity. The vulnerabilities were added to CISA's Known Exploited Vulnerabilities catalog, highlighting their active exploitation status.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Langflow and CVE-2025-3248 in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Multiple High-Risk Vulnerabilities Found in IBM Langflow OSS IBM Langflow OSS versions 1.0.0 through 1.12.2 are affected by several vulnerabilities, including CVE-2026-93443, CVE-2026-93445, CVE-2026-97676, and others, which allow remote authenticated attackers to execute arbitrary code or access sensitive information. The vulnerabilities stem from improper control of code…
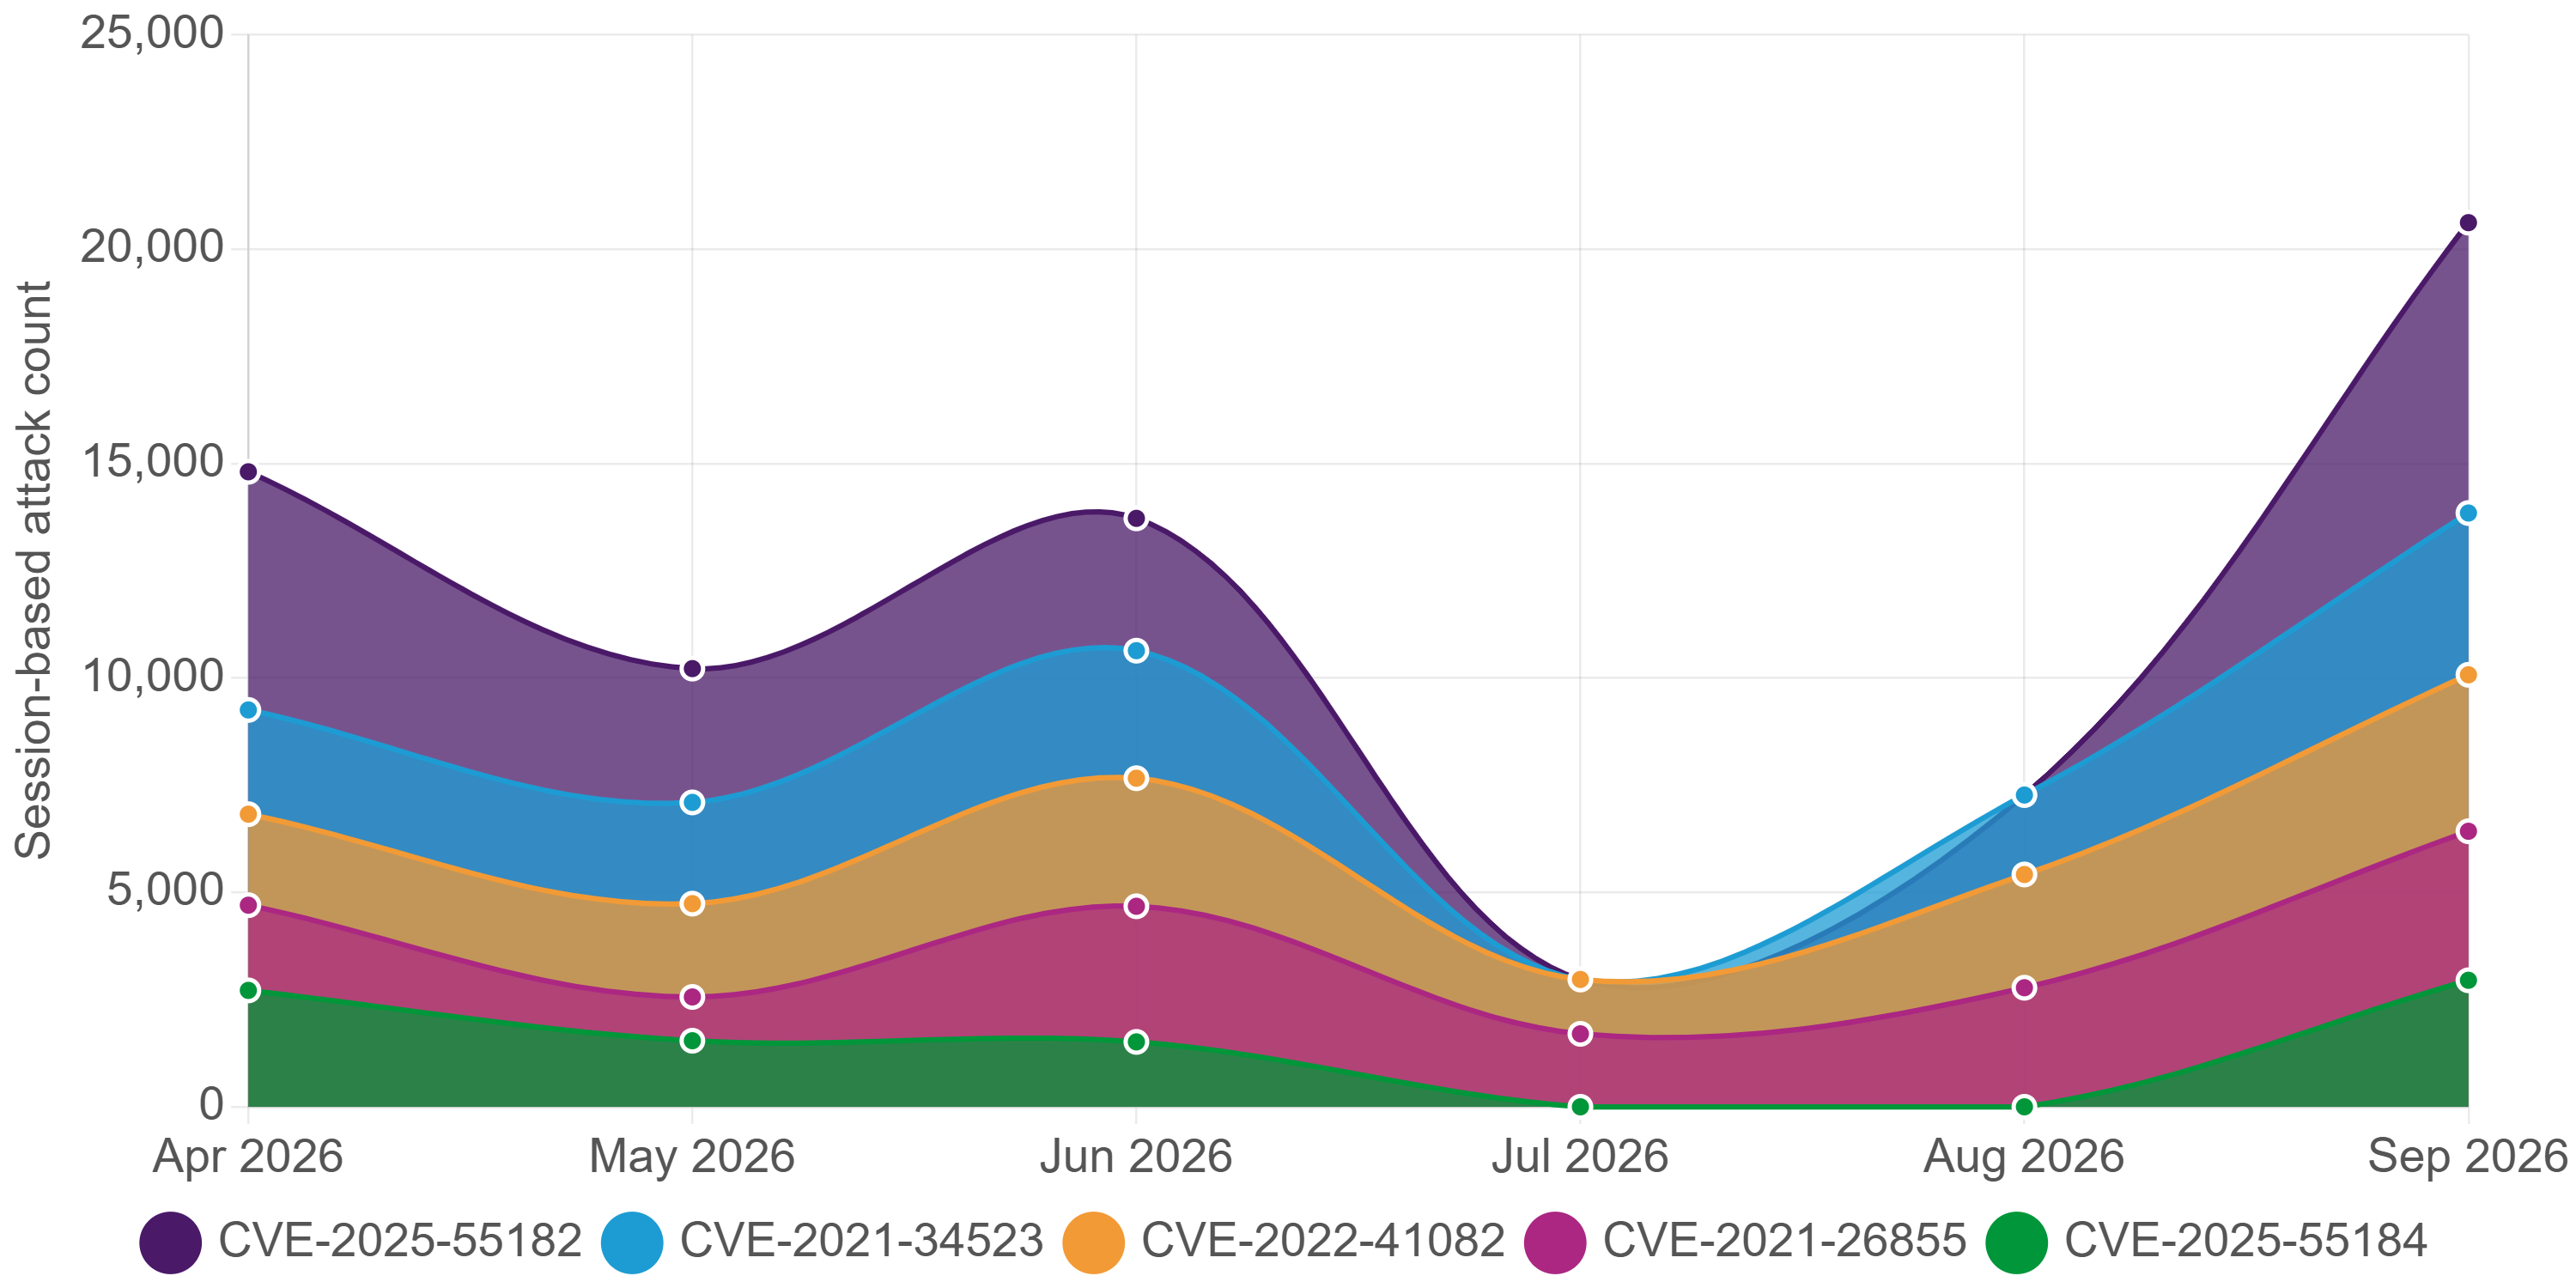 Langflow AI Platform Targeted by RCE Exploitation In September 2026, the Langflow AI application-building platform faced significant exploitation attempts targeting CVE-2026-0768, an unauthenticated remote code execution vulnerability. F5 Labs reported 405 requests from 55 distinct source IPs, indicating a coordinated effort to exploit this flaw. The vulnerability…