Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
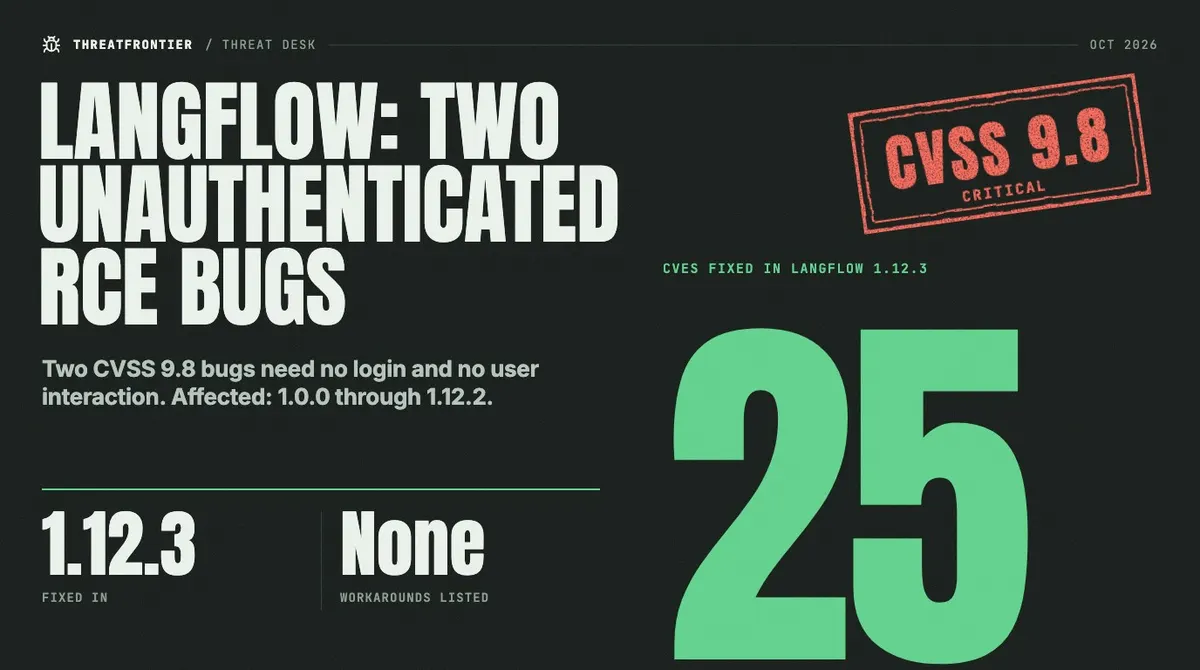
Adversaries have exploited two known remote code execution vulnerabilities in the AI application platform Langflow, specifically CVE-2025-3248 and CVE-2026-0770. These exploits were detected during a period of active commodity crawling, with 3,968 and 4,770 connection attempts recorded respectively....
IBM Langflow OSS versions 1.0.0 through 1.12.2 are affected by several vulnerabilities, including CVE-2026-93443, CVE-2026-93445, CVE-2026-97676, and others, which allow remote authenticated attackers to execute arbitrary code or access sensitive information. The vulnerabilities stem from improper c...
BeyondTrust has issued a warning regarding a critical remote code execution (RCE) vulnerability in its Remote Support and Privileged Remote Access software. The flaw, tracked as CVE-2026-1731, allows unauthenticated attackers to execute arbitrary code remotely and affects versions 25.3.1 or earlier...