 Thepoint.Gm
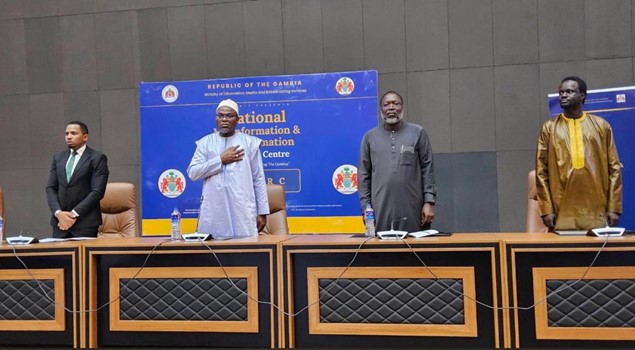
Gambia Launches National Centre to Combat Misinformation
Article Content

- •The NMDRC is the first national response mechanism against misinformation in West Africa.
- •The initiative aims to rebuild public trust and protect democratic integrity in The Gambia.
- •ECOWAS supports the Centre, highlighting its regional significance in combating digital misinformation.
On April 25, 2026, The Gambia inaugurated the National Misinformation and Disinformation Response Centre (NMDRC) in Banjul, marking a significant step in addressing the rapid spread of misinformation in the digital age. With 1.3 million Gambians online, officials highlighted the urgent need to combat false narratives that can damage reputations and erode public trust. The NMDRC aims to provide a platform for citizens to verify information and access accurate content, thereby supporting democracy and community cohesion. This initiative, backed by ECOWAS, is the first of its kind in West Africa and is designed to facilitate real-time fact-checking and cross-border collaboration. The Vice President emphasized that the Centre is not a tool for censorship but a means to empower citizens with verified information. The launch reflects a commitment to transparency and accountability in governance, as misinformation poses a growing threat to democratic processes.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…