 Independent
Hezbollah Deploys Fiber-Optic Drones Against Israel in Ongoing Conflict
Article Content

- •Hezbollah's fiber-optic drones are immune to electronic jamming, posing a new threat to Israel.
- •Recent attacks have resulted in one Israeli soldier killed and over a dozen injured.
- •The drones are believed to be locally manufactured and easy to produce.
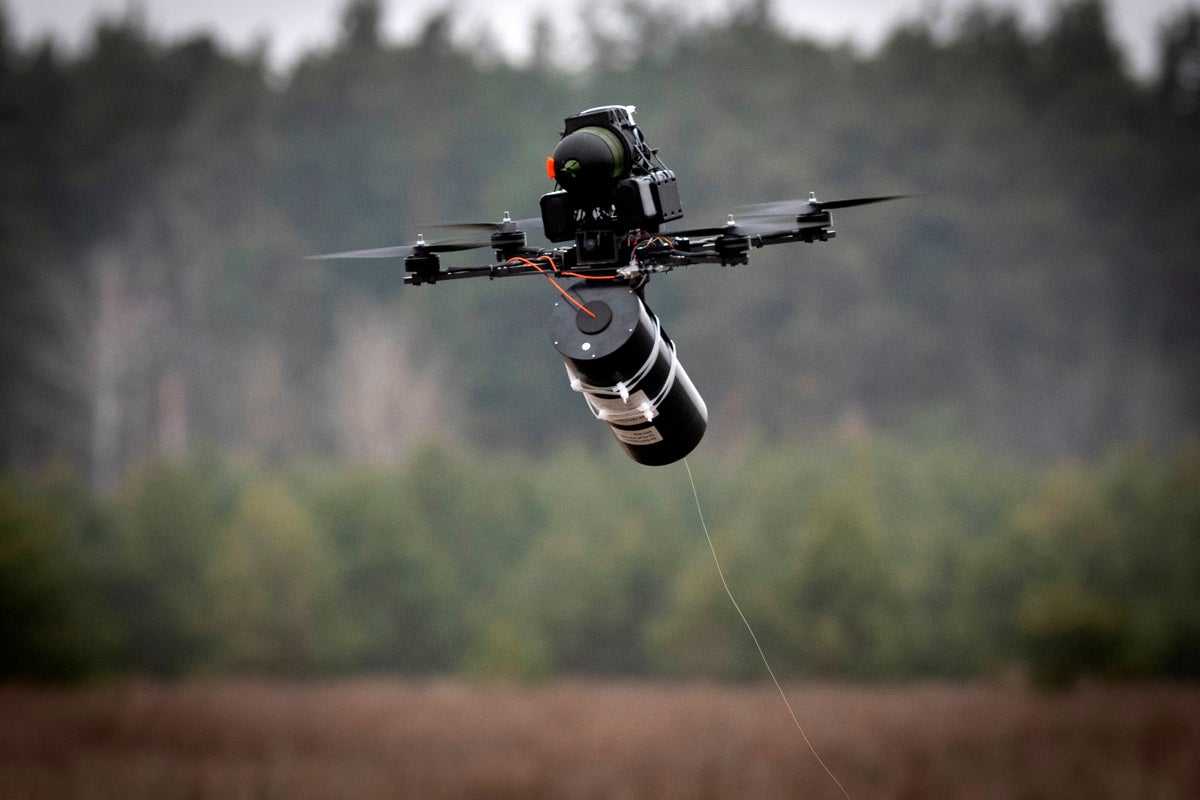
Hezbollah has introduced fiber-optic drones as a new weapon against Israeli forces in northern Israel, marking a significant escalation in the ongoing conflict. These small drones, controlled by cables the width of dental floss, evade electronic detection, making them a formidable challenge for Israeli air defenses. In recent attacks, these drones have resulted in the death of an Israeli soldier and injuries to at least a dozen others. The drones are difficult to intercept due to their small size and low flight paths, and they are immune to electronic jamming, a common vulnerability for many drones. Israeli military officials acknowledge that Hezbollah's use of these drones represents a new and serious threat, particularly as Israel's defenses have been effective against larger missiles and drones. The fiber-optic drones are believed to be locally produced and easy to manufacture, raising concerns about their proliferation. Israel is currently working on technological solutions to counter this new threat while also implementing ground measures to protect its troops. The situation continues to evolve as both sides adapt to the changing dynamics of warfare.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (24)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…