 Bastillepost
Hong Kong Launches Cybersecurity Initiatives Amid AI Adoption Challenges
Article Content

- •Hong Kong's Digital Policy Office launched new cybersecurity initiatives for 2026.
- •Focus on AI-related security measures due to increased AI technology adoption.
- •Community engagement activities include phishing exercises and an AI x Cybersecurity Challenge.
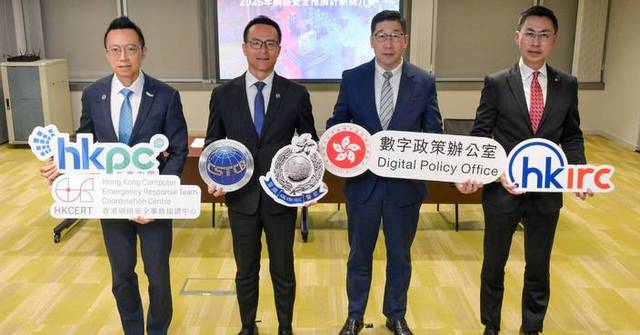
On June 2, 2026, Hong Kong's Digital Policy Office unveiled key cybersecurity initiatives for the second half of the year. The initiatives aim to bolster cybersecurity awareness and resilience in response to the rising integration of AI technologies. The DPO highlighted past efforts, including phishing exercises and community engagement activities. Future plans include the Secure AI@Work Enablement Campaign and the AI x Cybersecurity Challenge, focusing on AI-related security measures. The Cyber Security Summit and Symposium will also be integrated into a single event in December 2026. The Acting Commissioner emphasized a balanced approach to security and development. The initiatives involve collaboration with industry partners to enhance overall cyber resilience.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Education in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…