 Thestatesman
India Condemns Pakistan's 'Fitna al Hindustan' Label at UN
Article Content

- •India condemned Pakistan's use of 'Fitna al Hindustan' to label militant groups.
- •The term is seen as part of a state-sponsored campaign to promote anti-India sentiment.
- •India also criticized Pakistan's military airstrikes in Afghanistan, highlighting civilian casualties.
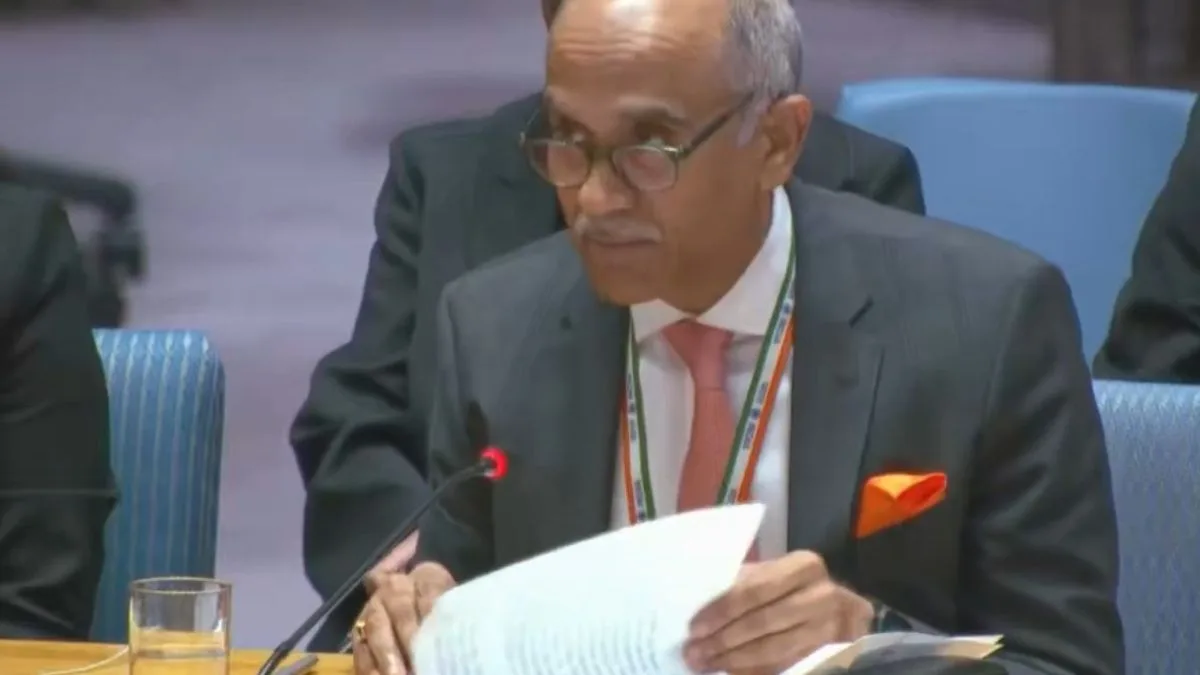
On June 9, 2026, India criticized Pakistan at the UN Security Council for labeling militant groups as 'Fitna al Hindustan', which India claims is a tactic to institutionalize anti-India rhetoric. India's Permanent Representative, Harish Parvathaneni, described this move as state-sponsored misinformation aimed at fostering hostility among Pakistani citizens. He asserted that such narratives serve to distract from Pakistan's internal political and economic issues. The term was officially adopted by Pakistan in 2025 for terrorist groups in Balochistan. India also condemned Pakistan's military actions in Afghanistan, highlighting the humanitarian impact of these operations. The ongoing tensions reflect a broader pattern of geopolitical strife in South Asia, with implications for regional security and counter-terrorism efforts. The situation remains dynamic as international discussions continue.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Continue Reading
 Critical Zero-Day Vulnerability in Cisco Secure Email Gateway Exploited On September 14, 2026, Cisco disclosed a critical SQL injection vulnerability (CVE-2026-76461) in its Secure Email Gateway, allowing unauthenticated remote attackers to execute arbitrary commands with root privileges. This vulnerability arises from insufficient validation in the email parsing logic. Cisco confirmed…
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…