 Iranintl
Iran Demands Release of $12B Frozen Assets in US Negotiations
Article Content
Browse articles 
- •Iran demands $12 billion in frozen assets from Qatar as a negotiation precondition.
- •Access to these funds is deemed crucial by Iranian officials for advancing US talks.
- •The negotiations are currently stalled, highlighting ongoing geopolitical tensions.
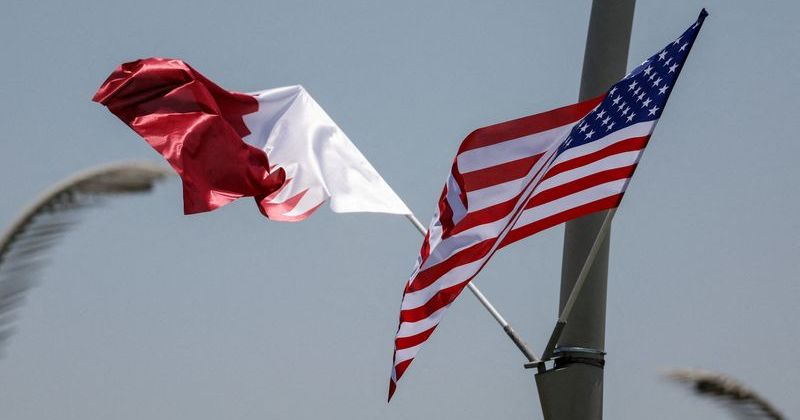
Iran is insisting on the immediate release of $12 billion in frozen assets held in Qatar as a prerequisite for advancing negotiations with the United States. This demand is central to ongoing discussions, with Iranian officials stating that guaranteed access to these funds is essential before any preliminary agreement can be reached. The situation highlights the geopolitical tensions surrounding financial negotiations between Iran and the US, particularly in the context of sanctions and diplomatic relations. As of now, no agreement has been finalized, and the negotiations remain stalled due to this key issue.
Ask AI about this cluster
Answers cite the sources they use
Updated 116d ago How this analysis works
Timeline
2026-05-24
Iran demands access to frozen assets
Iranian negotiators insist on the release of $12 billion in frozen assets as a precondition for US negotiations.
Iranintl2026-05-26
Qatar's role as broker highlighted
Qatar has emerged as a key broker in the dispute over frozen Iranian assets, crucial for US-Iran talks.
IranintlMore articles in this cluster (2)
Continue Reading
 Critical Zero-Day Vulnerability in Cisco Secure Email Gateway Exploited On September 14, 2026, Cisco disclosed a critical SQL injection vulnerability (CVE-2026-76461) in its Secure Email Gateway, allowing unauthenticated remote attackers to execute arbitrary commands with root privileges. This vulnerability arises from insufficient validation in the email parsing logic. Cisco confirmed…
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…