 Turkiyetoday
Israel Detains Gaza Flotilla Activists Amid Allegations of Torture
Article Content

- •Two activists from the Global Sumud Flotilla were detained by Israeli forces in international waters.
- •Allegations of torture and severe abuse have been reported by the activists' legal representatives.
- •Spain's Foreign Ministry has condemned the detention as illegal and demanded their release.
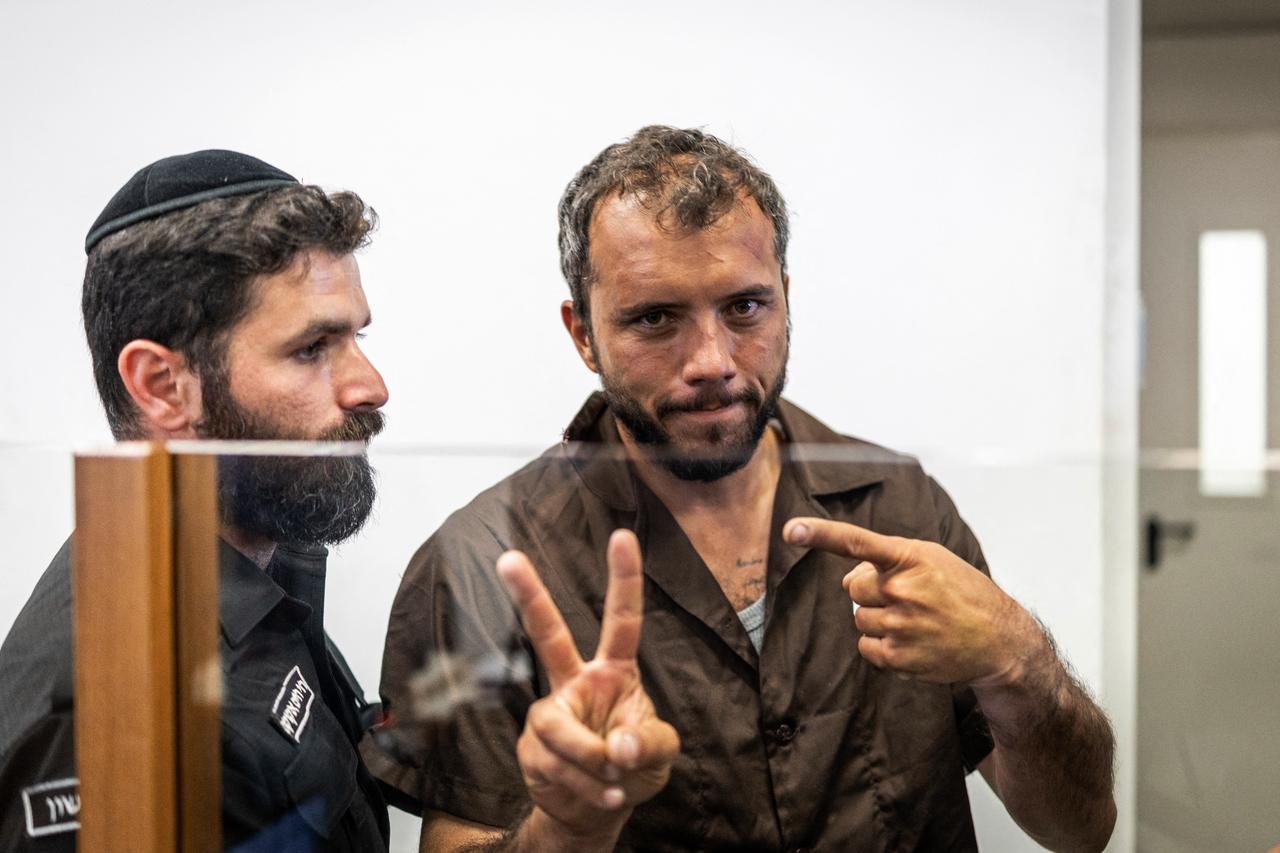
On May 2, 2026, Israeli forces intercepted the Global Sumud Flotilla in international waters, detaining activists Saif Abu Keshek and Thiago Avila. Both activists are accused of links to a group sanctioned by the U.S. Treasury, which is alleged to act on behalf of Hamas. An Israeli court extended their detention by two days on May 3, 2026, despite no formal charges being filed. Reports from their lawyers indicate that they have faced severe abuse and torture during their detention, including beatings and isolation. The Spanish Foreign Ministry has condemned their detention as illegal and called for their immediate release. The flotilla aimed to deliver humanitarian aid to Gaza, which has been under Israeli blockade since 2007. The situation has further strained diplomatic relations between Spain and Israel, already tense due to the ongoing Gaza conflict. The activists are currently held in Shikma Prison, continuing a hunger strike in protest of their treatment.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (20)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…