 Amp.Scmp
Japan Establishes National Intelligence Council Amid Privacy Concerns
Article Content

- •Japan's parliament passed a law to create a National Intelligence Council on May 27, 2026.
- •The council will centralize intelligence gathering to counter threats like cyberattacks and disinformation.
- •Concerns over civil liberties and lack of oversight were raised by opposition parties during the legislation process.
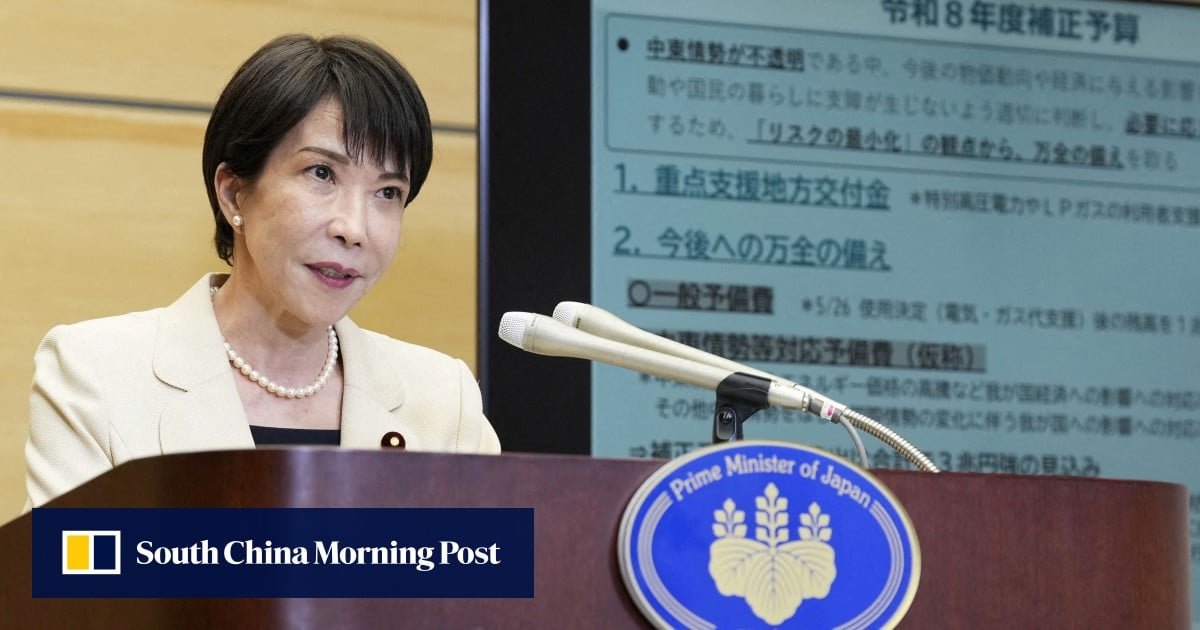
On May 27, 2026, Japan's parliament enacted a law to create a National Intelligence Council aimed at centralizing intelligence gathering to address overseas threats, including cyberattacks and election interference. The council, chaired by Prime Minister Sanae Takaichi, will coordinate intelligence from various government agencies, including the National Police Agency and the Defense Ministry. The legislation passed with support from the ruling coalition and some opposition parties, despite concerns about civil liberties and the lack of parliamentary oversight. The government plans to further enhance intelligence capabilities, with additional legislation expected in 2027. The establishment of the council is part of a broader security agenda in response to what is described as the most complex security environment since World War II. The law also includes a supplementary resolution emphasizing the protection of personal information and political neutrality in intelligence operations.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (12)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…