 Defensescoop
Lt. Gen. Doug Schiess Nominated as Chief of Space Operations
Article Content

- •Lt. Gen. Doug Schiess nominated as chief of space operations by President Trump.
- •Schiess aims to enhance Space Force capabilities and maintain strategic advantages.
- •The Space Force's fiscal 2027 budget request is its largest ever, indicating significant growth.
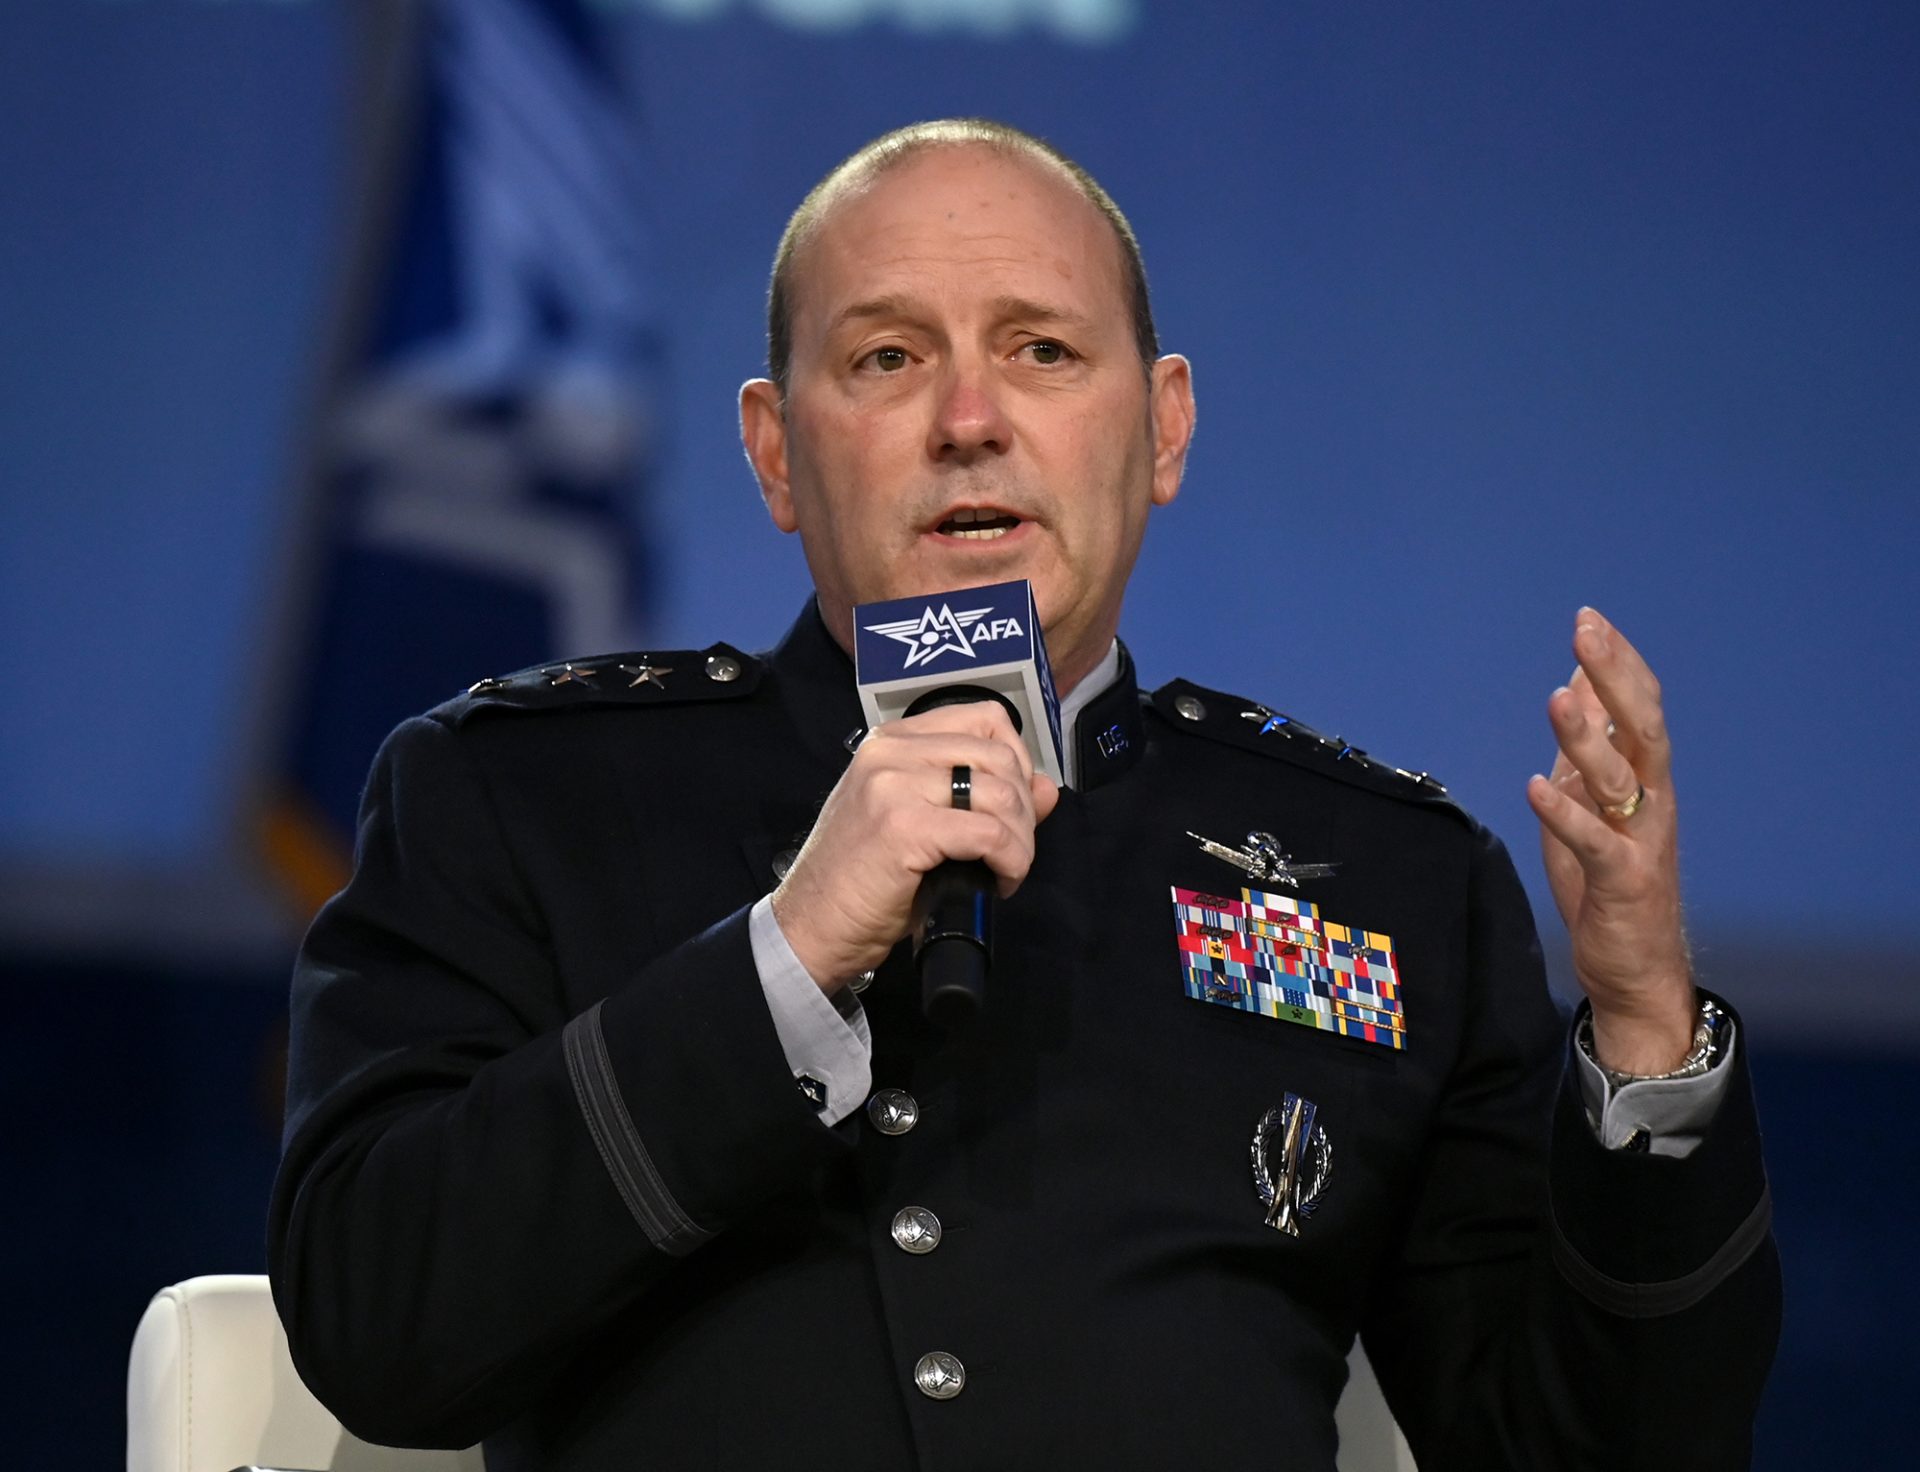
President Donald Trump has nominated Lt. Gen. Doug Schiess to be the next chief of space operations for the U.S. Space Force, as announced on May 1, 2026. Schiess, currently the deputy chief of operations, would succeed Gen. Chance Saltzman, who is expected to retire this year. If confirmed by the Senate, Schiess will focus on enhancing the Space Force's capabilities and maintaining its strategic advantage against adversaries. The Space Force is experiencing significant growth, with its fiscal 2027 budget request being the largest in its history, aimed at expanding its personnel and operational capabilities. Schiess has a robust background in military leadership, having previously commanded various operational components within the Space Force and U.S. Space Command. His nomination comes at a critical time as the Space Force takes on more mission areas, including missile defense. Saltzman praised Schiess as the right leader for the current challenges facing the Space Force.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…