 Hackread
Malicious Adobe Pages Distributing Remote Access Tool Identified
Article Content

- •Attackers use fake Adobe Acrobat pages to distribute legitimate remote access software.
- •The campaign exploits digitally signed installers with unauthorized configurations.
- •CloudSEK has identified multiple tenant configurations linked to the malicious activity.
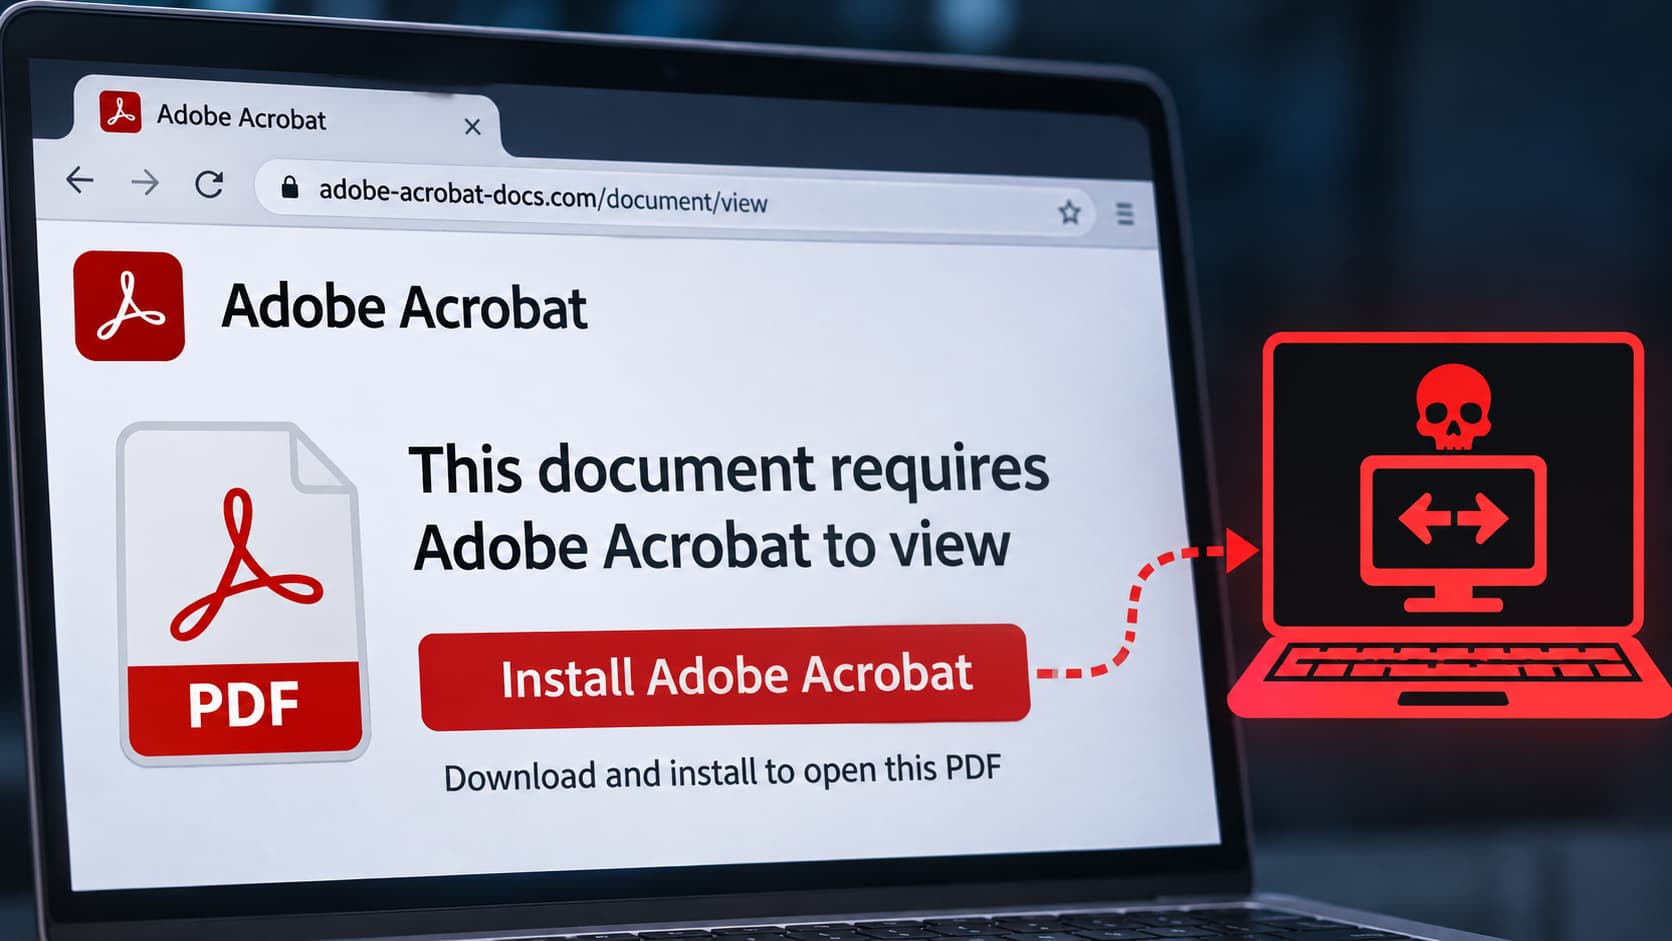
Cybersecurity researchers from CloudSEK have discovered a campaign using fake Adobe Acrobat pages to distribute legitimate ConnectWise ScreenConnect remote-access software. The attackers exploit digitally signed installers configured to connect to unauthorized tenants, potentially granting persistent access to Windows systems. The delivery mechanism involves deceptive document-review prompts that check visitor operating systems and collect sensitive information before automatically downloading the ScreenConnect client. The campaign has been linked to multiple tenant configurations, including omydze and vvvzou, with additional configurations identified. CloudSEK has not confirmed any victim compromises or the identity of the operators behind the campaign. Security teams are advised to monitor unauthorized ScreenConnect configurations and services.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Common questions
What software is being exploited?
How are victims targeted?
What should organizations do to protect themselves?
Continue Reading
 Critical RCE Vulnerability in Prefab UI Disclosed A critical remote code execution vulnerability, CVE-2026-120338, was disclosed on November 1, 2026, affecting Prefab UI's Generative UI sandbox. The flaw allows attackers to execute arbitrary Python code by exploiting Deno's permissions, enabling file read/write access on the host server. This vulnerability affects…
 Chinese Actor Compromises US Government Networks via PHP2Shell Exploit A suspected Chinese nation-state actor exploited vulnerabilities in Palo Alto Networks firewalls using a chained PHP2Shell exploit and a Linux kernel privilege escalation flaw. The attack, which began on October 23, targeted 25 servers across the US, Japan, Taiwan, and South Korea, with a focus on US…