 Foxnews
Malware Spread via Fake Windows Update in ClickFix Attack
Article Content
Browse articles 
A new ClickFix attack has emerged, distributing malware through a fake Windows update. Users are tricked into downloading malicious software that mimics legitimate system updates. This attack primarily targets Windows users, exploiting their trust in official update processes.
Ask AI about this cluster
Answers cite the sources they use
Updated 213d ago How this analysis works
More articles in this cluster (5)
Following this threat?
Track ClickFix in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
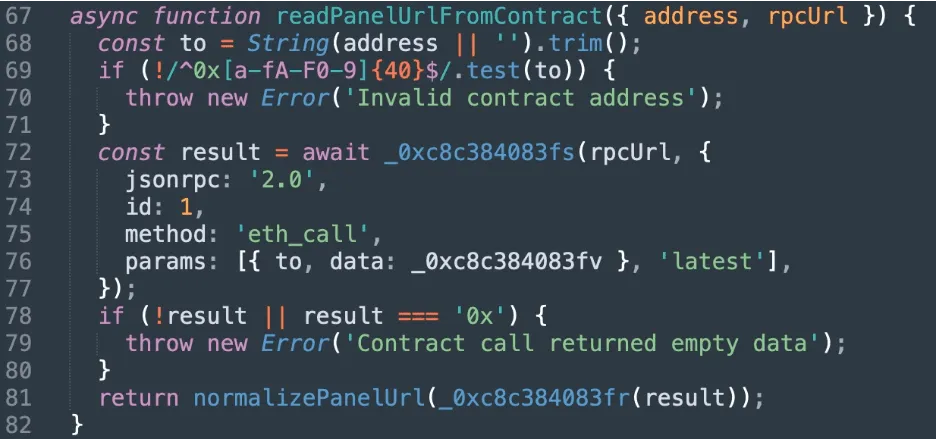 New ChainScript RAT Exploits ClickFix Lures with Blockchain C2 A newly discovered Node.js remote access trojan (RAT) named ChainScript is being deployed through ClickFix social engineering tactics, targeting Windows systems. The malware utilizes a unique command-and-control (C2) discovery method by querying a Polygon blockchain smart contract to dynamically rotate its server…
 Cybercriminals Exploit ChatGPT Custom GPTs for ClickFix RAT Attacks A new ClickFix campaign has been discovered that exploits ChatGPT Custom GPTs to impersonate legitimate products, luring users into executing malicious code. Cybersecurity firm Huntress reported that at least 40 users have been infected, with two confirmed incidents linked to Custom GPT instances. The attackers…