 News.Mit.Edu
MIT Announces New Quantum Systems Laboratory to Propel National Quantum Research
Article Content

- •MIT and Massachusetts announced a $25 million investment for a new Quantum Systems Laboratory.
- •The QSL will combine quantum computers with essential components for advanced research.
- •The initiative aims to establish Massachusetts as a national hub for quantum innovation.
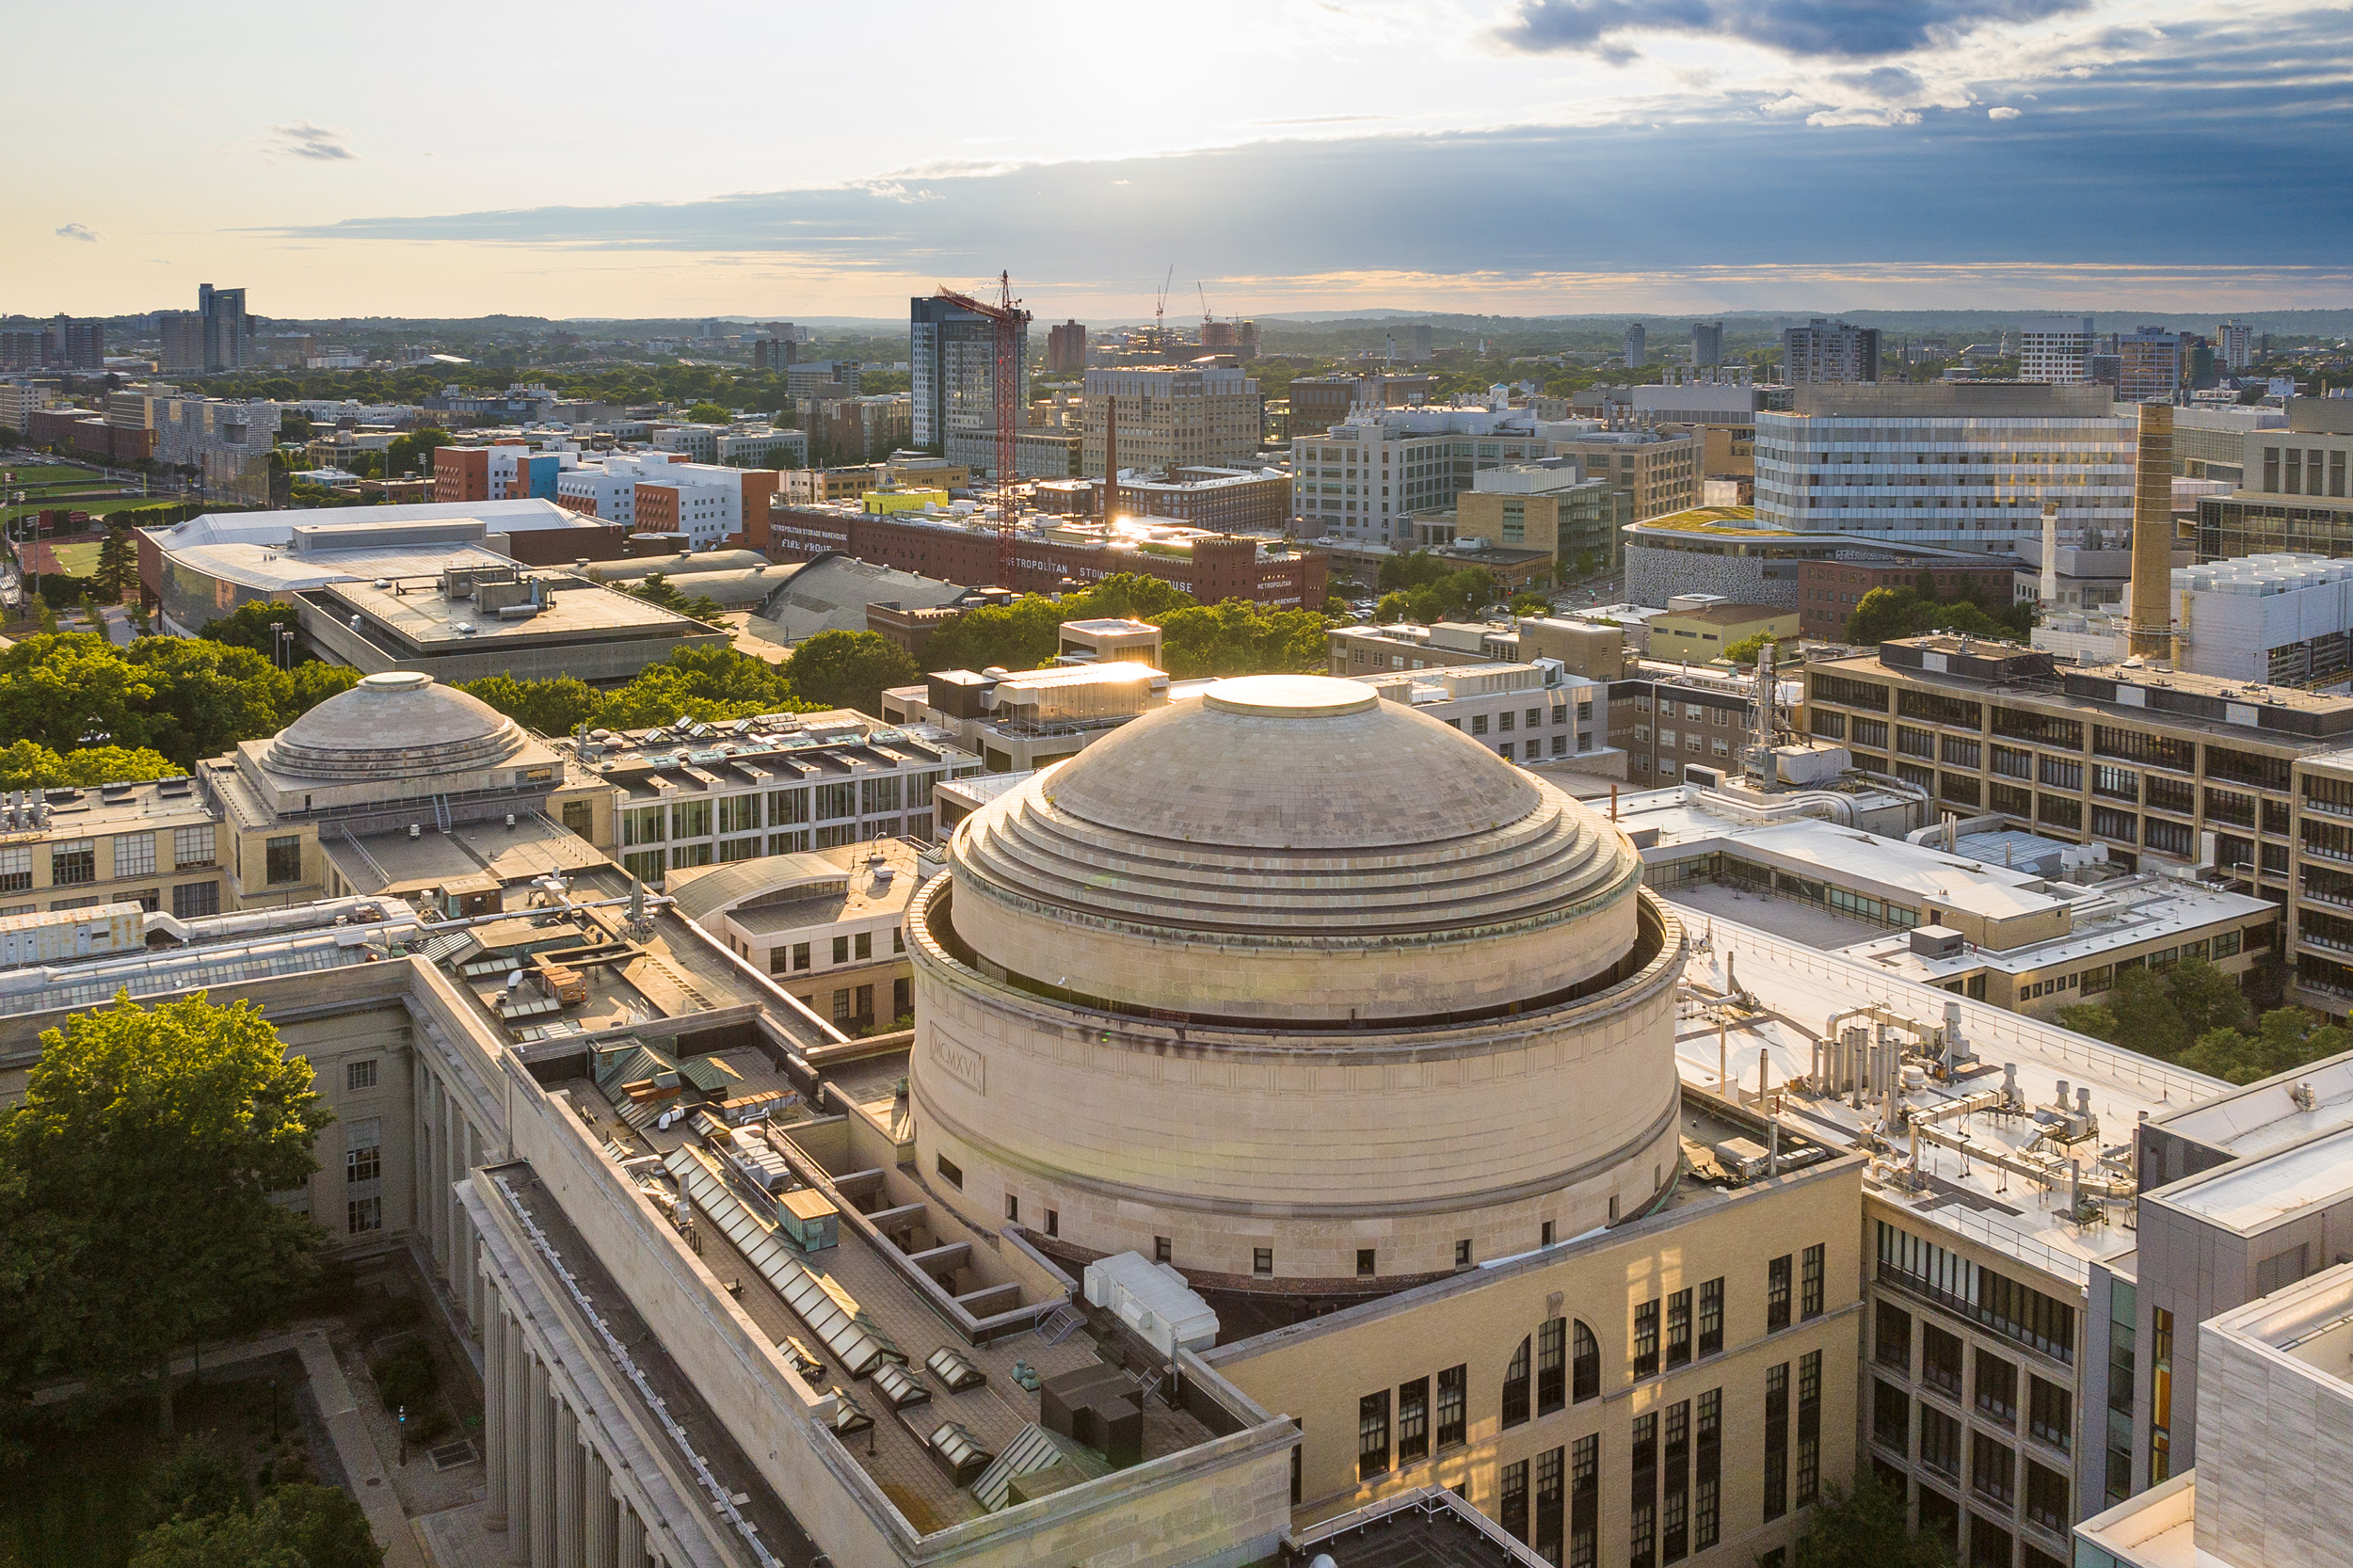
On May 28, 2026, MIT President Sally Kornbluth and Massachusetts Governor Maura Healey announced the establishment of the Quantum Systems Laboratory (QSL) at MIT. This facility aims to accelerate the development of next-generation quantum technologies, positioning Massachusetts as a national hub for quantum innovation. The QSL will combine state-of-the-art quantum computers with essential components like sensors and quantum interconnects, facilitating hands-on research for MIT and external researchers. A $25 million investment from the state will match federal funding for ongoing quantum research at MIT, enabling construction to begin as early as summer 2026. The initiative is part of a broader effort to enhance the region's capabilities in quantum science and technology, which are critical for various industries including computing, security, and health sciences. The facility will also support collaboration between academic and commercial ventures, fostering economic growth and scientific progress.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Continue Reading
 Critical Zero-Day Vulnerability in Cisco Secure Email Gateway Exploited On September 14, 2026, Cisco disclosed a critical SQL injection vulnerability (CVE-2026-76461) in its Secure Email Gateway, allowing unauthenticated remote attackers to execute arbitrary commands with root privileges. This vulnerability arises from insufficient validation in the email parsing logic. Cisco confirmed…
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…