 Lokmattimes
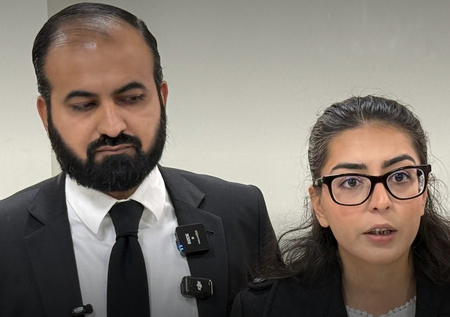
NCCIA Challenges Supreme Court Directive on Lawyers' Sentence Suspension
Article Content

- •NCCIA opposes Supreme Court's directive for expedited hearing on lawyers' sentence suspension.
- •Imaan Zainab Mazari-Hazir and Hadi Ali Chattha were sentenced for social media posts critical of the state.
- •The case has sparked international condemnation and raised concerns over judicial independence in Pakistan.
The National Cyber Crime Investigation Agency (NCCIA) has contested a Supreme Court order from May 12, 2026, which instructed the Islamabad High Court (IHC) to expedite the hearing of suspension pleas for lawyers Imaan Zainab Mazari-Hazir and Hadi Ali Chattha. The couple was sentenced in January 2026 under Pakistan's Prevention of Electronic Crimes Act for critical social media posts. The NCCIA argues that the Supreme Court should not intervene in ongoing high court matters unless extraordinary circumstances exist. The couple's case has drawn international condemnation, with rights groups labeling the trial as politically motivated and a threat to judicial independence. The IHC has yet to rule on the suspension requests, with the NCCIA's recent petition seeking to uphold judicial processes and avoid perceived bias due to the couple's legal profession. The situation reflects broader concerns regarding civic space and legal advocacy in Pakistan.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…