 Securityaffairs.Co
Ransomware Operators Exhibit Predictable Business Hours
Article Content

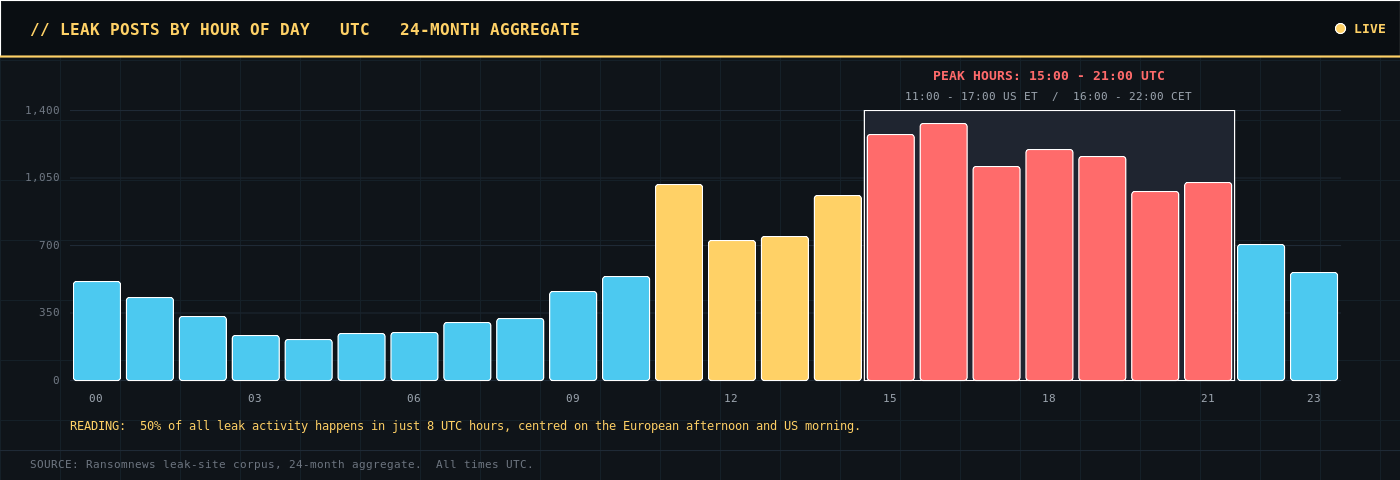
- •Ransomware activity drops 84% during weekdays, peaking in European afternoons.
- •The study analyzed 16,699 posts from 200 ransomware groups over two years.
- •October sees consistent spikes in ransomware activity annually.
An analysis of 16,699 ransomware leak posts over two years reveals that ransomware operators tend to operate during specific business hours, with an 84% drop in activity from Monday to Friday. The data shows peak activity during European afternoon hours and notable spikes in October each year. This trend suggests a level of organization and predictability in ransomware operations, which could be leveraged for defensive strategies. The analysis covers 200 groups and provides insights into the timing of ransomware attacks, offering valuable information for cybersecurity professionals. Understanding these patterns can help organizations better prepare and respond to potential ransomware threats.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Continue Reading
 Critical Zero-Day Vulnerability in Cisco Secure Email Gateway Exploited On September 14, 2026, Cisco disclosed a critical SQL injection vulnerability (CVE-2026-76461) in its Secure Email Gateway, allowing unauthenticated remote attackers to execute arbitrary commands with root privileges. This vulnerability arises from insufficient validation in the email parsing logic. Cisco confirmed…
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…