 www.intellinews.com
Russia's Treaty with South Ossetia Signals De Facto Annexation
Article Content

- •The treaty signed on May 9 allows Russian officials to serve in South Ossetia's government.
- •Georgian opposition parties are condemning the agreement as a new phase of annexation.
- •Marat Kambolov, a Kremlin bureaucrat, has been nominated as South Ossetia's new Prime Minister.
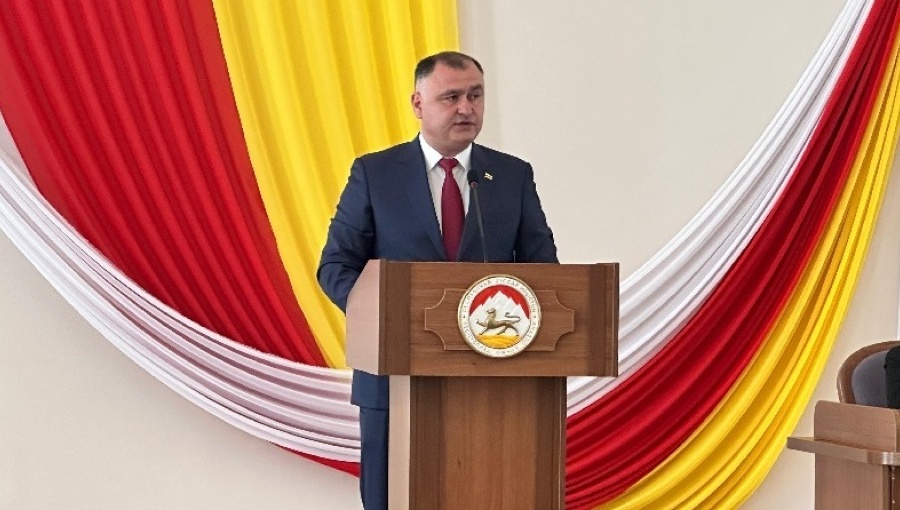
On May 9, 2026, Russian President Vladimir Putin and South Ossetian President Alan Gagloev signed a treaty aimed at deepening ties, which analysts and Georgian officials interpret as a step toward annexation. The treaty allows Russian officials to hold positions in South Ossetia's government and integrates economic and social systems between the two regions. This development follows the resignation of South Ossetia's Prime Minister Dzambolat Tadtoyev, with Marat Kambolov, a Kremlin bureaucrat, nominated as his successor. Georgian opposition leaders have condemned the agreement, calling it a 'new phase of annexation' and accusing the ruling government of inaction. The treaty has been ratified by both parties and is seen as a significant escalation in Russia's control over the region. The situation raises concerns about the future of Georgian sovereignty over South Ossetia and Abkhazia.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…