 Rescana
Salesloft Drift OAuth Token Breach Exposes Salesforce Data
Article Content

- •Over 700 organizations were affected by the breach involving Salesloft's Drift integration with Salesforce.
- •The attackers exploited stolen OAuth tokens to perform unauthorized data exports from Salesforce.
- •Immediate actions included revoking OAuth tokens and removing the Drift integration from the AppExchange.
Between August 9 and August 17, 2025, the threat actor UNC6395 exploited stolen OAuth tokens from Salesloft's Drift integration to access Salesforce environments of over 700 organizations, including major tech firms. The attackers harvested sensitive data, including plaintext AWS keys and VPN credentials, using automated Salesforce Object Query Language (SOQL) queries and bulk exports. The breach was detected on August 19, prompting immediate revocation of OAuth tokens and removal of the Drift integration from the AppExchange. While the immediate threat was contained, the stolen credentials pose a long-term risk. The incident highlights the vulnerabilities associated with over-permissive SaaS integrations and the need for stricter OAuth access controls. Organizations are advised to monitor for anomalous API behavior and review their integration security practices.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Following this threat?
Track Unc6395 and Cloudflare in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
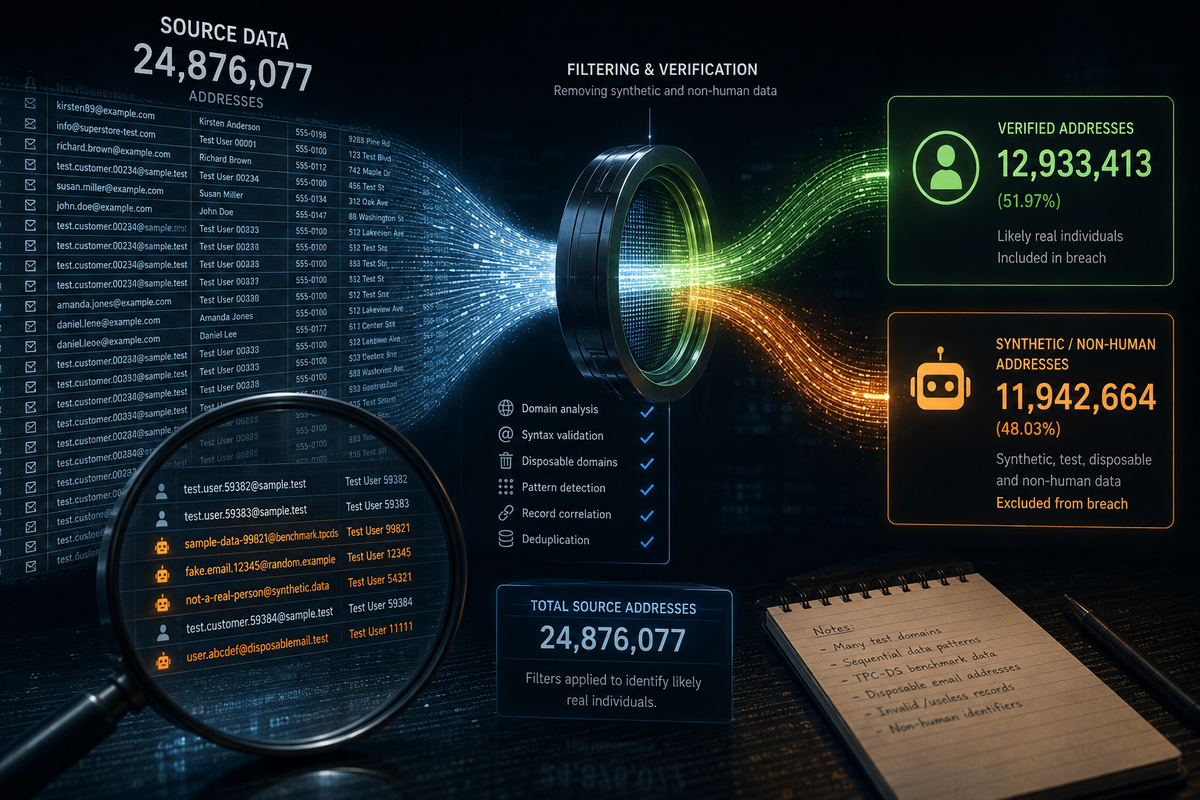 Carhartt Data Breach Exposes 12.9 Million Accounts The ShinyHunters hacking group claims to have compromised Carhartt, stealing sensitive data from nearly 13 million accounts. The breach, which occurred on August 13, 2026, involved over 50GB of data, including customer and employee information. Troy Hunt, founder of Have I Been Pwned, analyzed the leaked data and…
 Exaforce Launches AI Security Tool to Combat Rogue Agents Exaforce has introduced Exaforce AI Security, a platform designed to monitor and control AI agents within enterprise environments. The tool addresses vulnerabilities in enterprise logging that attackers exploit to hide malicious activities under legitimate user actions. Recent incidents have shown how compromised AI…