 News.Ycombinator
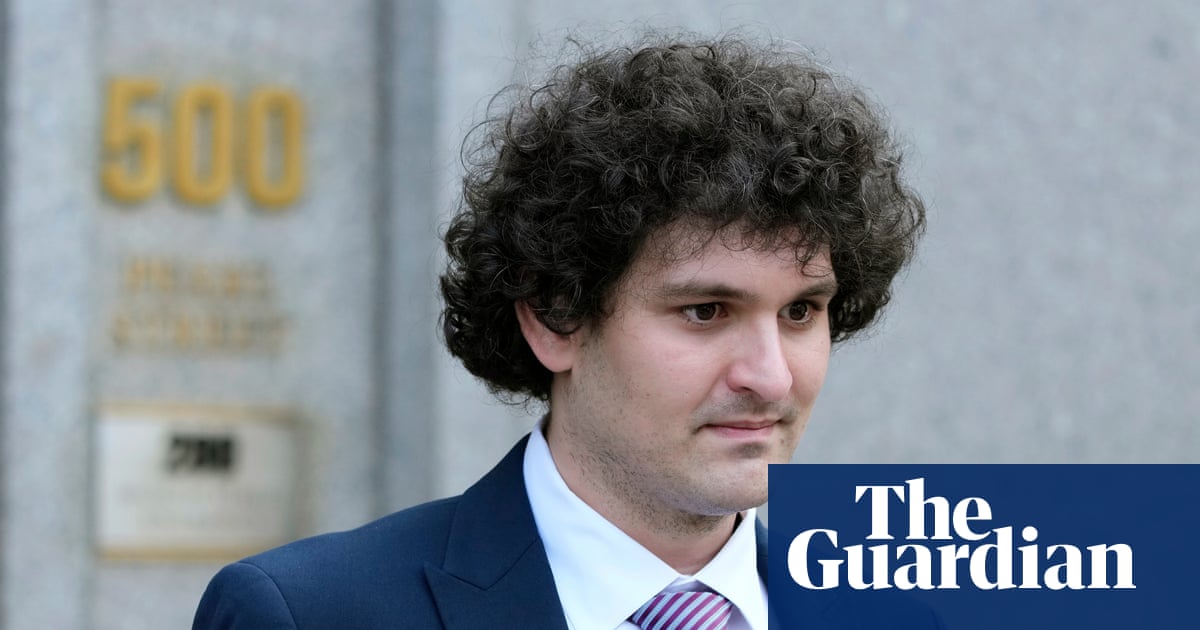
Sam Bankman-Fried Loses Appeal on Fraud Conviction and 25-Year Sentence
Article Content

- •Sam Bankman-Fried's appeal to overturn his 25-year sentence was denied.
- •The court found overwhelming evidence of fraud involving $8 billion in customer funds.
- •Bankman-Fried's potential next steps include further appeals or seeking a presidential pardon.
Sam Bankman-Fried, the founder of the FTX cryptocurrency exchange, lost his appeal to overturn his fraud conviction and 25-year prison sentence. A three-judge panel from the 2nd U.S. Circuit Court of Appeals upheld the conviction, citing robust evidence of his fraudulent activities. Prosecutors revealed that Bankman-Fried misused $8 billion of customer funds for personal expenses while assuring stakeholders of FTX's financial safety. His defense argued that he was wrongly prevented from presenting evidence to support his case. The court's ruling confirmed that Bankman-Fried's actions constituted one of the largest financial frauds in U.S. history. He is currently serving his sentence at a federal prison in California, with eligibility for release in 2044. He may seek further appeals or a presidential pardon.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Alameda Research in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…