 Businesstimes.Sg
Singapore Launches Initiatives to Enhance AI Adoption and Cyber Resilience for SMEs
Article Content

- •Singapore's new initiatives aim to support 12,000 SMEs in AI adoption and cybersecurity.
- •Over 80% of organizations in Singapore experience annual cybersecurity incidents.
- •The SME AI Impact Awards will recognize businesses achieving measurable AI outcomes.
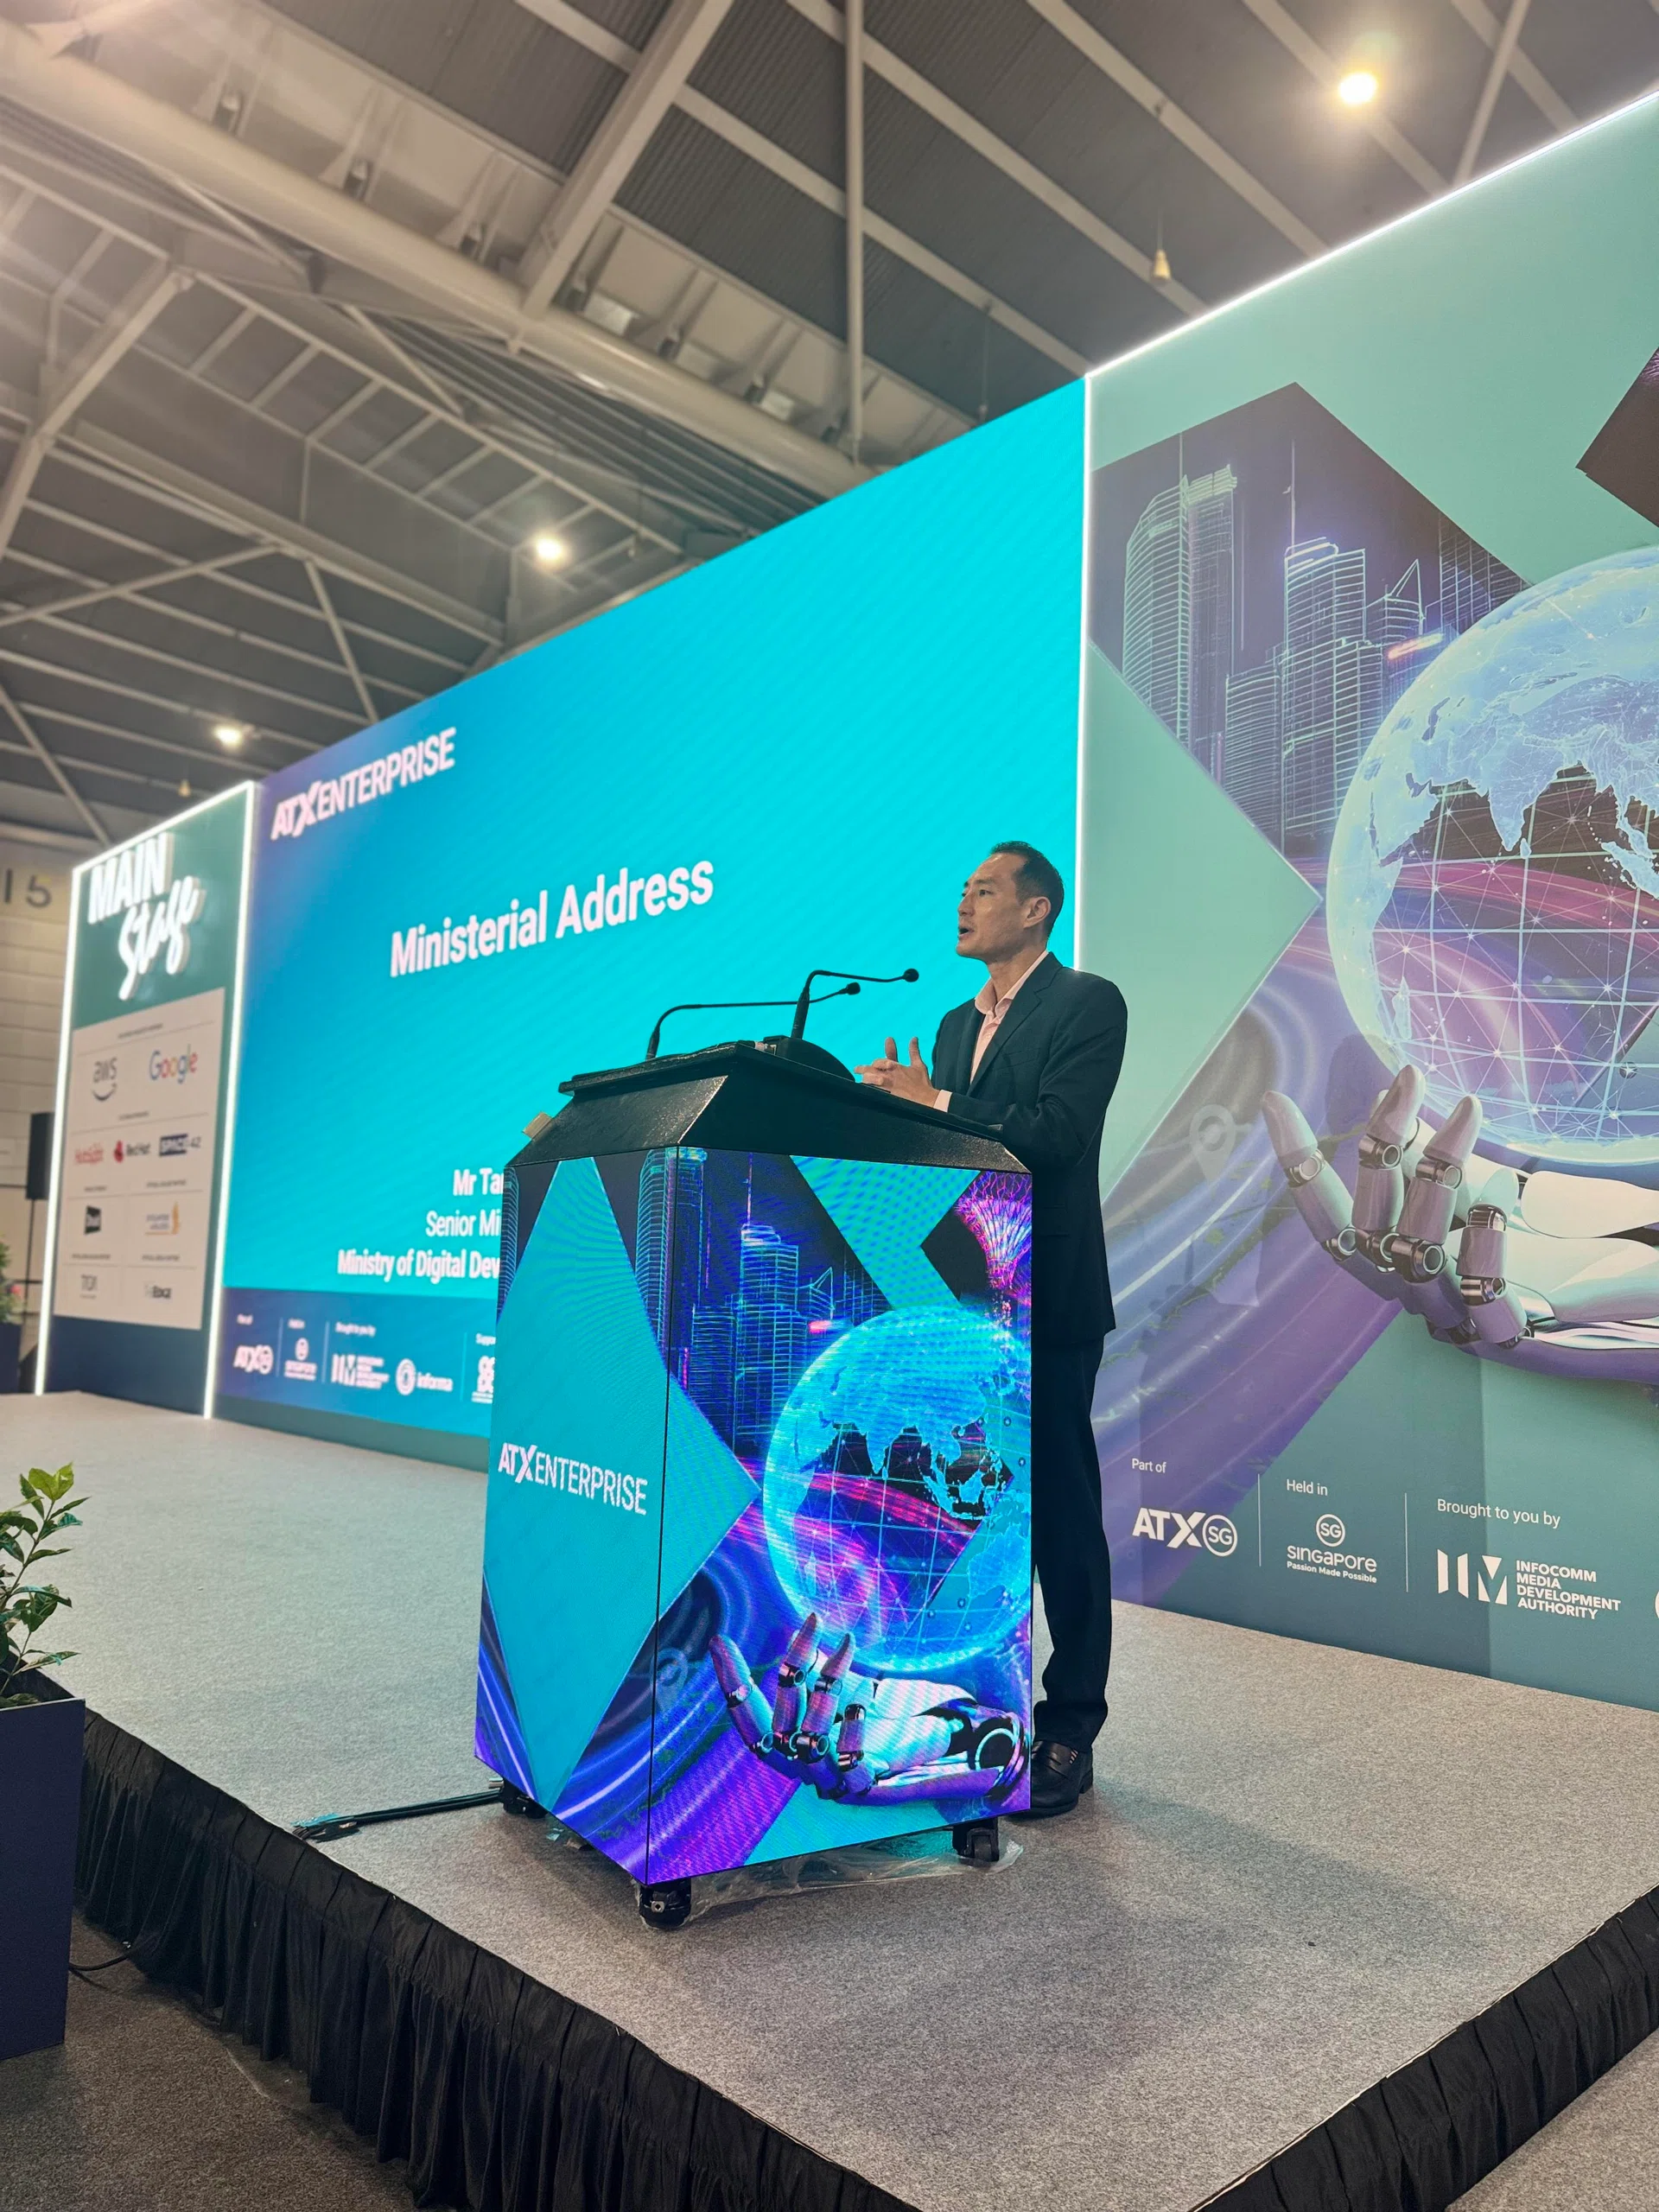
On May 21, 2026, Singapore announced new initiatives to bolster AI adoption and cybersecurity among small and medium enterprises (SMEs) at the ATxEnterprise 2026 event. Senior Minister Tan Kiat How highlighted that over 80% of organizations face annual cybersecurity incidents, necessitating stronger digital resilience. The Infocomm Media Development Authority (IMDA) introduced partnerships with Grab and RSM Stone Forest IT to support 12,000 SMEs through targeted programs. Grab will implement the Grab AI Programme, offering training and resources to 10,000 SMEs in the food and beverage, e-commerce, and retail sectors. RSM will launch the Cyber2SME Programme, providing phishing simulations and training to enhance cyber defenses for 2,000 SMEs. The inaugural SME AI Impact Awards will recognize SMEs achieving significant outcomes through AI, with nominations opening on June 1, 2026. These initiatives aim to ensure no SME is left behind in the digital transformation journey.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (9)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…