 Unn.Ua
Sweden Launches Military Satellite for Russian Surveillance Amid Rising Tensions
Article Content

- •Sweden's first military satellite launched for reconnaissance over Russia.
- •Plans to deploy a total of ten military satellites within two years.
- •Increased independent intelligence capabilities amid NATO membership.
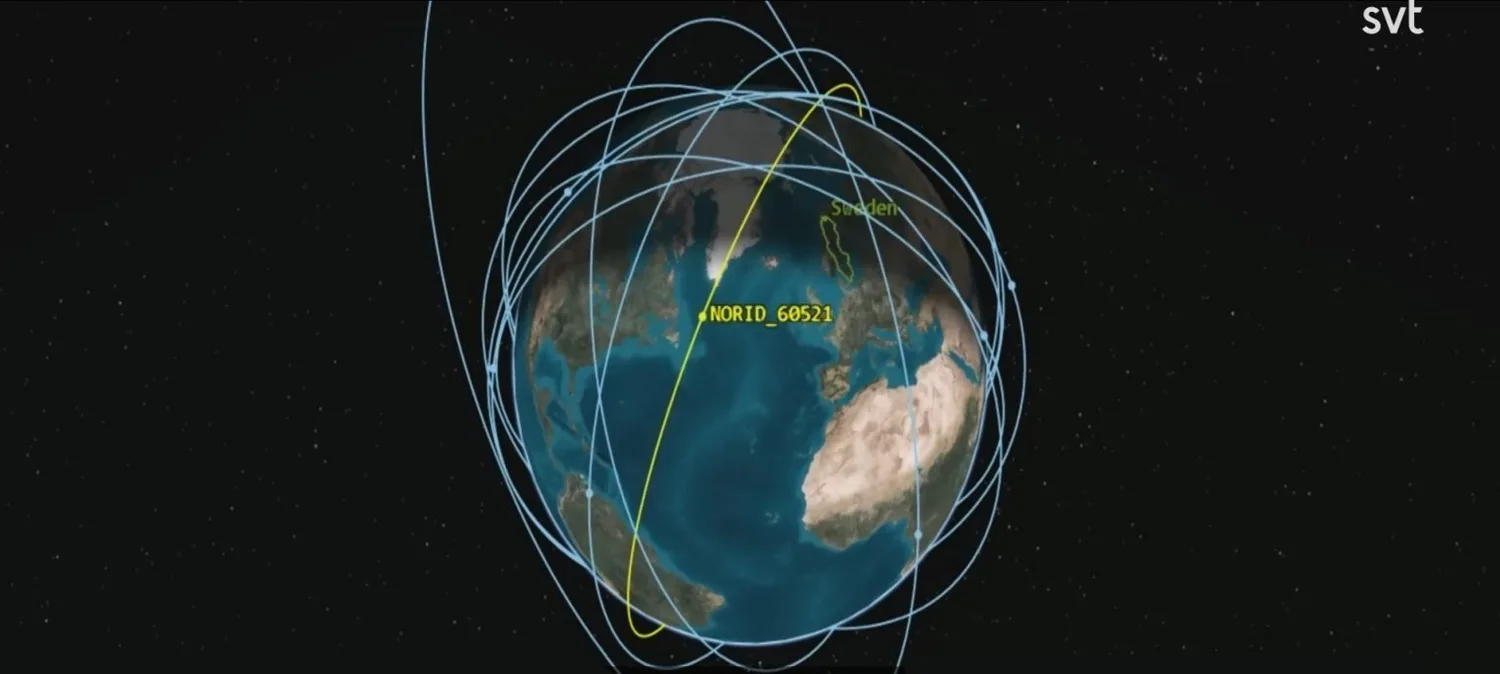
On May 3, 2026, Sweden successfully launched its first military satellite from Vandenberg Space Force Base, in collaboration with SpaceX. This satellite is designed for reconnaissance and surveillance of military targets within Russian territory and is part of a broader initiative to establish a constellation of approximately ten military satellites over the next two years. The satellite will enhance Sweden's independent intelligence capabilities, which previously relied on commercial sources and allies. Anders Sundeman, head of the Space Division, emphasized the urgent need for high-precision targeting data due to Sweden's NATO membership and the acquisition of long-range weaponry. The satellite will take about one month to reach its operational orbit and will be managed from the Space Operations Center in Uppsala. This launch comes amid heightened security concerns in the region, particularly following the destruction of a Russian satellite due to orbital debris. The satellite will aid in monitoring military facilities and detecting troop movements.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (8)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…